
AI pentesting that reads your code and proves what's actually exploitable
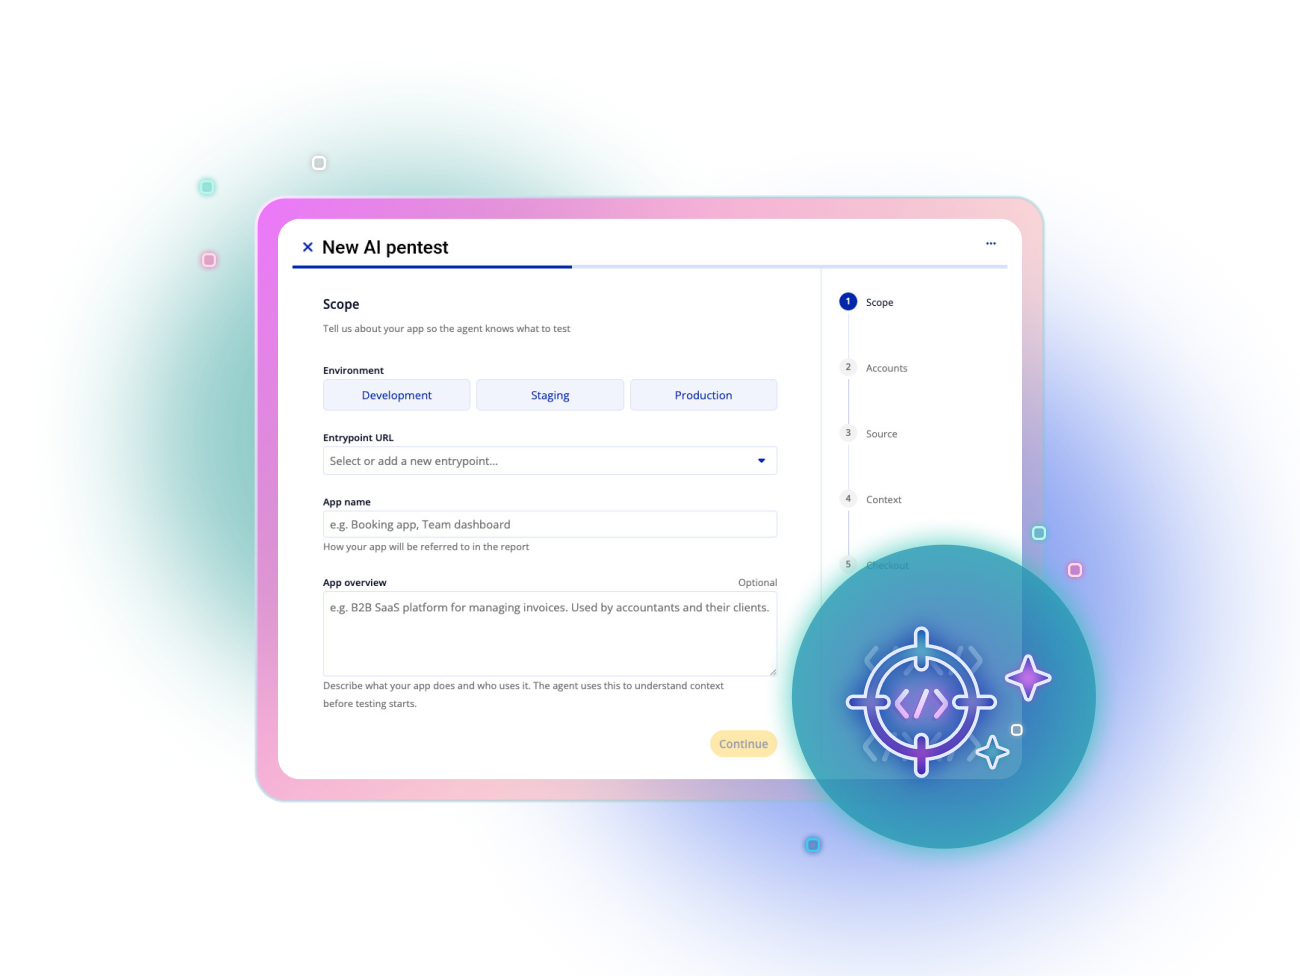
Intruder's AI agents test your web apps on demand with white box access to your repo, and a compliance-ready report lands in hours. Run one on every major release.
Join 3,000+ companies securing their attack surface with Intruder






The depth a manual pentest can miss
AI SAST across your repo lets the agents use your code to go deeper than a human tester can. They have found issues that survived multiple years of annual penetration tests.
Results in hours, not weeks
Scope a test and the agents start straight away. A full report lands in hours, not the weeks a manual engagement takes to schedule and run.
A pentest budget that goes further
An AI pentest costs a fraction of a manual engagement. Instead of one assessment a year, you can run one whenever you need it.
Keep security and engineering in lockstep
From repo to runtime, in one test

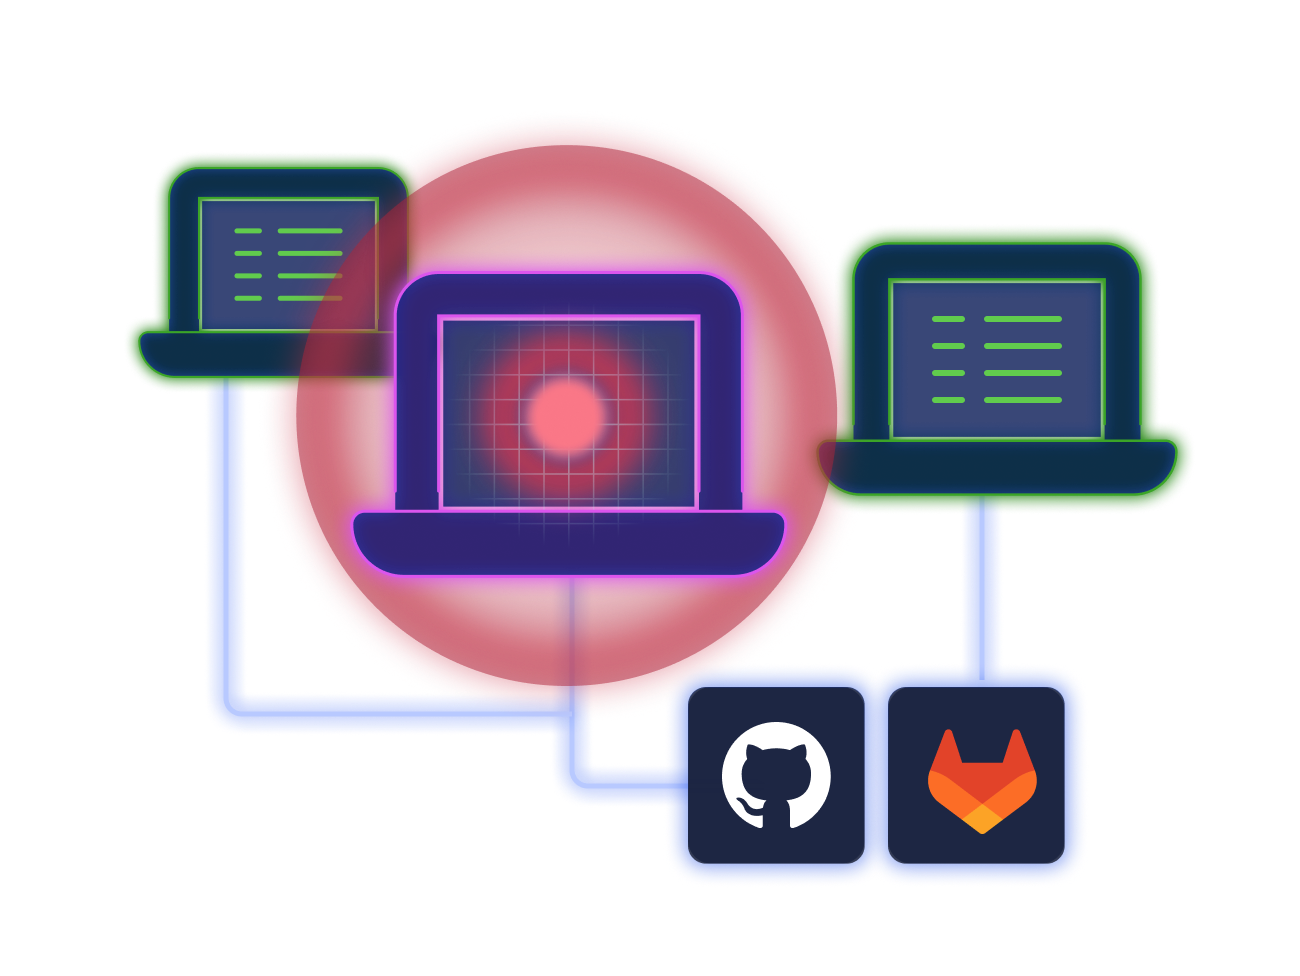
Connect your GitHub or GitLab repo and the agents run AI SAST across your source, then test each finding against the running app to prove what they found. That white box view is what gives the test its depth, reaching issues a once-a-year manual engagement can miss.
Separate exploitable issues from theoretical ones
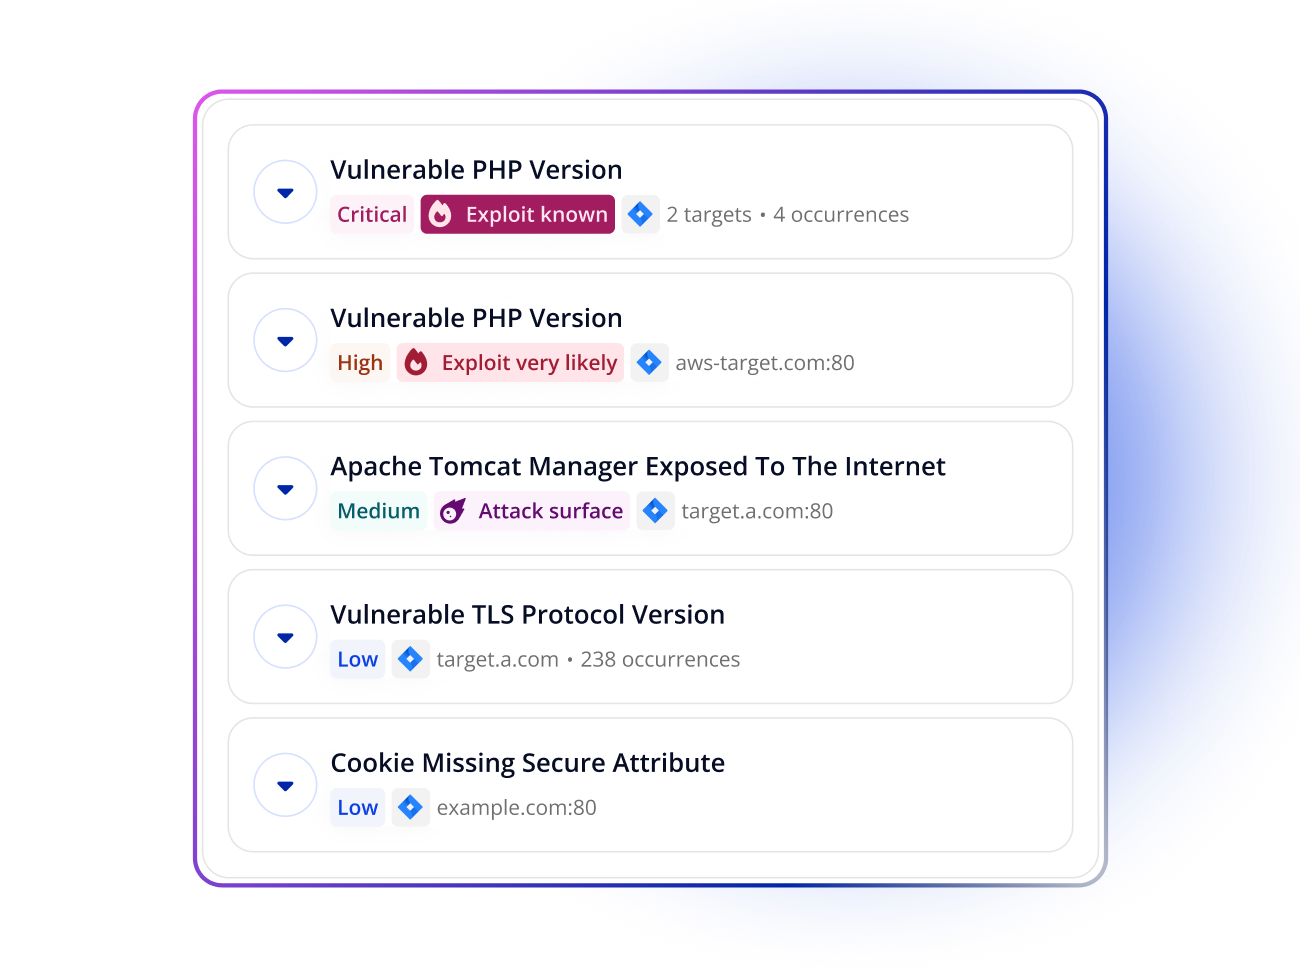
The agents investigate each finding the way an experienced pentester would, running the exploit against your app to confirm it works before it is ever reported. You get proof-of-concept code with it, so your team can reproduce the issue rather than take our word for it.
Get a report you can act on in hours
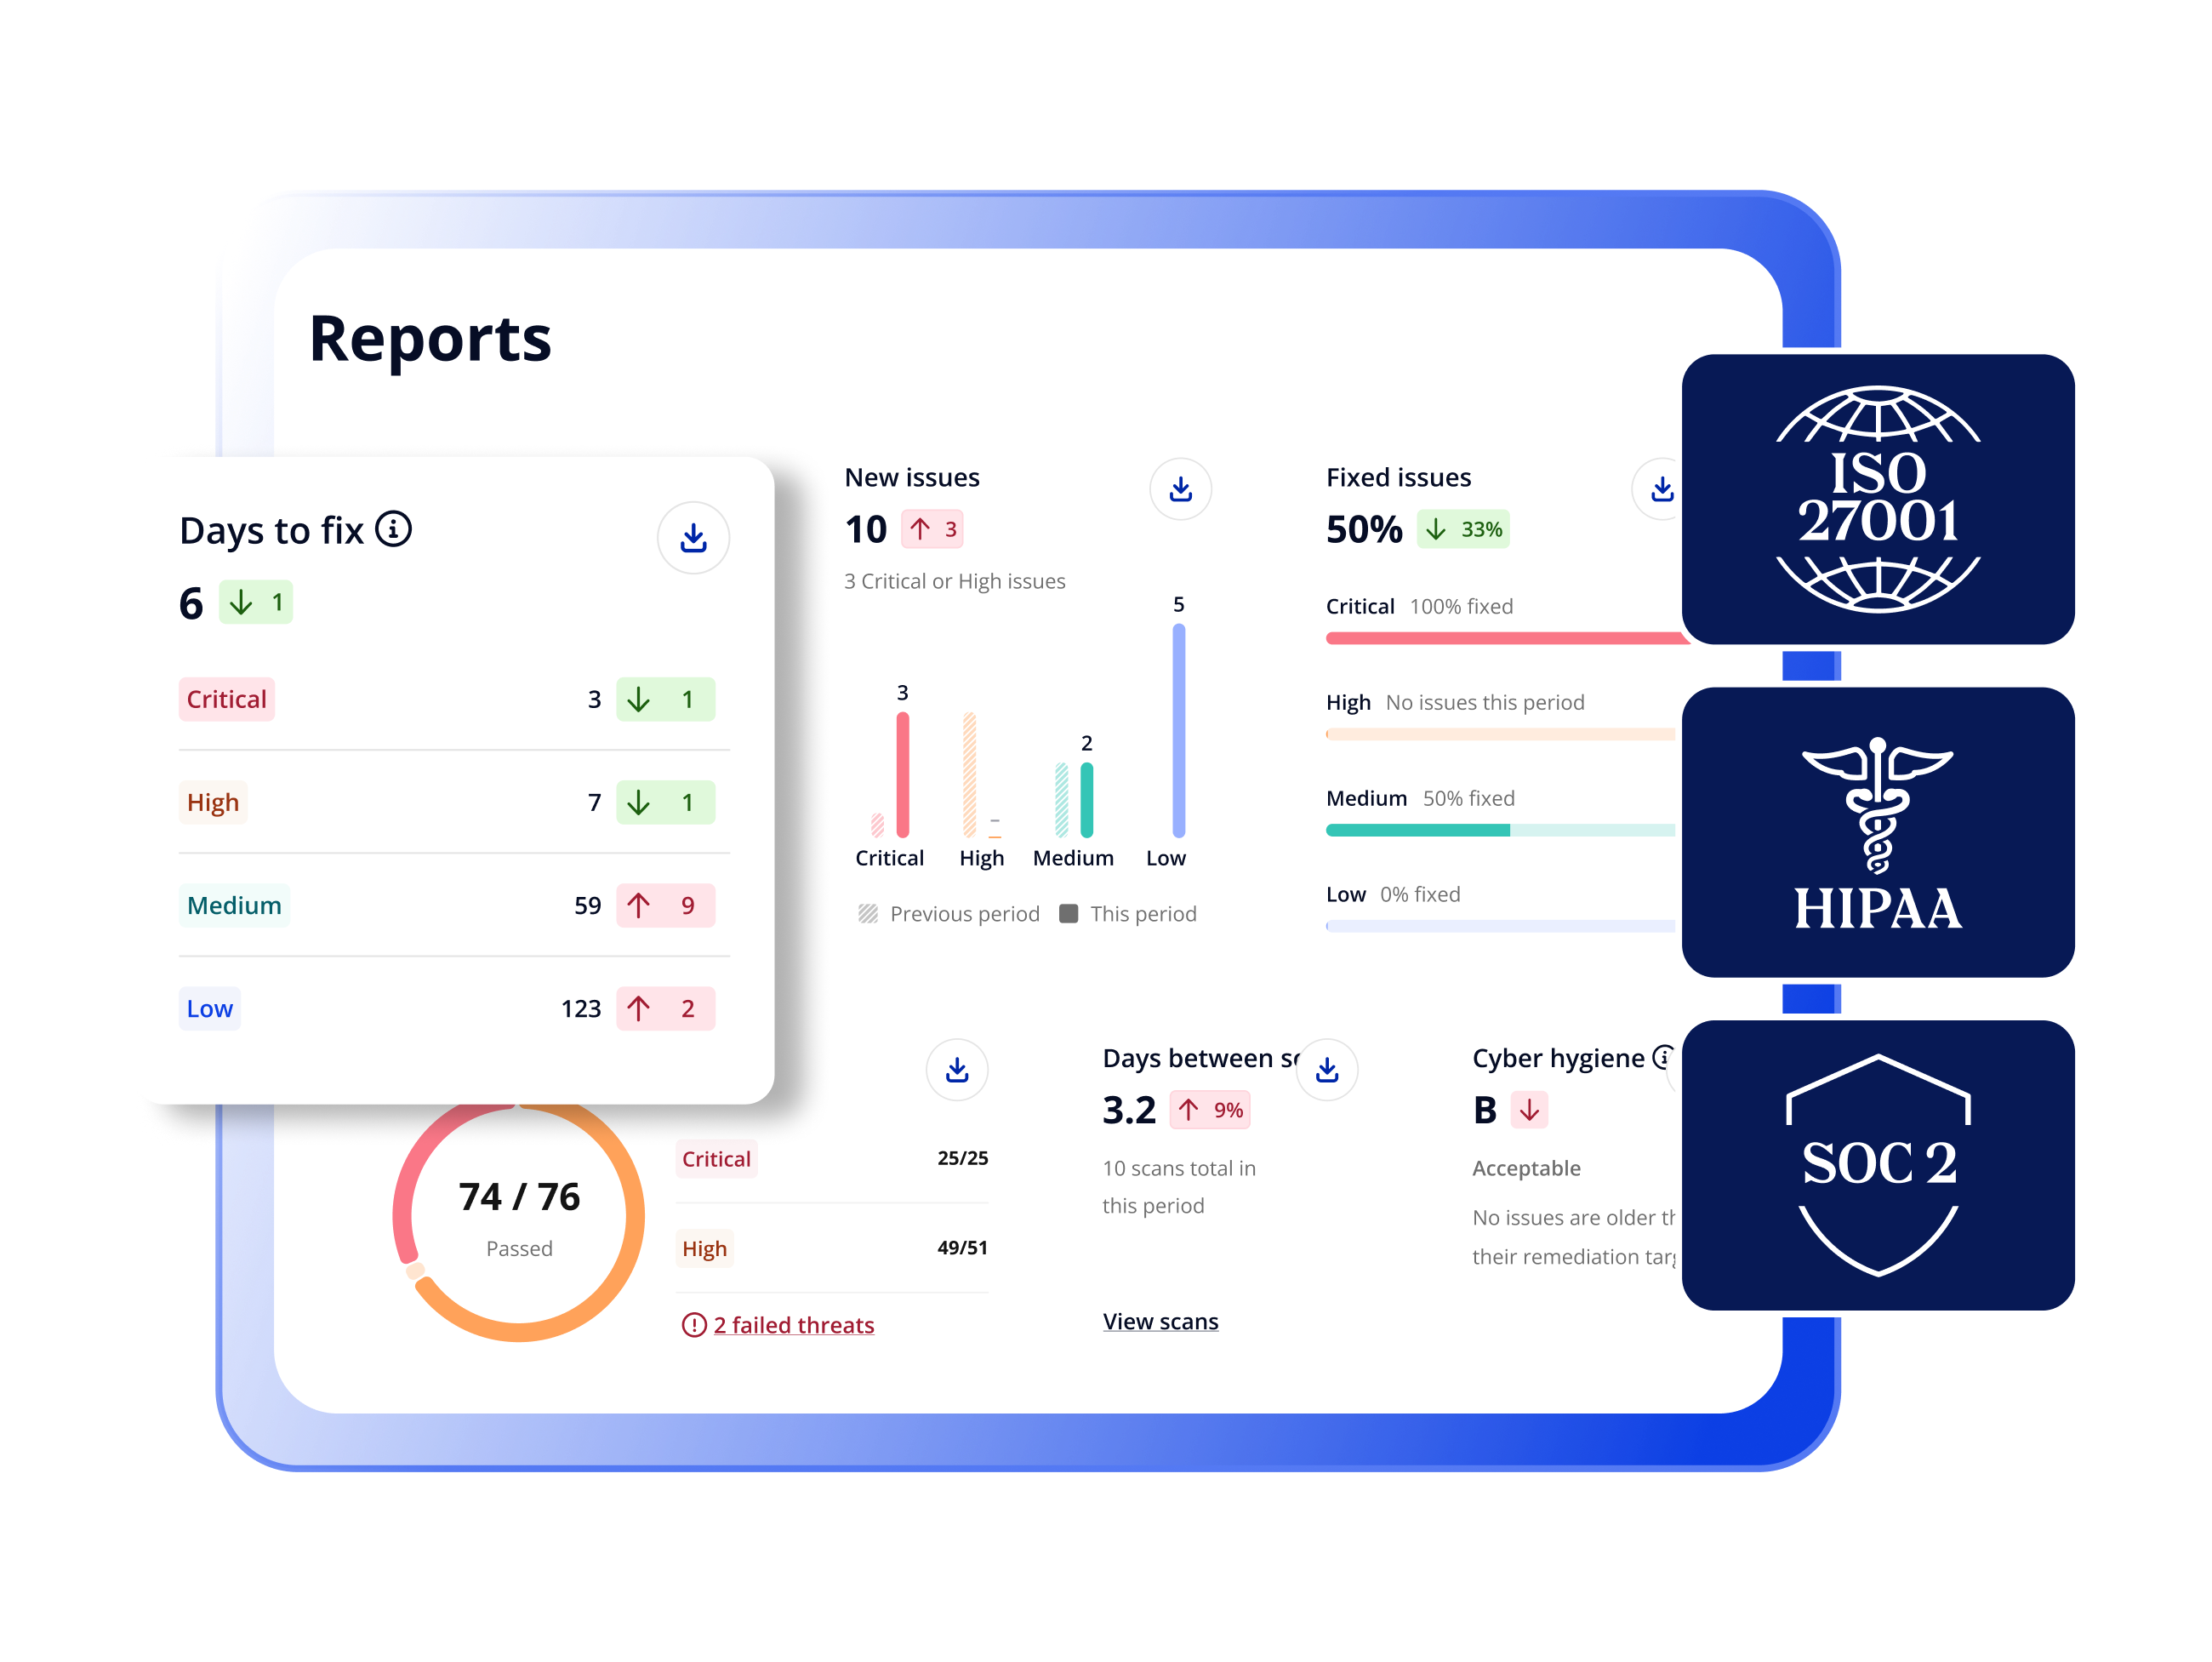
You get a summary, the detailed findings with the exact line of code behind each one, and a full transcript of every step the agent took, so you and your auditor can see exactly what was tested and what it found.

Find what's exposed, fix what matters, and stay ahead of new threats

External Scanning
Infrastructure Security

Attack Surface Monitoring
Respond to changes

CSPM
Daily cloud config checks

DAST
Secure web apps

Risk Based Prioritization
No more alert fatigue

Cyber Hygiene Reporting
Demonstrate progress

Emerging Threat Detection
Check and act fast

Asset Discovery
Reveal unknown targets

Secrets Detection
Prevent leaked credentials

Website Security
140k+ checks

Container Image Scanning
Automated image discovery

API Security
Test your APIs

Compliance
SOC 2, ISO, HIPAA, DORA

Internal Scanning
Secure employee devices
Our customers love Intruder




Security that works for the 99%. Pricing that does too.

Free


Pro
Sign up for your free 14-day trial
AI SAST means using AI agents to analyze source code for security weaknesses instead of matching it against fixed rules. Intruder runs that analysis as part of a penetration test: the agents read your codebase, then prove what's exploitable against your running app.
White box. The agents get your source code and, when you supply them, working credentials, which is the deepest access a pentest can have. Grey box testing works from credentials and partial knowledge without the code, so it cannot trace a flaw back to the line that caused it.
Full AI web app pentests are bought per test, so you can run as many as you need rather than being capped by plan. See our AI pentest pricing for current rates. Separately, issue-level AI Pentest investigations, which validate individual scanner findings, run on monthly credits by plan: 5 on Cloud, 10 on Pro, and 50 on Enterprise.