


Key Points
We've summarized the essential pentesting tools to aid pentesting pros, plus the newer AI-driven tools for teams looking for automated assessments.
TL;DR
Best manual pentesting tools
- Kali Linux
- Nmap
- Metasploit
- SQLmap
- Burp Suite
Best automated pentesting tools
- Intruder
- Strix
- XBOW
- Escape
- AWS Security Agent
5 top manual pentesting tools
When it comes to professional penetration testing, a human tester will use specialist software like network sniffers or password crackers. There are many to consider, but here are our top picks for IT professionals taking their first steps into manual pen testing, including open-source tools and paid pentesting tools.
1. Kali Linux
Kali Linux is an operating system built specifically for penetration testers. It comes bundled with approximately 600 tools for reconnaissance, discovery and exploitation of vulnerabilities, post-exploitation, forensics, and more.

Pros
- Pre-installed toolset: Having these tools pre-installed and automatically maintained means pentesters can spend more time focused on their engagements.
- Community and support: Kali Linux has a large community of users and developers, which means there's extensive documentation, tutorials, and forums available for support.
Cons
- Not best for customizing: Can be customized, but is best used out of the box. Installing additional tools can be challenging without corrupting the build, so building your own Linux-based OS is preferable for more advanced users.
Pricing
Free
2. Nmap
Nmap (short for network mapper), initially released in 1997, is the tried and tested penetration testing tool for reconnaissance and network security scanning. Nmap's probes let testers discover hosts and services within computer networks. Once identified, Nmap's scripting engine and version identification capabilities will give testers the ability to map out a network's attack surface, which will then direct exploitation efforts.

Pros
- Fast: It's generally very quick and efficient to run scans with Nmap, including for large networks.
- Highly configurable: Nmap offers extensive configurations and its own scripting engine, so you can tailor it to meet your specific requirements.
- Compatible: Nmap works on all major operating systems, including Windows, Linux, and macOS.
Cons
- No GUI: Nmap is primarily a command line tool. Though there are GUI versions available (Zenmap), it still requires users to read and understand various port scanning flags, and the GUI does not add significant value or ease of use.
Pricing
Free
3. Metasploit
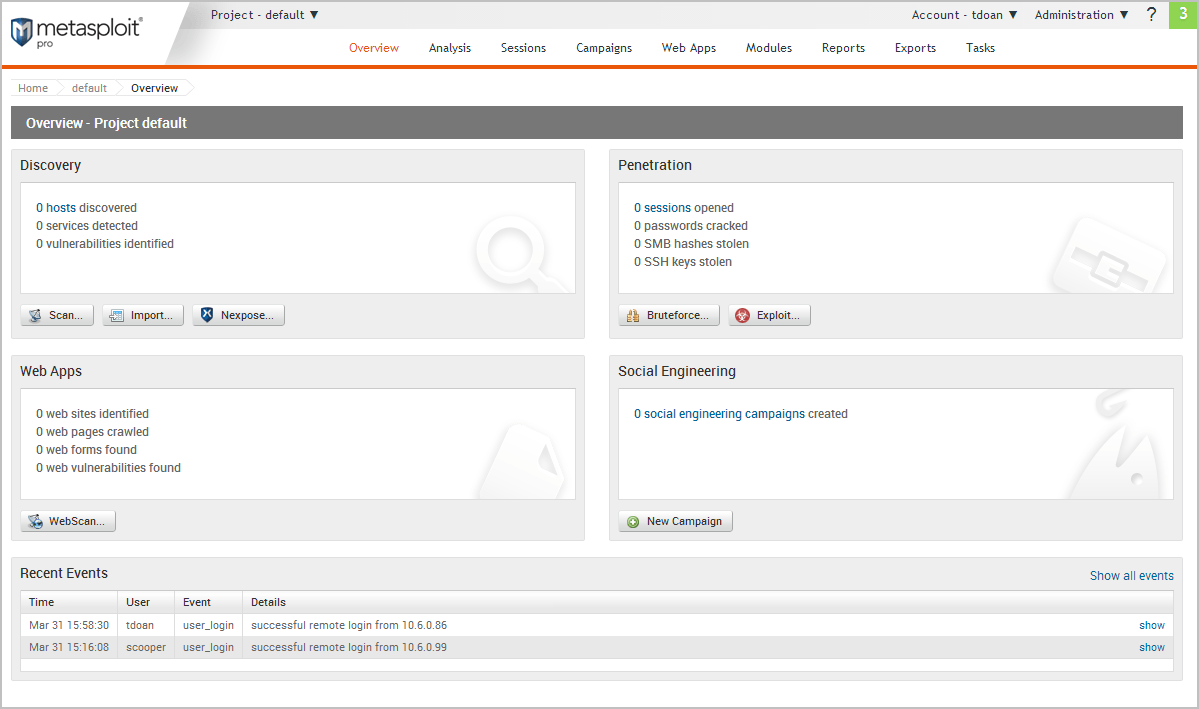
Metasploit is a platform of penetration testing tools and modules for conducting offensive operations. The framework allows testers to carry out vulnerability scans, search for and launch exploits, and manage compromised systems, including a wide range of tools for post-exploitation activities.
Pros
- Exploit database: Metasploit provides a vast database of exploits, payloads, and tools for developing and executing exploits.
- Integrations: It integrates well with other tools and can be extended with custom modules and scripts, making it highly flexible.
- Ease of use: It has both a command-line interface and a graphical user interface (Pro version), making it accessible to both beginners and experienced users.
Cons
- Limited documentation: Certain modules or features are not well-documented, which can make it challenging to implement more advanced functionalities.
- Not always up to date: Metasploit's exploit database is not always up to date, so sometimes users must source the latest exploits from elsewhere.
Pricing
- Free version available
- Pro version (price available on request)
4. SQLmap
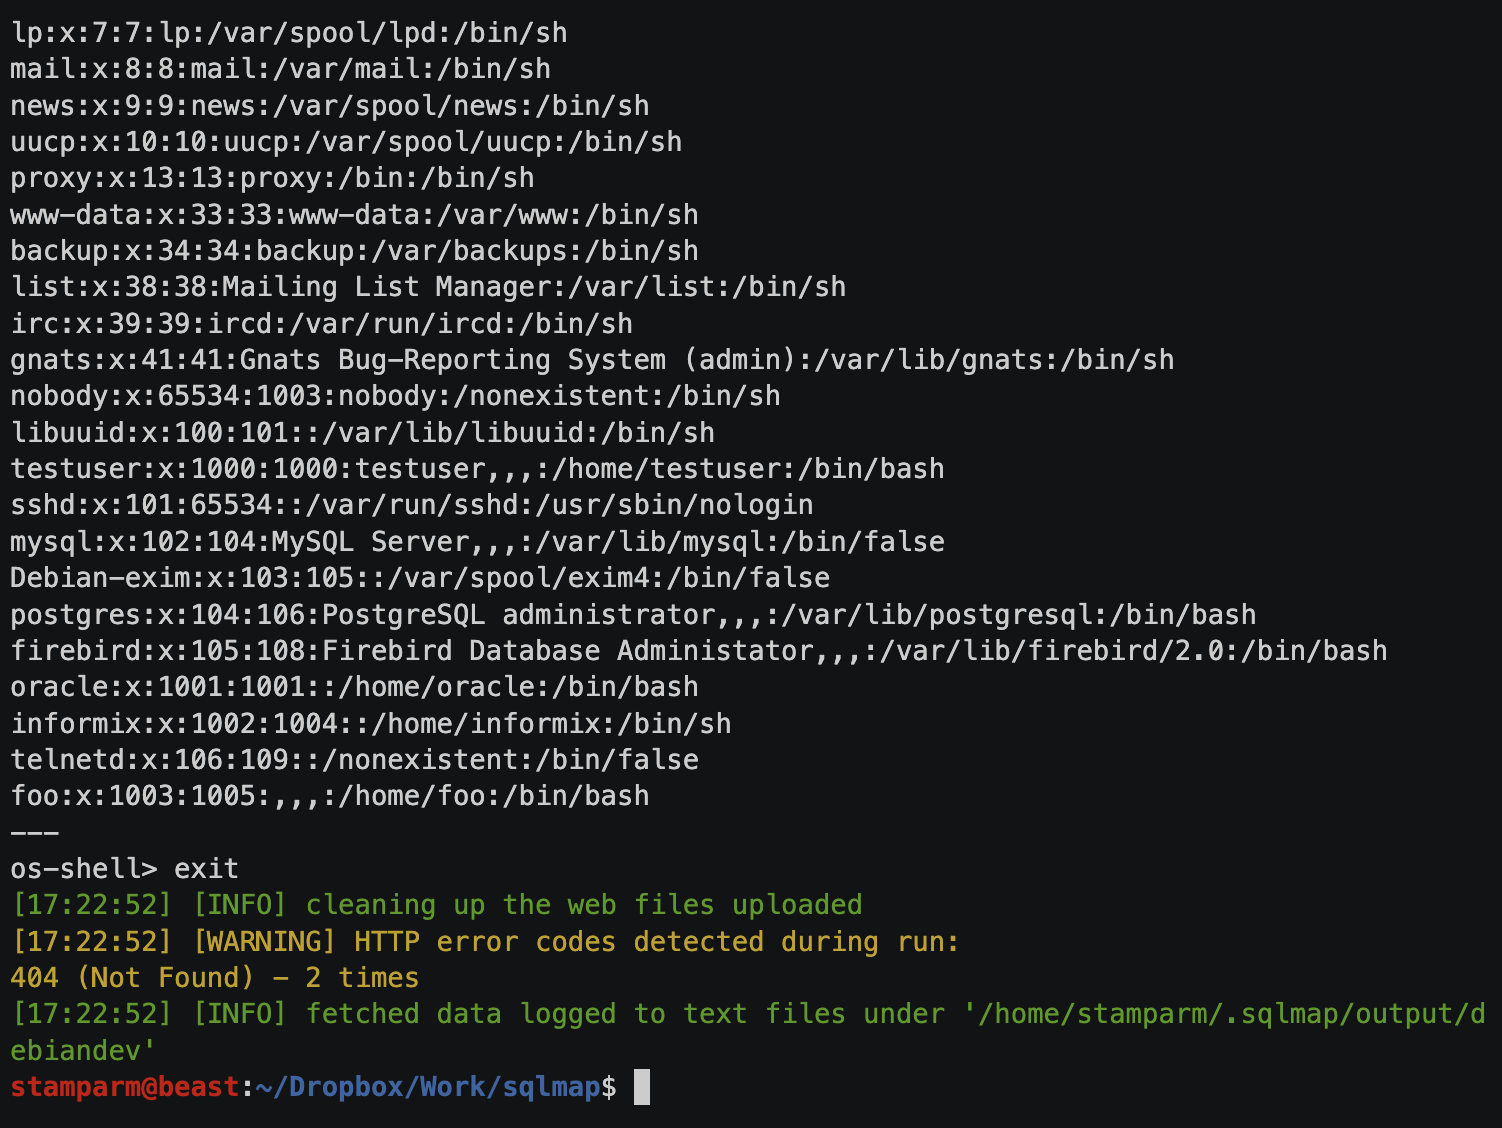
SQLmap is a pentesting tool for automatically detecting and exploiting SQL injection vulnerabilities in web applications. It automates away the nitty-gritty complexities and allows testers to focus on getting impactful results through the extraction, querying and modification of compromised databases.
Pros
- Find vulnerabilities quickly: SQLmap automates the process of detecting and exploiting SQL injection flaws, which helps users find vulnerabilities quickly.
- Support for multiple databases: It supports a wide range of databases, including MySQL, Oracle, PostgreSQL, Microsoft SQL Server, and more.
- Automated exploitation: SQLmap can automate complex exploitation to extract information from a database which would otherwise require writing custom scripts. For example, extracting a database's contents via a Blind SQL injection weakness.
Cons
- Manual verification required: SQLmap may sometimes produce false positives or miss complex vulnerabilities, requiring manual verification.
- Limited scope: SQLmap's crawling capabilities are limited, and it's best used against an endpoint which already appears vulnerable. As such, it's usually required to chain multiple tools, and use another tool to crawl/spider a site and pass off interesting requests for further scanning.
Pricing
Free
5. Burp Suite
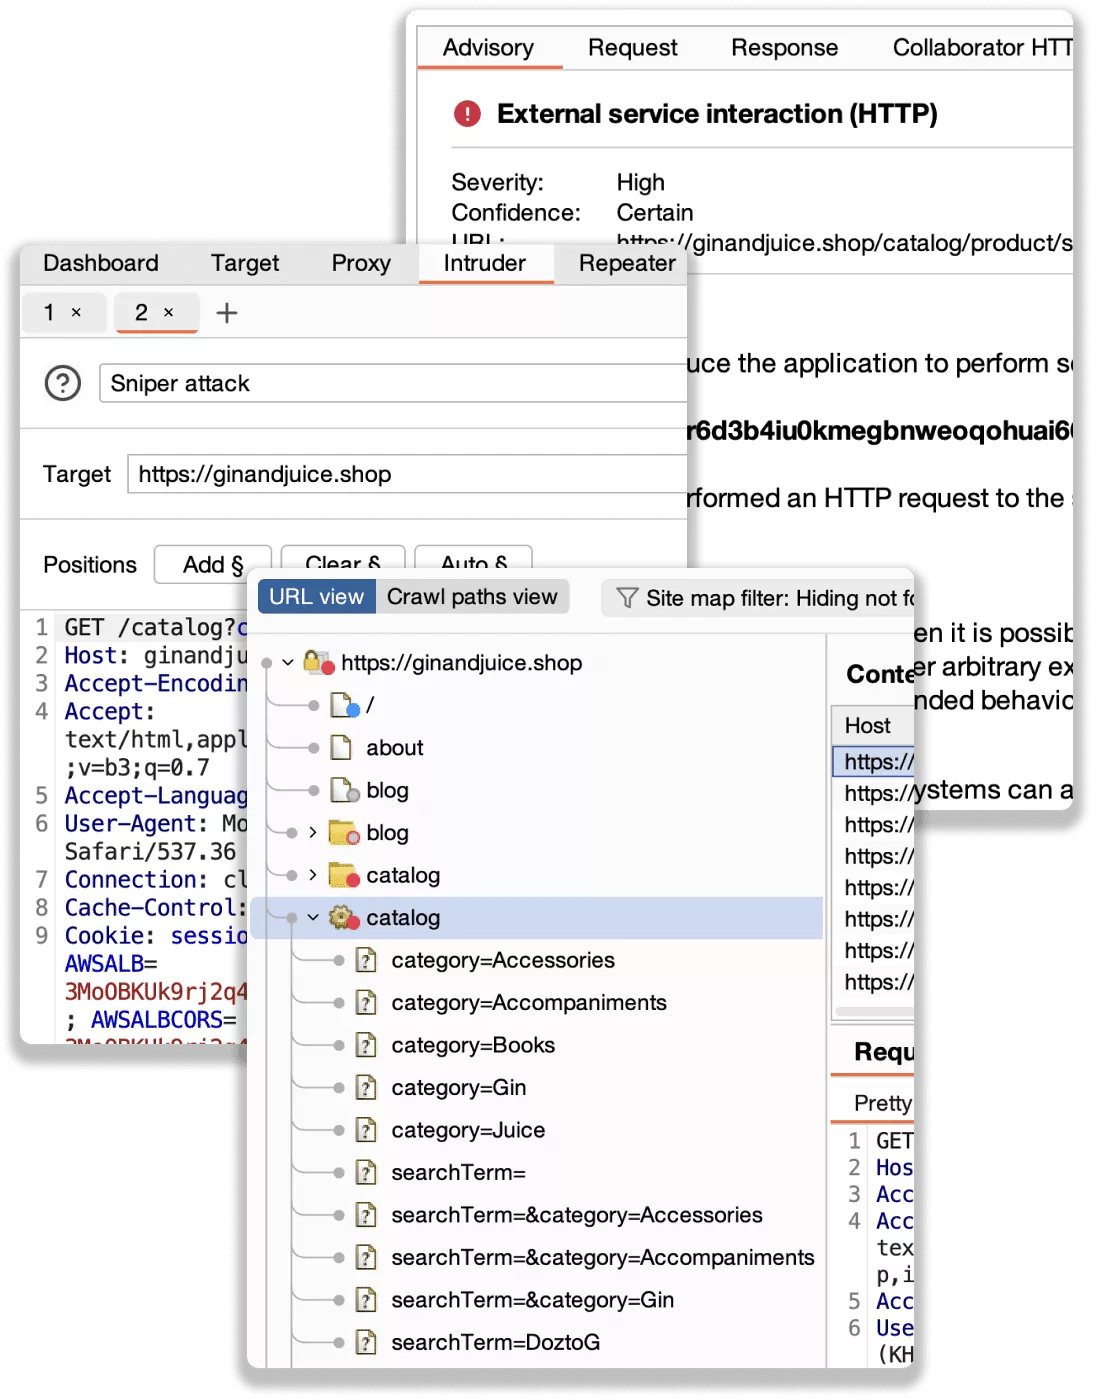
Burp Suite is an attack proxy and vulnerability scanner used to carry out web application security assessments. Burp allows testers to map out applications, carry out automated scans and identify weaknesses through the interception and replaying of web traffic. Augmenting this is a wide library of free and paid extensions which can be passively or actively used to help the tester discover vulnerabilities.
Pros
- Automations: Burp Suite's Pro plan offers a range of automations that can detect a wide range of weaknesses.
- Plugins: Users can install a wide range of plugins from the Burp Suite BApp Store to extend its capabilities.
- User-friendly: The tool provides a graphical interface that is easy to navigate.
Cons
- Paywall: Burp Suite's most useful features are available only on the Professional subscription, which is not free.
Pricing
- Burp Suite Community Edition is free
- Burp Suite Professional subscription starts at $449 for one user
Manual vs. AI pentesting
AI pentesting tools hand the test itself to agents. They map the application, decide what to probe, and attempt exploitation, with no tester directing each step. Our deep dive on AI pentesting covers how they work in more detail.
5 best automated pentesting tools
The five pentesting tools below run the full test on their own and only report findings they've confirmed with a working exploit. For the full breakdown, see our complete list of AI pentesting tools.
1. Intruder
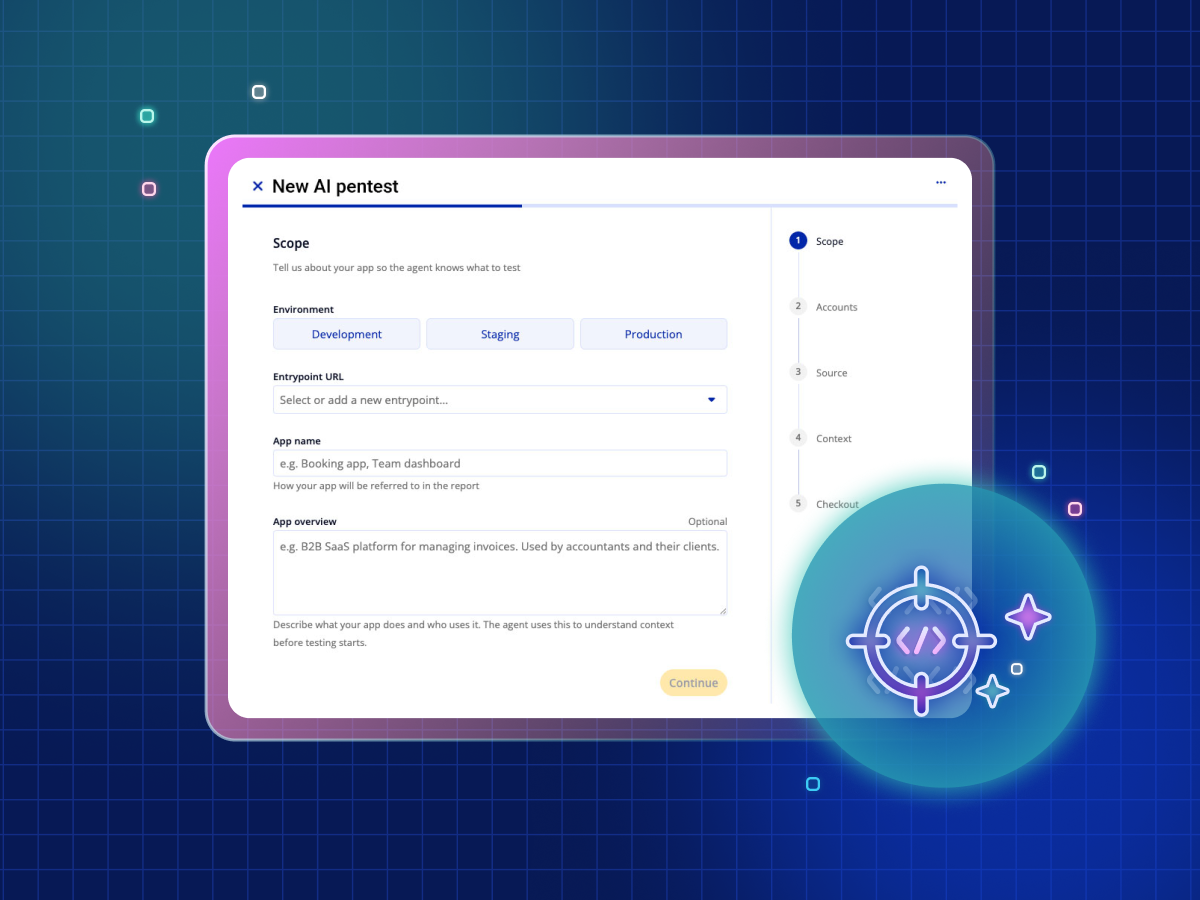
Intruder runs AI pentesting agents against web applications and their APIs on demand. The agents connect to your GitHub or GitLab repo and read your source code directly, then chain smaller weaknesses into serious exploits and validate each one against the live application. They’re built by Intruder's in-house CREST and OSCP-certified pentesters, and findings pinpoint the vulnerable code by file and line number.
2. Strix
Strix is an open-source, agentic security platform that coordinates specialized agents across reconnaissance, exploitation, and validation, covering internal apps and infrastructure as well as web apps. Every finding is validated with a working proof-of-concept exploit, and confirmed issues come back as ready-to-merge pull requests. You can also choose which AI model powers the agents and switch providers whenever you want.

3. XBOW
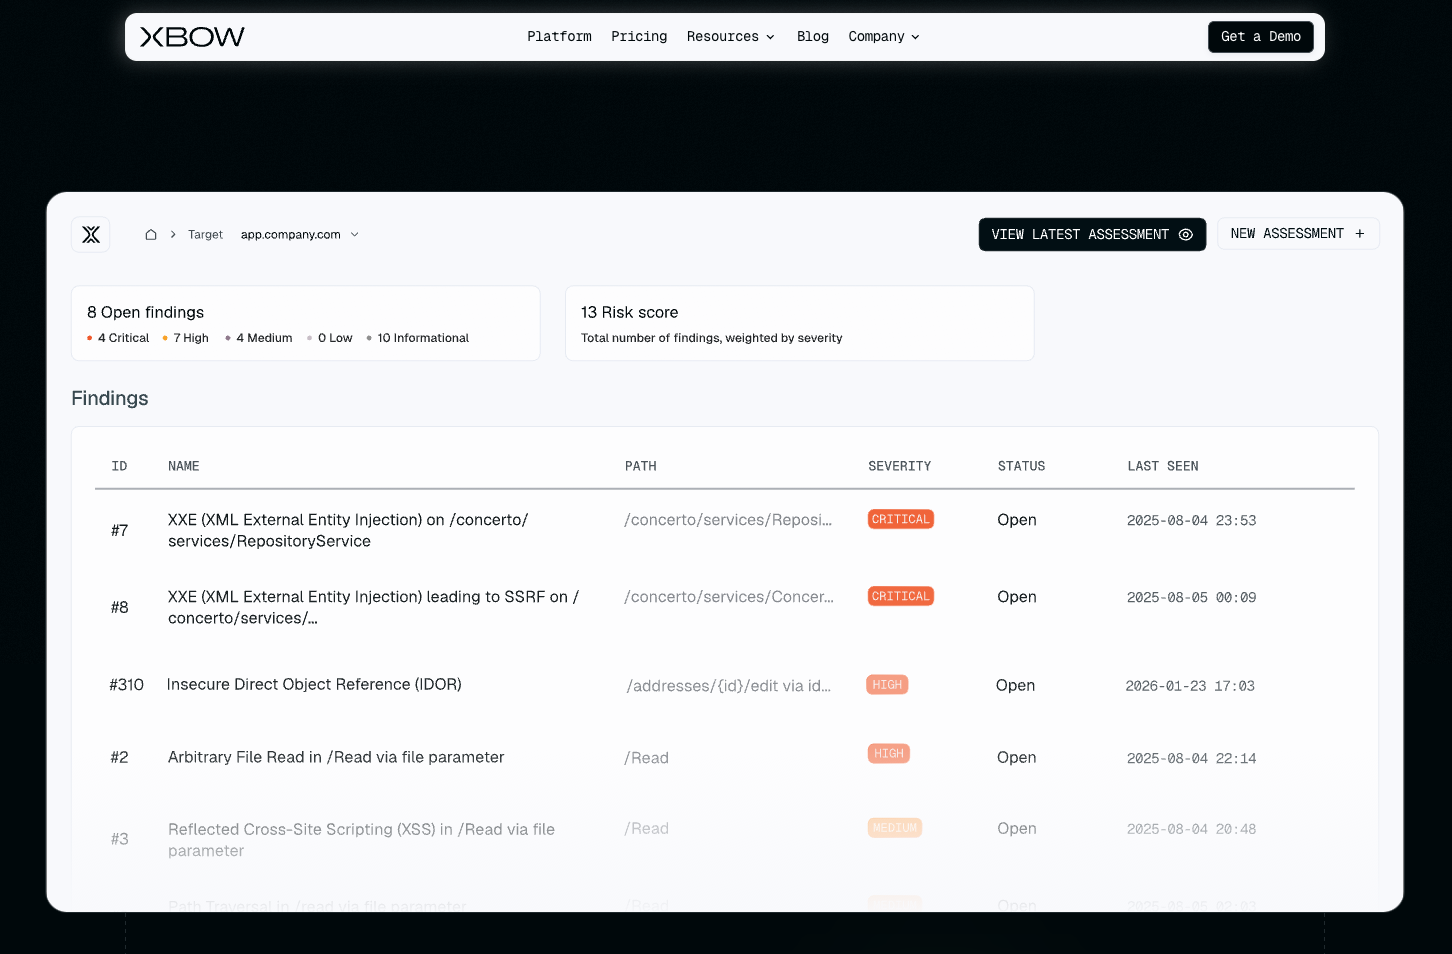
XBOW is an autonomous offensive security platform for web applications. Given a target and whatever context you can share, a coordination layer decides what to test and in what order, then the agents map the attack surface and chain vulnerabilities in parallel. It isn't tied to a single AI model, and nothing is reported until it's confirmed with a reproducible exploit.
4. Escape
Escape is an automated pentesting platform built specifically around business logic. Its multi-agent engine, Cascade, learns an application's user roles, state, and data model before testing, and remediation advice is generated against your actual source code. Every confirmed finding becomes a regression test that reruns automatically on future builds.

5. AWS Security Agent
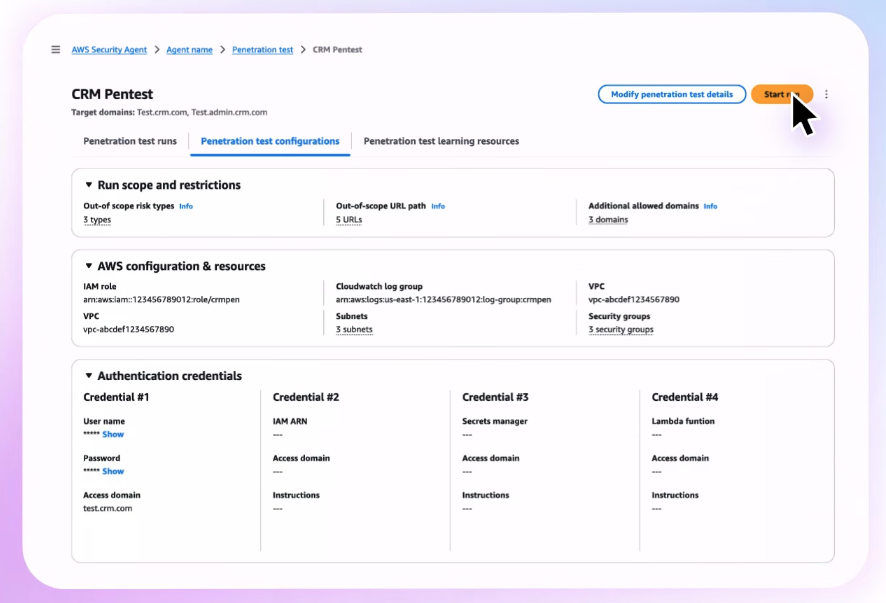
AWS Security Agent, part of AWS Continuum, runs on-demand pentests tailored to your application, learning from your source code and documentation before validating each vulnerability through exploitation. Every finding comes back with a reproducible attack path and a ready-to-implement fix, mapped against your compliance requirements.
Get started with automated web app pentesting
Security and engineering teams can now close the gap between annual pentests, with a model of testing that keeps pace with how fast they ship and how quickly today's threats move. Intruder's AI pentesting brings that depth on-demand. Ready to see it in action? Run your first pentest.
Vulnerabulletin