
The Sophos Cloud Optix alternative for automated cloud security
Sophos has retired Cloud Optix. Intruder picks up your daily cloud posture checks and adds external vulnerability scanning, attack surface discovery, and AI pentesting in one platform.
Multi-cloud security in one platform
Sophos Cloud Optix gave teams cloud posture management across AWS, Azure, and Google Cloud from one console.
The migration path Sophos recommends is cloud provider native tooling: AWS, Azure, and Google Cloud each with its own console, its own alerts, and its own way of working. What you lose is the ability to see your risk in one place and rank it in one order. Intruder keeps it to one, and you do not need a cloud security specialist to run it.

See what a misconfiguration actually exposes
Configuration issues sit next to results from 170,000+ infrastructure checks, so you can see which settings are creating real risk.
No manual checking when a CVE lands
When a new vulnerability hits the news, Intruder checks your external targets automatically and tells you which ones are affected.

Scanning in under 5 minutes
Connect a cloud account and start scanning in minutes. No procurement-length onboarding to schedule around.
Trusted by thousands of companies worldwide






Keep daily cloud posture checks running
Agentless checks run daily across your connected accounts, surfacing misconfigurations, insecure permissions, and exposed secrets with plain-English guidance on what to change. Intruder also checks those accounts every two hours for new assets, so what gets scanned keeps pace with what you actually run.


Know which findings actually matter
Intruder scans the services your cloud exposes and tests web apps and APIs behind login pages, then ranks what it finds by blending severity scores with exploit intelligence from EPSS and the KEV list, plus input from our own security team. When Intruder says something is critical, you know it is.
Scan the container images you actually have deployed
Cloud Optix container image scanning was retired ahead of the rest of the product. Intruder discovers images automatically across AWS ECR, Azure Container Registry, Google Cloud Artifact Registry, and Docker Hub, with no agents to deploy or maintain. You choose which tags to monitor, so you only see vulnerabilities in the images you actually use rather than every version ever pushed.

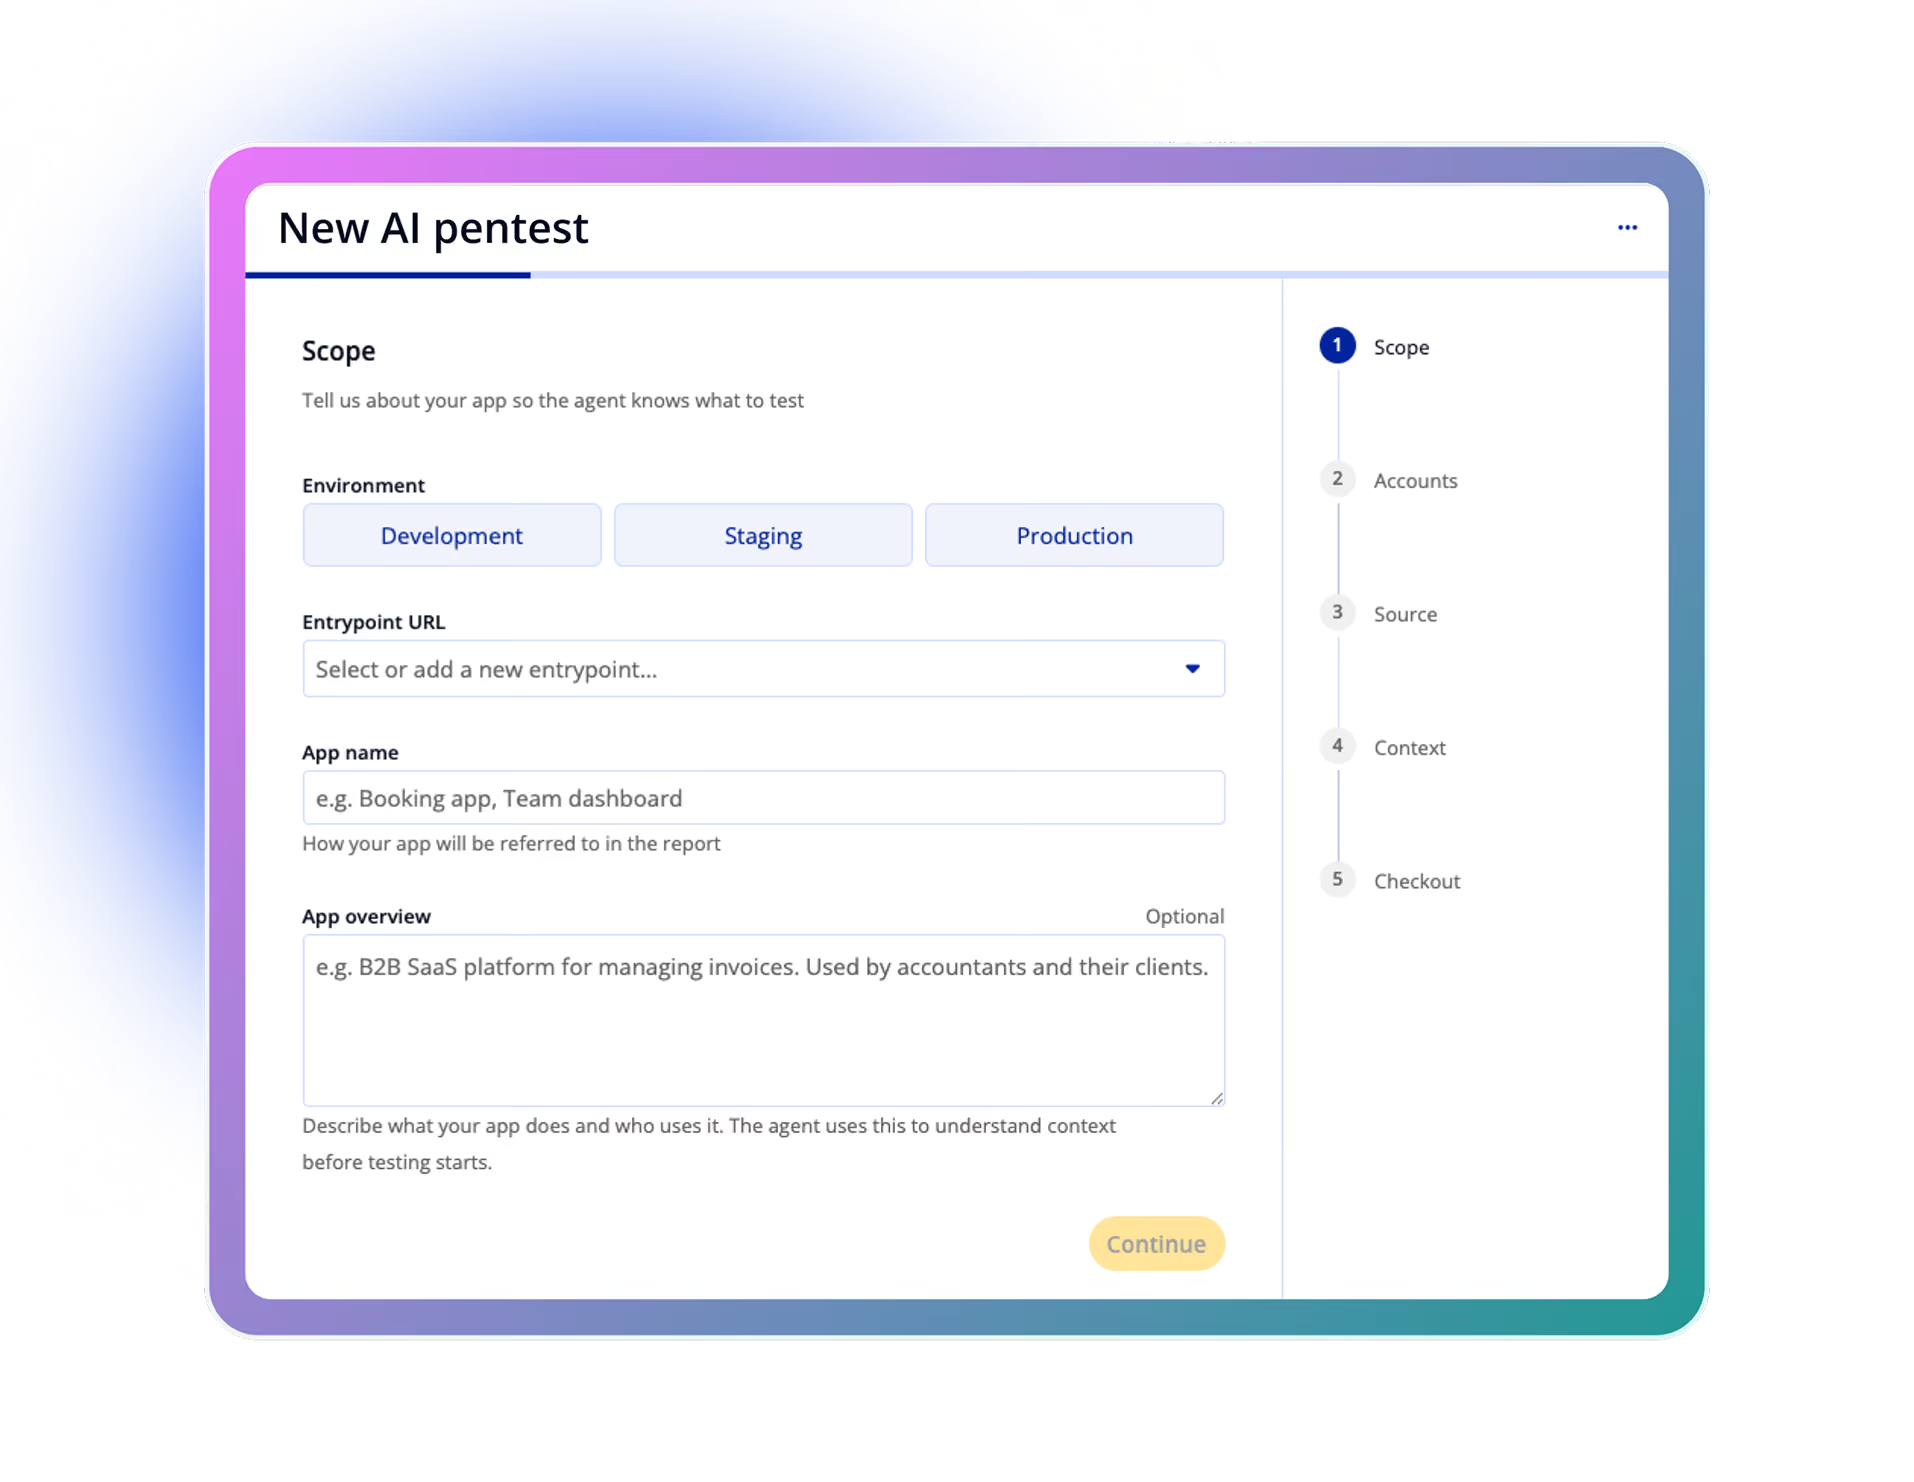
Pentest on every release, not once a year
Annual pentests leave months uncovered while your code keeps shipping. Connect your codebase through GitHub or GitLab, provide context and credentials, and launch a test in minutes with no scoping calls or lead time. Agents built and trained by our CREST-certified pentesters test with full code awareness, finding issues that have evaded manual pentesters for years.
Generate audit-ready reports, instantly
Streamline your audit process and eliminate manual evidence gathering. Intruder generates audit-ready reports for SOC 2, ISO 27001, HIPAA, and DORA, syncs live issue data into Vanta and integrates with Drata, and pentest reports are accepted as evidence in their own right. The evidence is ready as soon as your auditor asks for it.
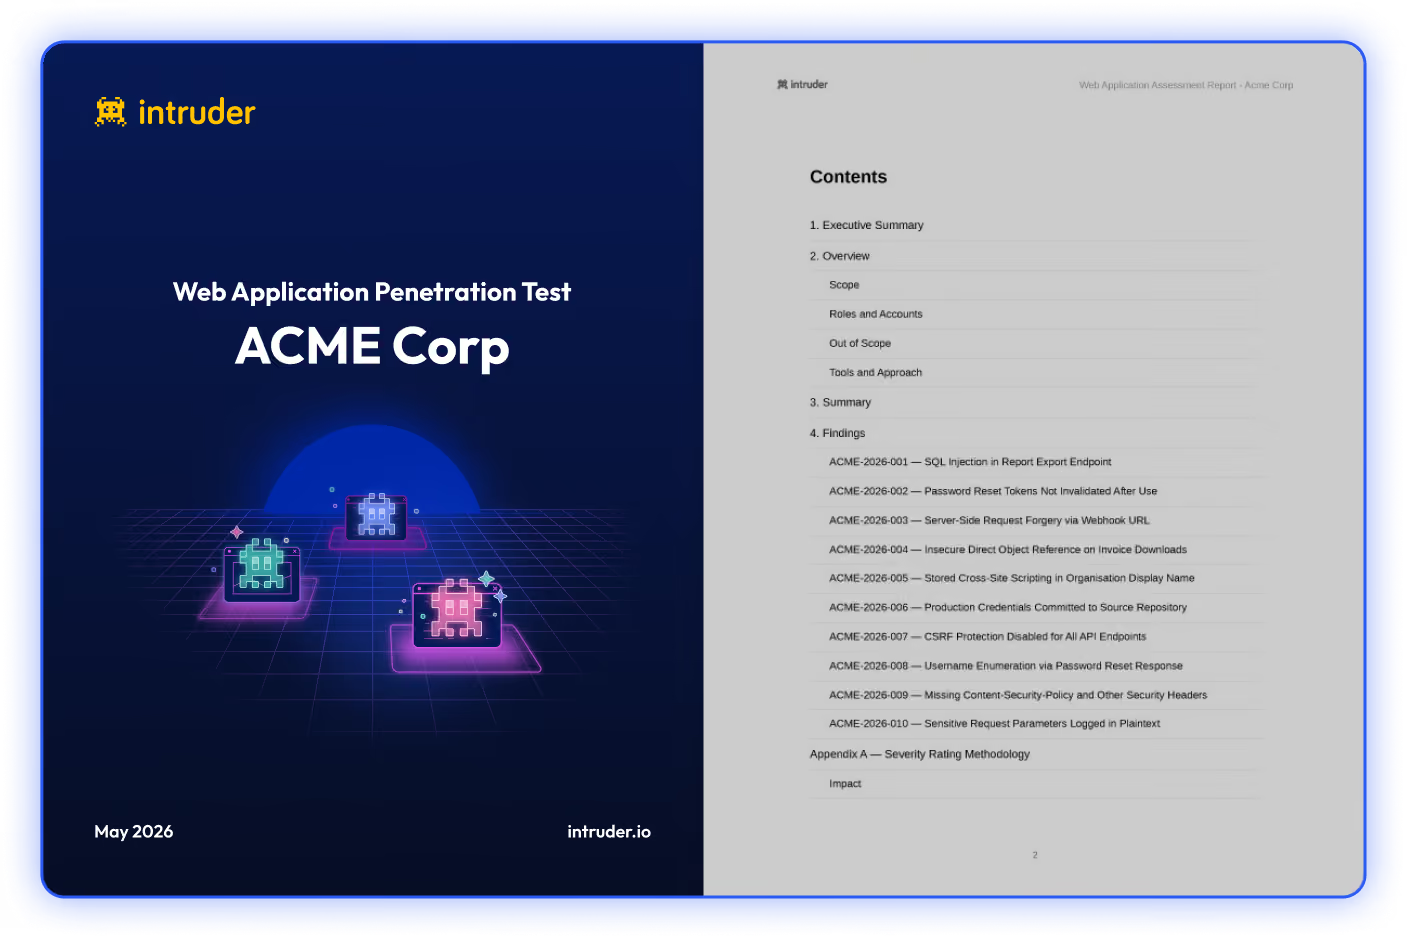

From finding to fixing, fast
Intruder connects to your existing tools like Slack, Jira, and GitHub, to keep remediation moving. GregAI triages findings and drafts plain-language notes so your team can fix issues fast without needing to be security experts.


Sophos has retired the product. End of sale was 31 March 2026, with end of life on 30 September 2026. After that date, access ends and Sophos deletes dashboards, alerts, policies, and historical data. Container image scanning was removed earlier, in March 2026.
It depends what you used it for. Sophos recommends cloud provider native tooling for posture management and Taegis for cloud detection and response. If you want posture checks and active vulnerability testing in one place rather than split across native consoles, Intruder covers AWS, Azure, and Google Cloud posture alongside external, web application, and API scanning.
AWS, Azure, and Google Cloud for cloud security scans, plus Cloudflare for DNS target sync. Connected accounts are checked every two hours for new assets.
