

Key Points
Another busy month for the engineering team. Here's what's new and live in Intruder.
TL;DR
- AI pentest results in the portal: Manage pentest findings in the same place as everything else
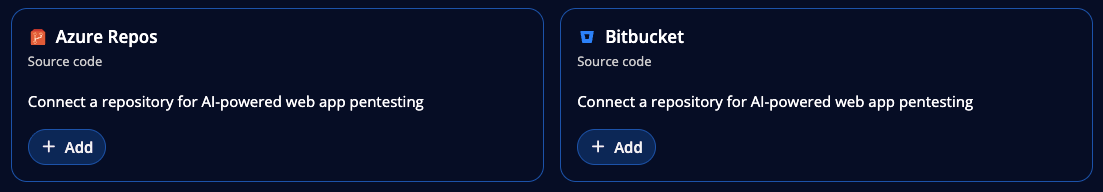
- Bitbucket and Azure repos for AI Pentesting: Connect Bitbucket or Azure repos and run AI pentests against your code
- Retest pentest findings: Unlimited retests to check whether your fixes worked, without re-running the full pentest
- Cross-domain scanning: One authenticated scan across your app, its APIs, and its auth provider
- Improved Azure DevOps integration: Control which targets and tags create work items
- Auto AI SQL injection validation: SQL injection findings are now automatically validated during the scan, so false positives are suppressed before they reach you
- Monitor cyber hygiene: See how your score is trending over time
Your pentest findings have joined the rest of your workflows
Your AI pentest findings now live in the portal alongside your regular scan issues. Same layout, remediation guidance, and ability to comment. Managing pentest results becomes part of your normal security workflow, right alongside everything else.
Connect Bitbucket and Azure repos for AI pentesting
Bitbucket and Azure Repos now sit alongside GitHub and GitLab as supported code repositories for AI Pentesting. If your team hosts code in either, you can connect your repos and run AI-powered penetration tests directly against your codebase.
Spot-check your pentest fixes
Found and fixed an AI pentest issue? Select the finding(s) in the portal, hit retest, and get a check on whether they've actually been resolved. Retests only check the findings you select, and results are captured in a dedicated retest report alongside the originals, giving you a clear record of what's been fixed. The best bit? Retests are unlimited and free.
Authenticated scanning that follows your app across domains
We’ve introduced the ability to scan across subdomains, so your frontend and its API backend could be covered in one authenticated scan. Cross-domain scanning takes that further. If your app relies on entirely separate domains for authentication, APIs, or external services, you can now add up to three cross-domains alongside your primary application target. The scanner follows the real application flows across domain boundaries, so a single scan covers more of how your app actually works.
Available on: Cloud, Pro, and Enterprise
Route Azure DevOps work items to the right teams
You can now scope which vulnerabilities auto-create Azure DevOps work items by target and tag, combining asset scope with existing severity rules. That way only the issues that matter reach each project, and the right teams get the right tickets.
Available on: Cloud, Pro, and Enterprise
Less noise from SQL injection checks
Intruder now deploys AI agents to validate SQL injection findings before they reach you. Confirmed false positives are automatically suppressed, while genuine and inconclusive results continue to surface as normal. Less time triaging noise, more time on the issues that actually matter.
Available on: Enterprise
Understand how your security posture is changing over time
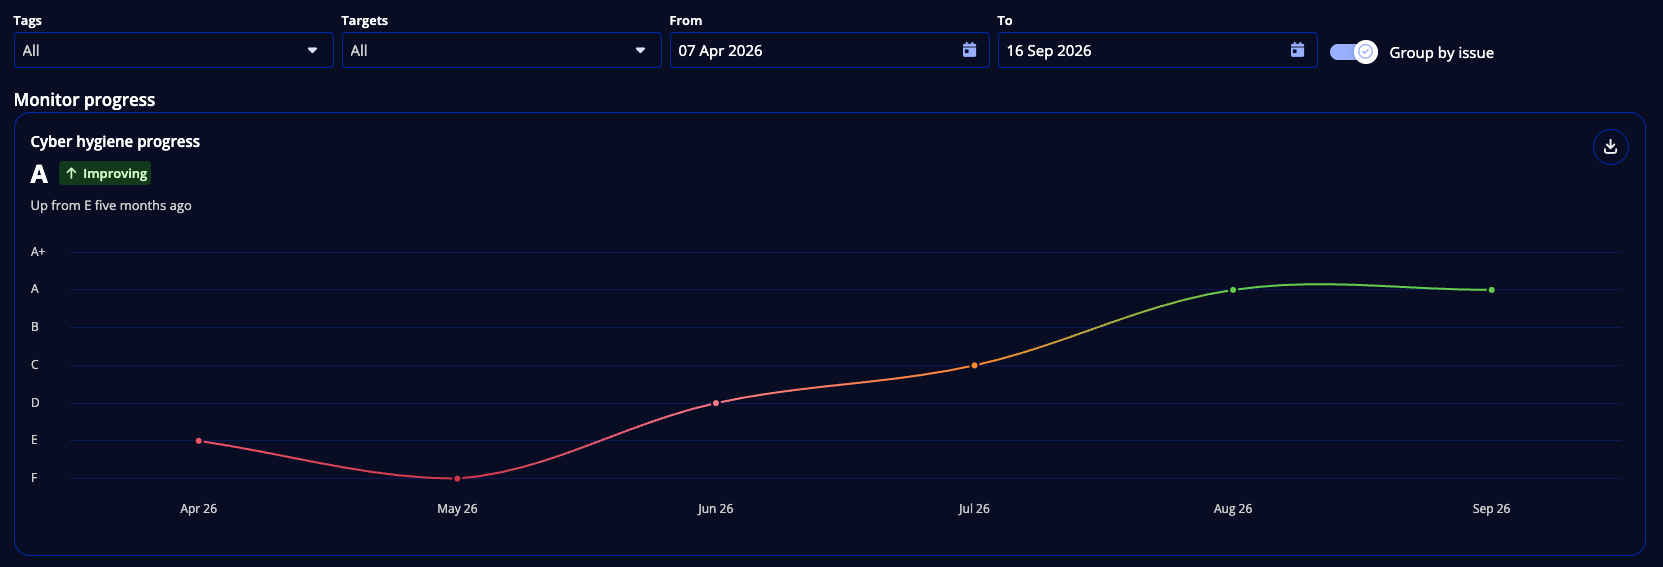
You can now see how your Cyber Hygiene Score is trending over time, with a configurable range from four weeks up to a full year. That means you can answer "are we getting better or worse, and how quickly?" at a glance. Useful when you need to demonstrate progress to leadership or show an auditor that things are moving in the right direction.
Don't take our word for it, try it for yourself
All of it's live now. Log in to take a look, or if you're new here, start a free trial and see what's exposed across your attack surface. Interested in AI pentesting? Take a look at pricing, or book a call.
Got feedback or something you'd like to see next? Send it our way.

Vulnerabulletin