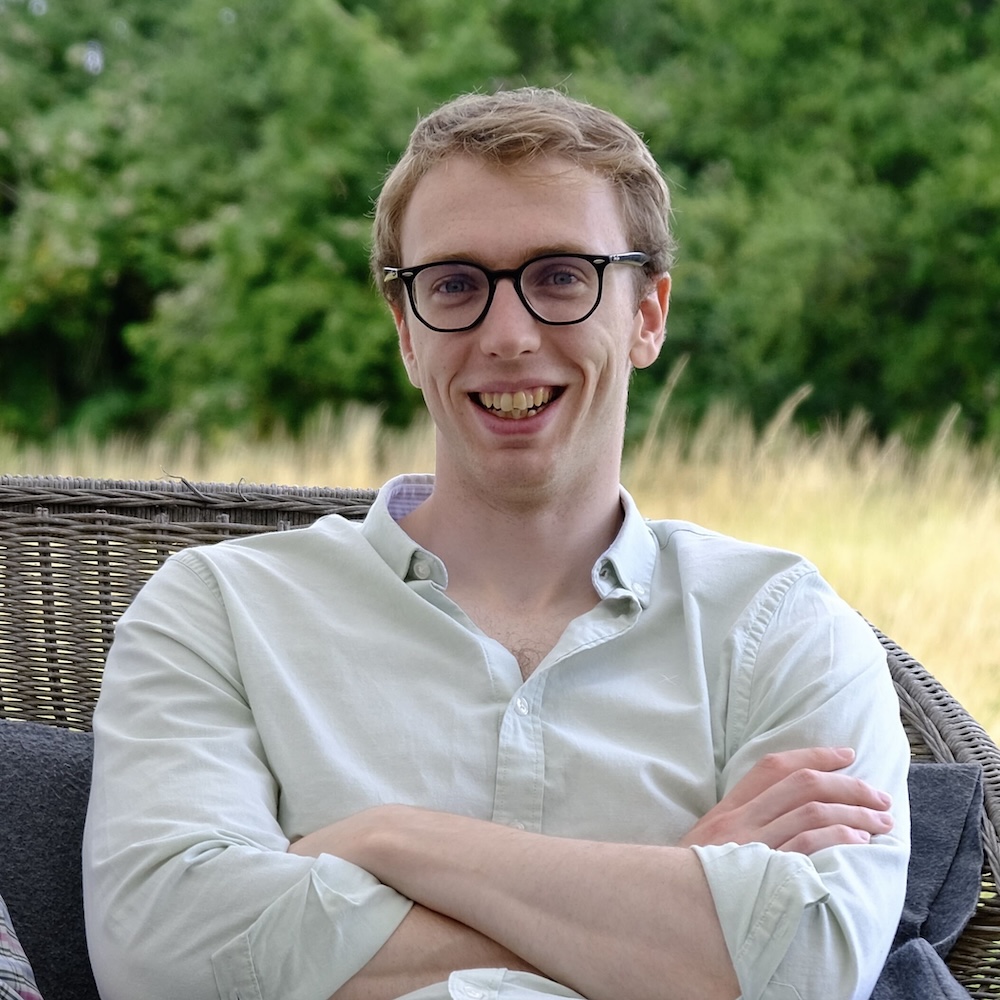
Daniel Thatcher

Security Research Engineer
Daniel is a security researcher with a background in penetration testing, and a focus on exploiting web applications in black-box scenarios.

Daniel Thatcher

's Posts

Clear all filters
Is AI pentesting as good as a human pentester?

Is AI pentesting as good as a human pentester?

An honest comparison of AI pentesting and human pentesting by a seasoned pentester, including methodology, coverage, findings, and reports.
AI pentesting
Attack surface management: Find your assets before the hackers do

Attack surface management: Find your assets before the hackers do

Find out how Daniel Thatcher demonstrated the importance of attack surface management to delegates at DTX Europe.
Attack surface management
What Are Fake Clickjacking Bug Bounty Reports?

What Are Fake Clickjacking Bug Bounty Reports?

Beware, there’s a new trend in play, concerning a new type of fake clickjacking bug bounty reports. Read on to understand what to ...
Insights
No results found
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.

Daniel Thatcher

's Researches

Tricks for Reliable Split-Second DNS Rebinding in Chrome and Safari

This is the second post in a two-part series on DNS rebinding. In this post, I introduce new techniques for achieving reliable, split-second DNS rebinding in Chrome, Edge, and Safari when IPv6 is available, as well as a technique for bypassing the local network restrictions applied to the fetch API in Chromium-based browsers.

We Hacked Ourselves With DNS Rebinding

This post is the first in a two-part series on DNS rebinding in web browsers. In this post, I will talk about a bug we found in our own product which allowed us to retrieve low-privileged AWS credentials using DNS rebinding. In the next post, I will share new techniques to reliably achieve split-second DNS rebinding in Chrome, Edge, and Safari, as well as bypass Chrome's restrictions on requests to private networks.‍

Detecting Server-Side Prototype Pollution

Prototype pollution bugs have been a feature in many CTFs in recent years, and real-world examples in open-source applications have led to impactful exploits such as remote code execution and denial-of-service. The discovery of these bugs has long relied on access to source code, with no safe black-box detection techniques being widely used.

In GUID We Trust

GUIDs (often called UUIDs) are widely used in modern web applications. However, seemingly very few penetration testers and bug bounty hunters are aware of the different versions of GUIDs and the security issues associated with using the wrong one.

Practical HTTP Header Smuggling: Sneaking Past Reverse Proxies to Attack AWS and Beyond

Modern web applications typically rely on chains of multiple servers, which forward HTTP requests to one another. The attack surface created by this forwarding is increasingly receiving more attention, including the recent popularisation of cache poisoning...