
Intruder for

Manage exposure across your entire digital estate
One platform to secure your external network, web apps, APIs, cloud environments, and internal endpoints. Discovery, triage, and remediation made easy.
Join 3,000+ companies securing their attack surface with Intruder






A single view of exposure
One platform. One list of issues. Coverage for your entire environment. No cross-referencing dashboards to work out where you stand. Know what's urgent at a glance.
Continuous security
Gain peace of mind knowing Intruder is plugged in and monitoring your entire digital estate. When things change, scans launch automatically and you’re notified where things need attention.
More time for stretched teams
A unified platform, continuous scanning, AI pentesting agents, and a virtual security analyst leave more time for security and IT teams to fix the real risks.
All in one security
Continuous vulnerability scanning and pentesting

Over 170,000 checks run across your infrastructure, web apps, and APIs, on a schedule, when your attack surface changes, and when new threats emerge. On-demand AI pentesting delivers the investigative depth of a manual pentest when needed.
Multi-cloud security
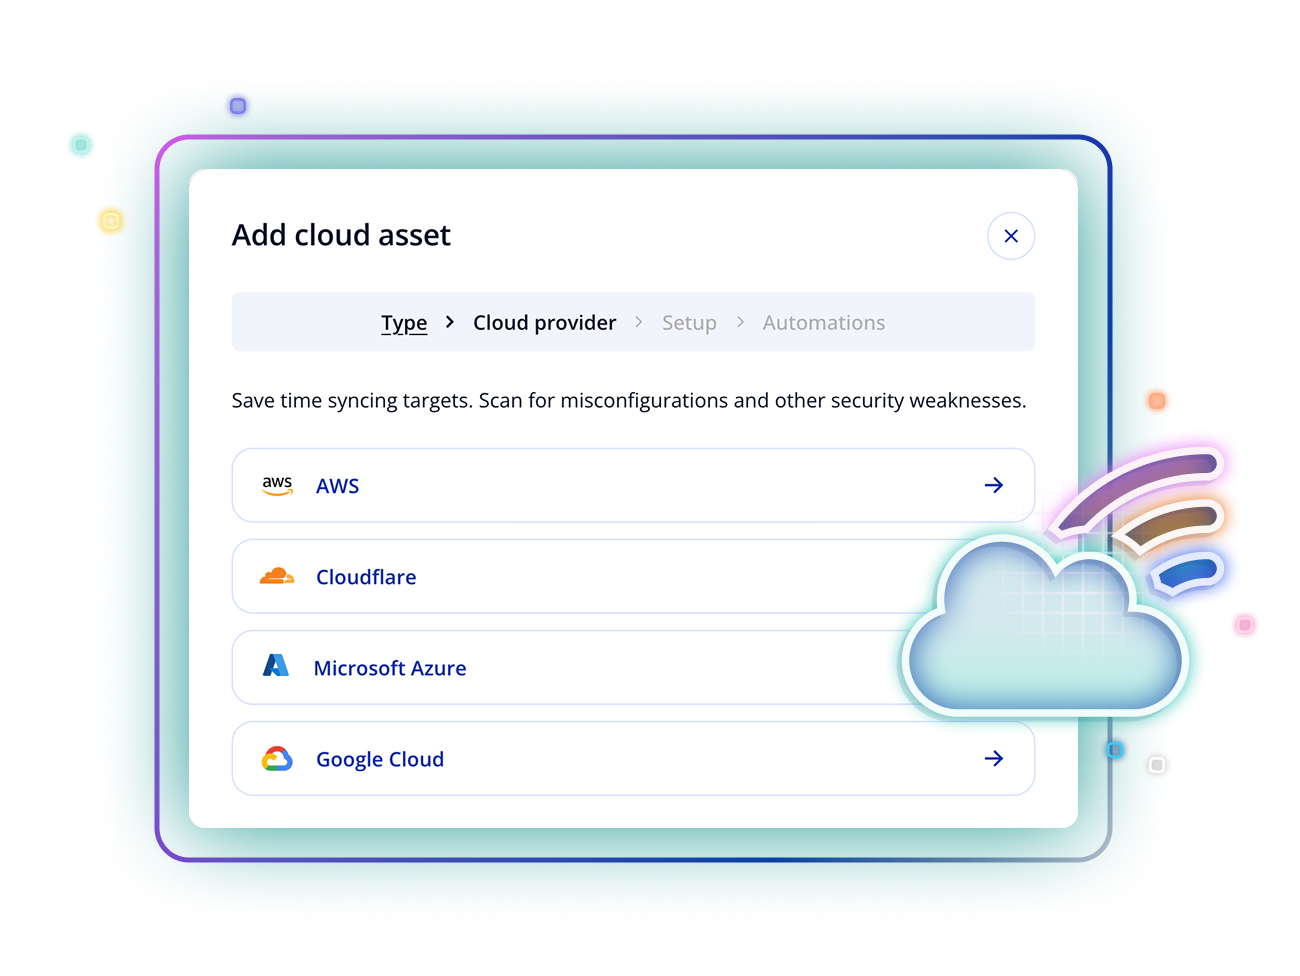
Connect your AWS, Azure, and Google Cloud accounts to run daily configuration checks that flag misconfigurations, exposed secrets, and insecure permissions. Registry level container image scanning catches vulnerable containers before they reach production.
Always-on attack surface monitoring
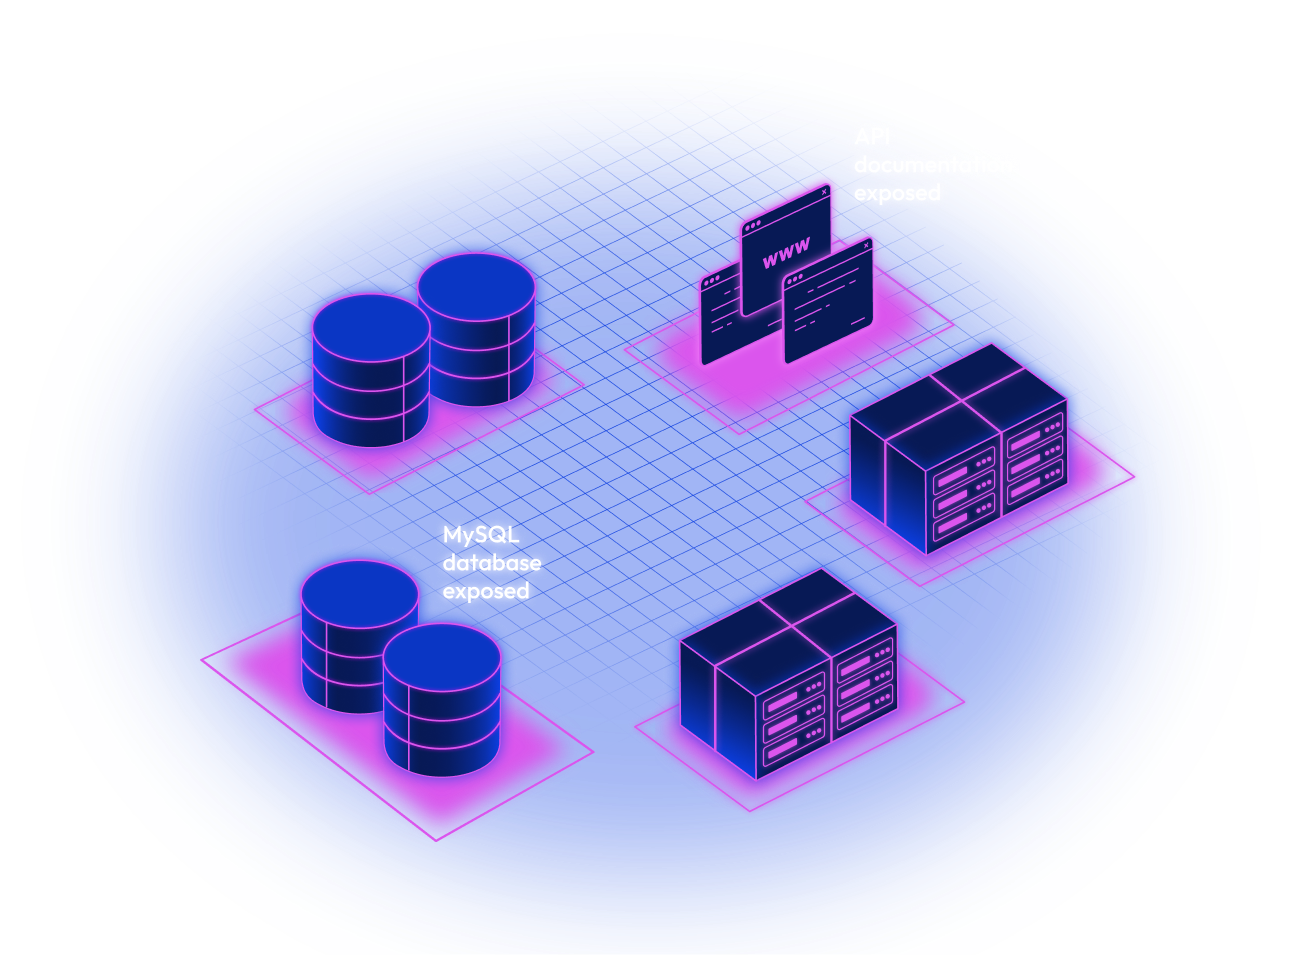
Continuous monitoring ensures security keeps up with engineering. Spot exposed assets the moment they appear, from new subdomains to exposed ports and services you'd lost track of.
Find what's exposed, fix what matters, and stay ahead of new threats
External Scanning
Infrastructure Security
Attack Surface Monitoring
Respond to changes

CSPM
Daily cloud config checks

Asset Discovery
Reveal unknown targets

DAST
Secure web apps

Risk Based Prioritization
No more alert fatigue

Cyber Hygiene Reporting
Demonstrate progress

Emerging Threat Detection
Check and act fast

Container Image Scanning
Automated image discovery

Secrets Detection
Prevent leaked credentials

Website Security
140k+ checks

API Security
Test your APIs

Compliance
SOC 2, ISO, HIPAA, DORA

Internal Scanning
Secure employee devices
Our customers love Intruder





One platform. Continuous security.
Intruder integrates with Jira, GitHub, GitLab, Azure DevOps, and ServiceNow for issue tracking, Slack and Microsoft Teams for alerts, Drata and Vanta for compliance, and Microsoft Sentinel for SIEM. See all our integrations.
Intruder runs over 170,000 checks across your external infrastructure, web apps, APIs, cloud environments, container images, and internal endpoints. Everything lands in a single issues view, prioritized by real-world risk.
Enterprise tools like Tenable and Qualys give you breadth but expect a dedicated team to work through the results. Intruder is built for midsize teams that don't have that resource. It combines vulnerability scanning, attack surface management, cloud security, and AI pentesting in one platform, with prioritization and noise reduction built in.
Add your targets or connect your cloud accounts and your first scan launches immediately. No agents to deploy for external or cloud scanning, and no professional services required. Most teams are up and running the same day.