
Measure cyber hygiene
Monitor your security posture, understand how it’s changing over time, and get insights for how to improve.
Join 3,000+ companies securing their attack surface with Intruder


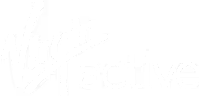




One view of your security posture
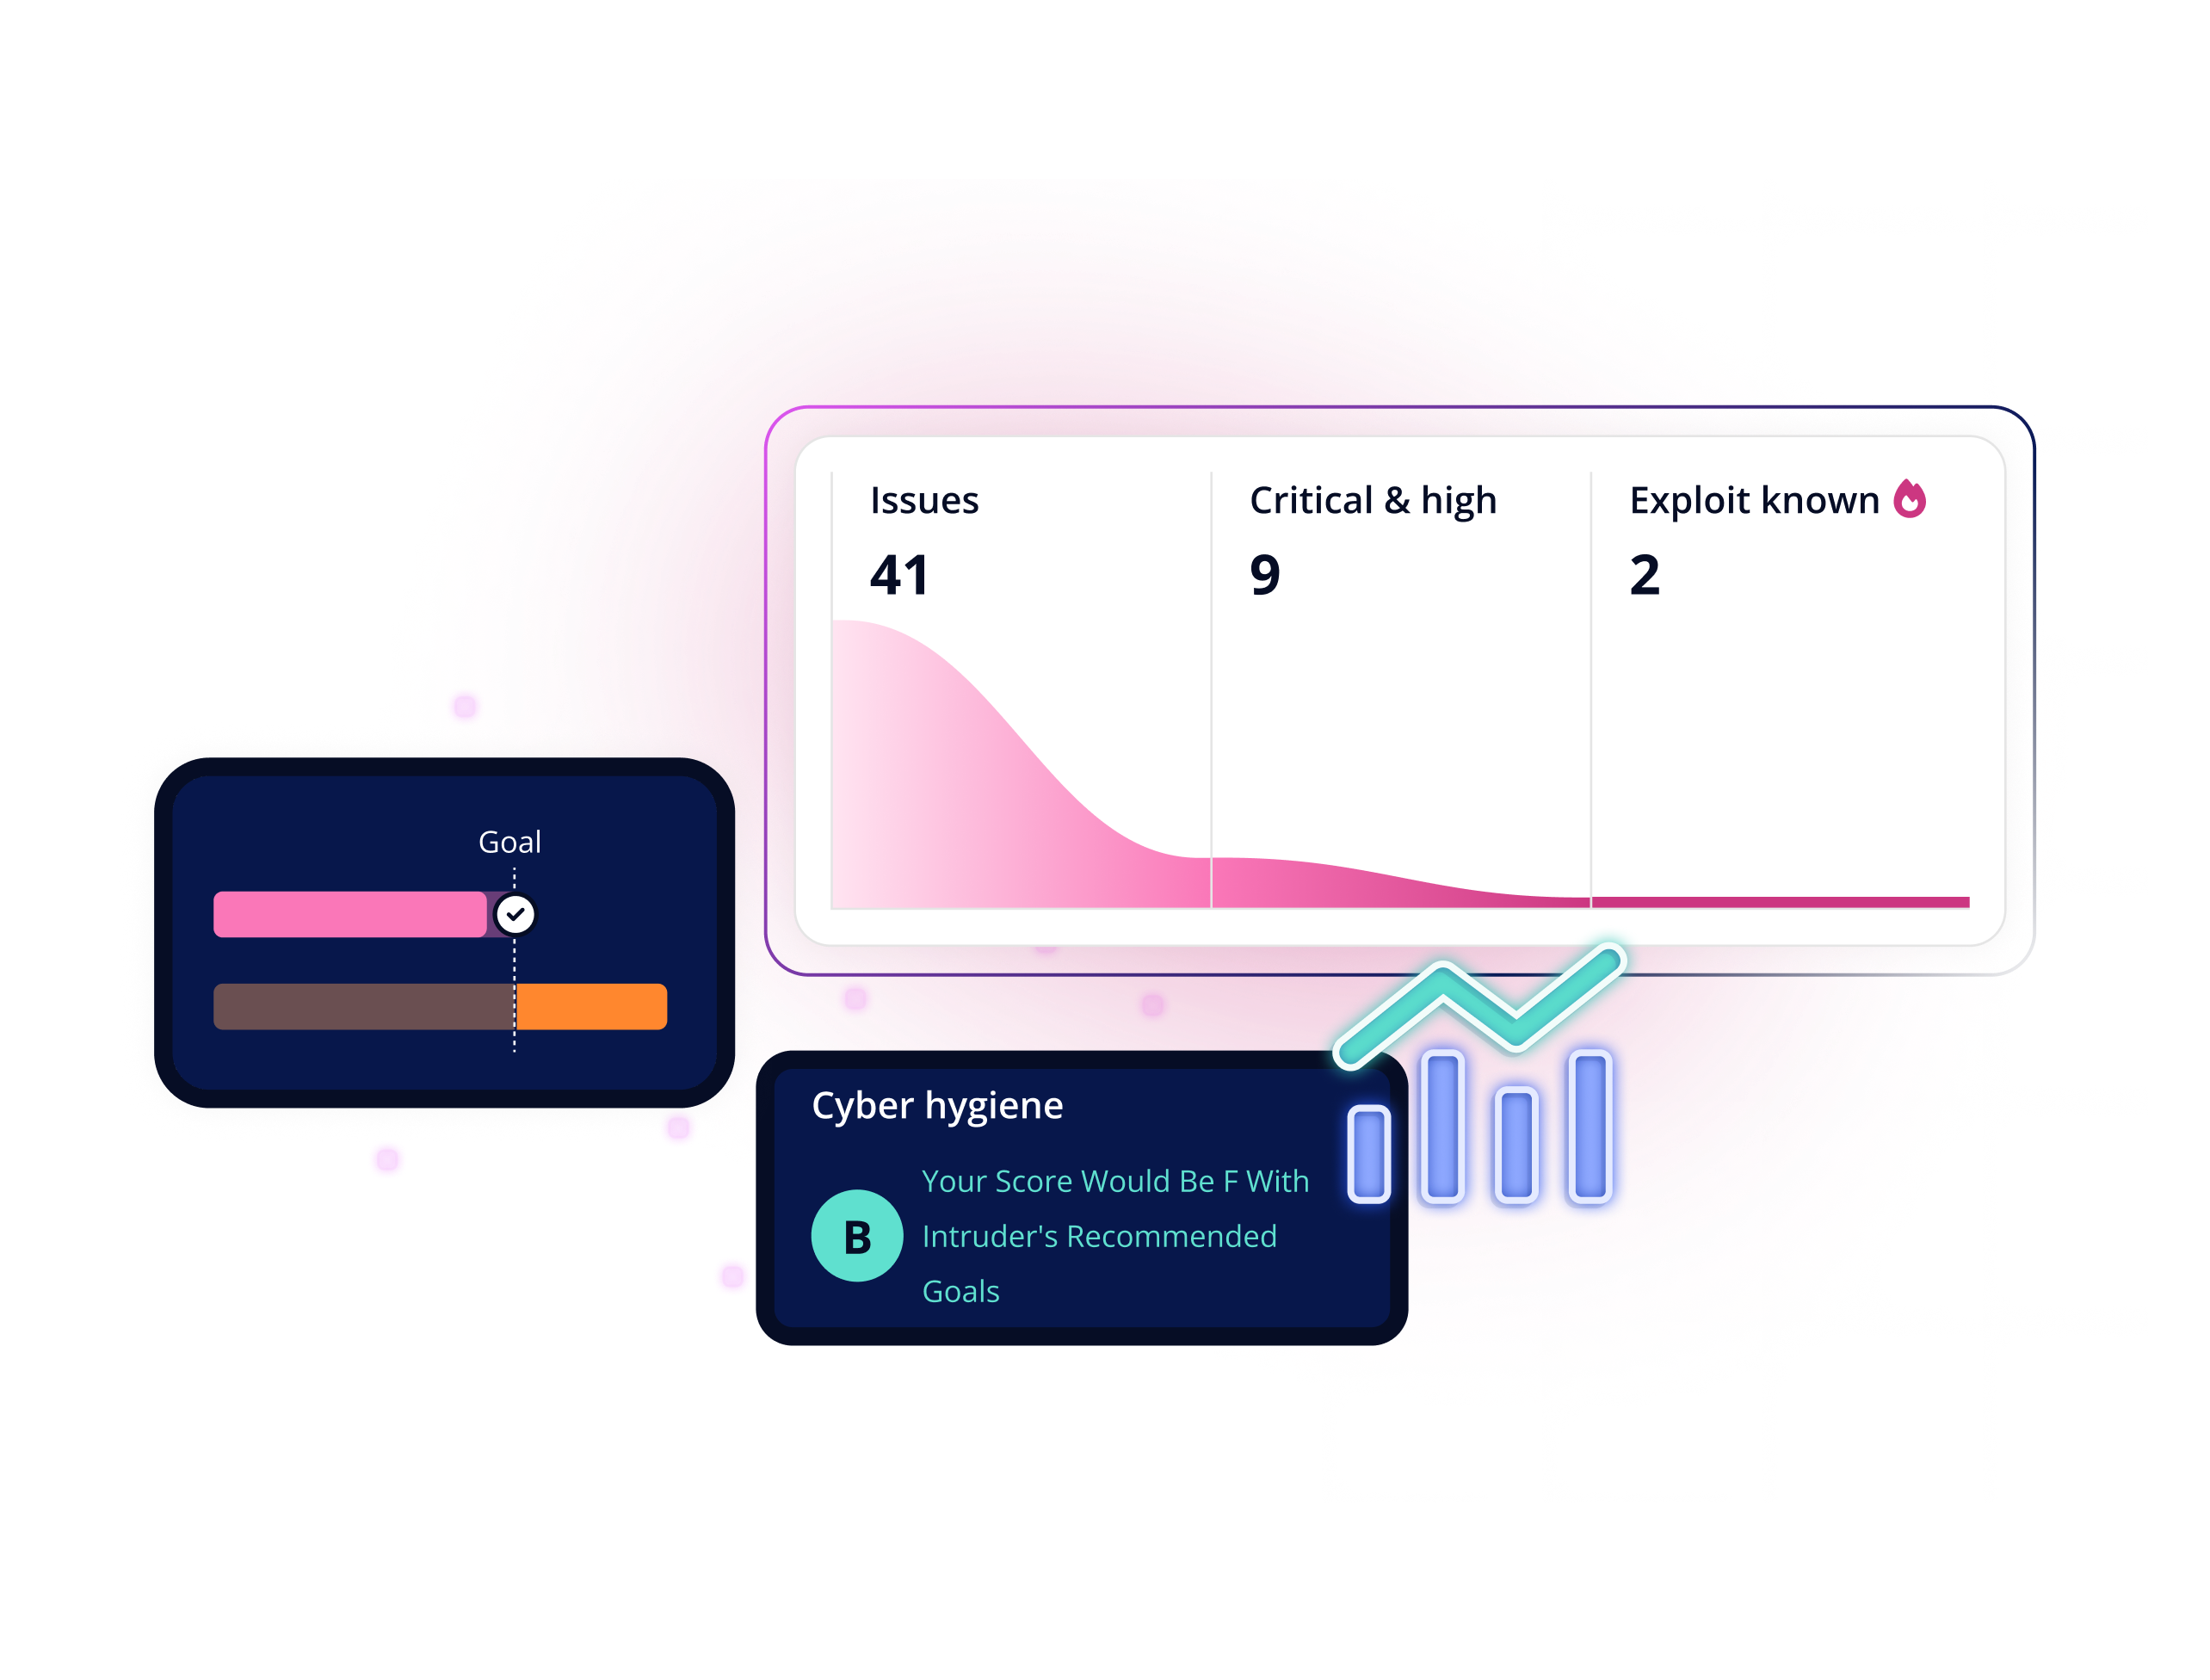
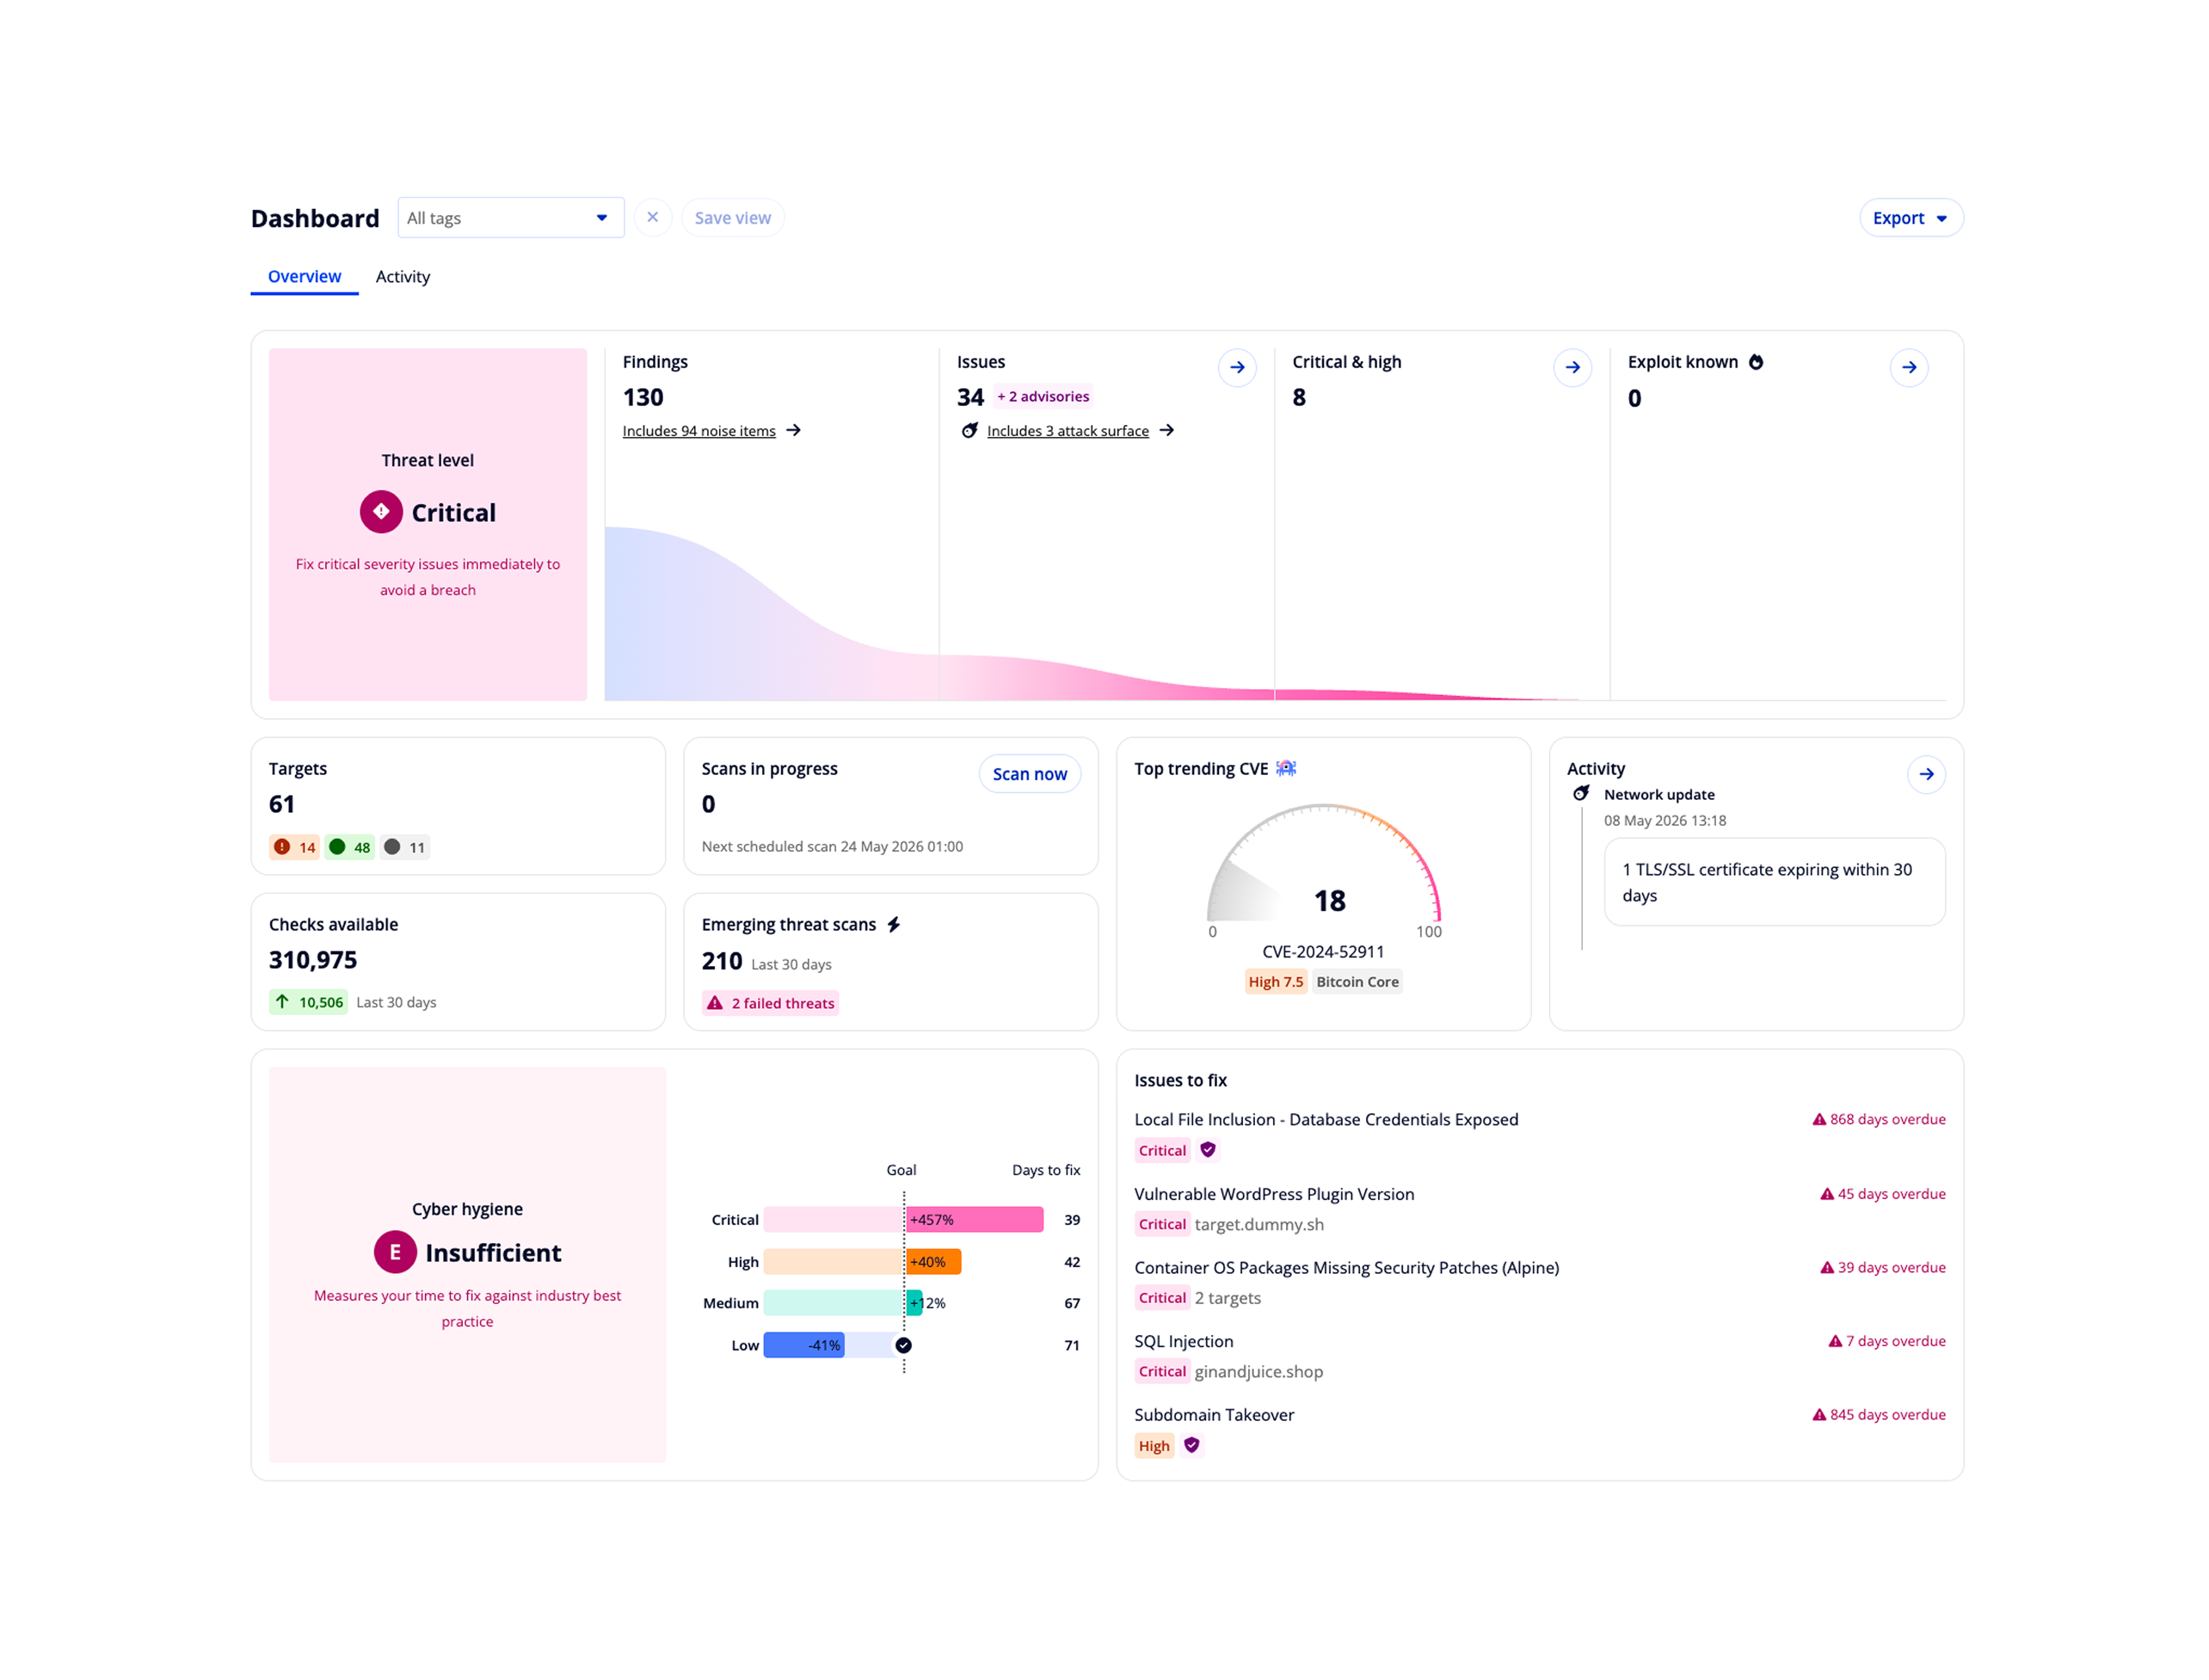
Stop piecing together insights from different tools and spreadsheets. Intruder plugs into your entire digital estate to provide a single view of cyber hygiene.
Show progress to stakeholders
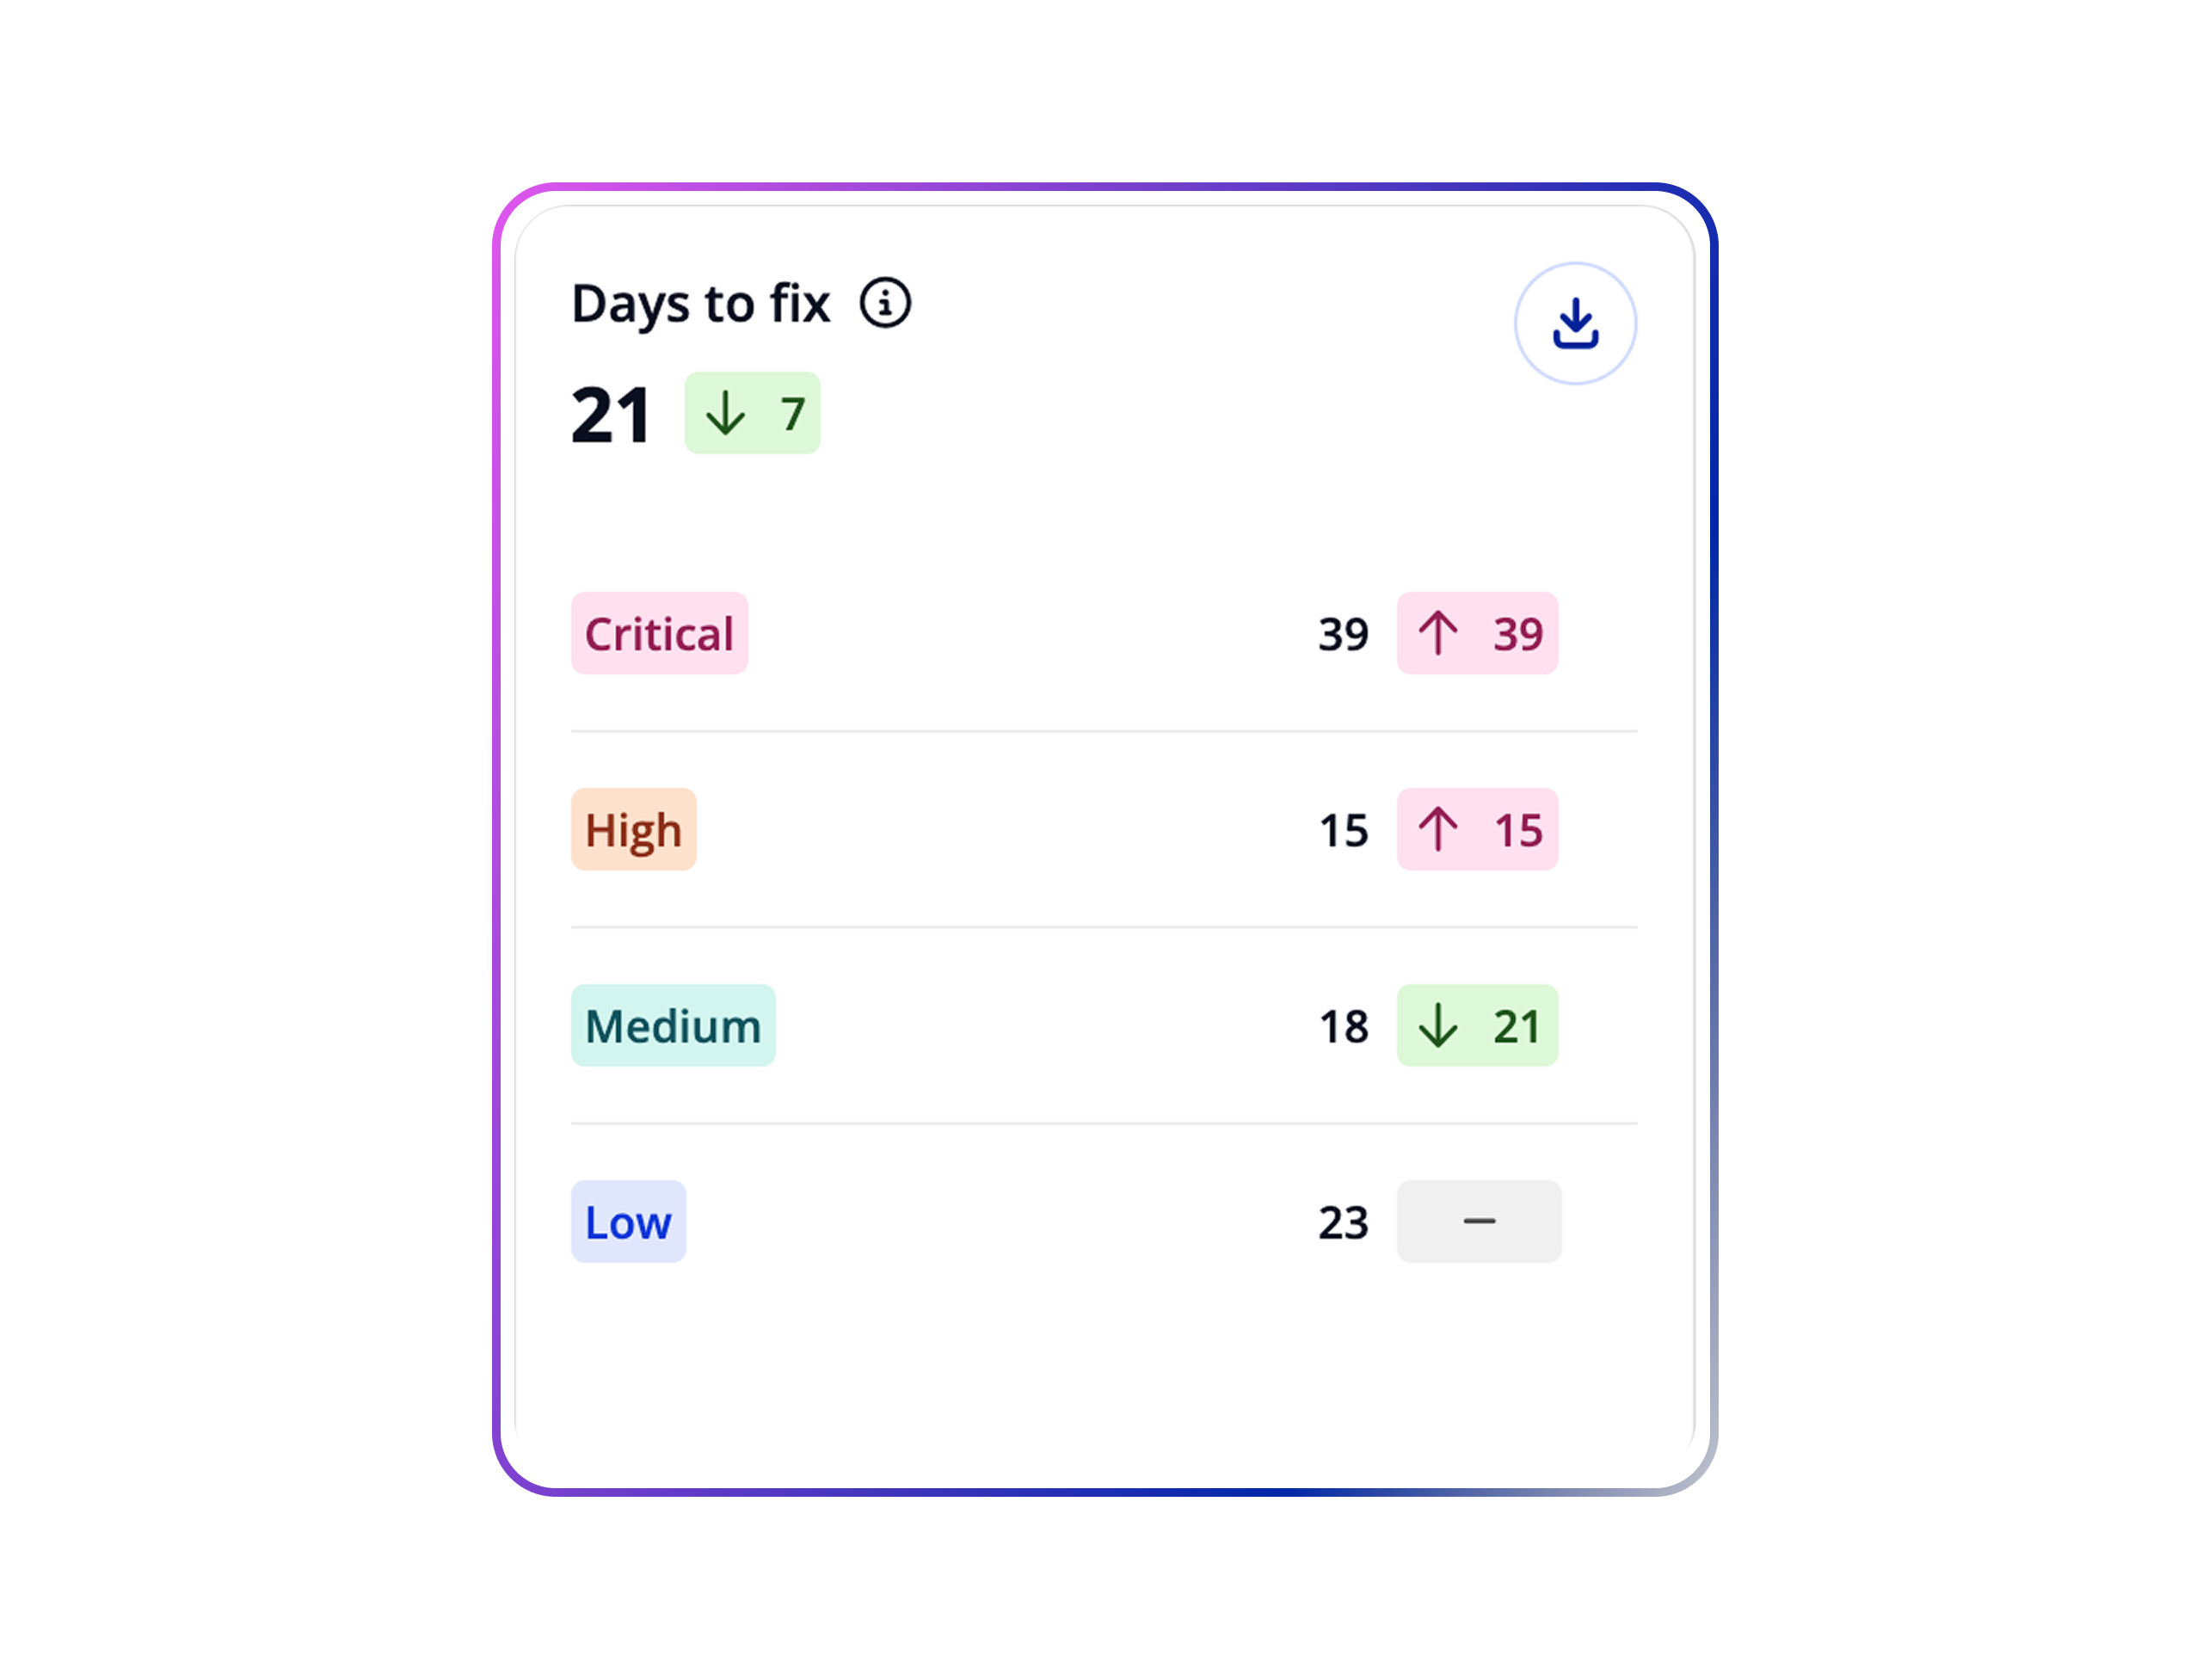
Prove the work your doing is moving the needle. Easily show stakeholders how your number of open issues, time to fix, and cyber hygiene score are changing over time.
Identify problems early
Spot negative trends and pain points early so you can take corrective action, or build the business case for additional resources.
Quantify your security posture
Real-time threat level

Get an easy to understand, live view of your threat level based on the number of unresolved vulnerabilities and attack surface issues. Scoring is weighted so critical issues with known exploits carry more impact.
Cyber hygiene score
Define your cyber hygiene goals by specifying target remediation times by issue severity. Automatically track performance against these goals on the dashboard.
Compliance-ready scan reports
Detailed reports show all your scanner findings and can easily be shared with auditors, or automatically sent to GRC platforms including Vanta and Drata.
Find what's exposed, fix what matters, and stay ahead of new threats
External Scanning
Infrastructure Security
Attack Surface Monitoring
Respond to changes

CSPM
Daily cloud config checks

Asset Discovery
Reveal unknown targets

DAST
Secure web apps

Risk Based Prioritization
No more alert fatigue

Cyber Hygiene Reporting
Demonstrate progress

Emerging Threat Detection
Check and act fast

Container Image Scanning
Automated image discovery

Secrets Detection
Prevent leaked credentials

Website Security
140k+ checks

API Security
Test your APIs

Compliance
SOC 2, ISO, HIPAA, DORA

Internal Scanning
Secure employee devices
Our customers love Intruder





One platform. Continuous security.
Intruder's cyber hygiene score is a letter grade (A through F) that reflects how well your team is managing and remediating vulnerabilities over time. The score is based on each issue's CVSS severity and its real-world exploitation likelihood, using EPSS and KEV (Known Exploited Vulnerabilities) data. Learn more about the cyber hygiene score.
A scan report is a snapshot — it shows what's exposed right now. Intruder's analytics layer tracks how your posture changes across time periods: issues opened and closed, average time to fix by severity, exposure trends, and your cyber hygiene score compared to the previous period.
Yes. Intruder's reports include a high-level summary (targets scanned, issues by severity, an exposure-over-time graph) and a full inventory of issues with remediation guidance, formatted to share with auditors, customers, or compliance teams. Reports can also be pushed directly to Drata and Vanta as scan evidence.
Intruder integrates with Jira, GitHub, GitLab, Azure DevOps, and ServiceNow for issue tracking, Slack and Microsoft Teams for alerts, Drata and Vanta for compliance, and Microsoft Sentinel for SIEM. See all our integrations.