
Critical vulnerabilities don't wait. Neither does Intruder.
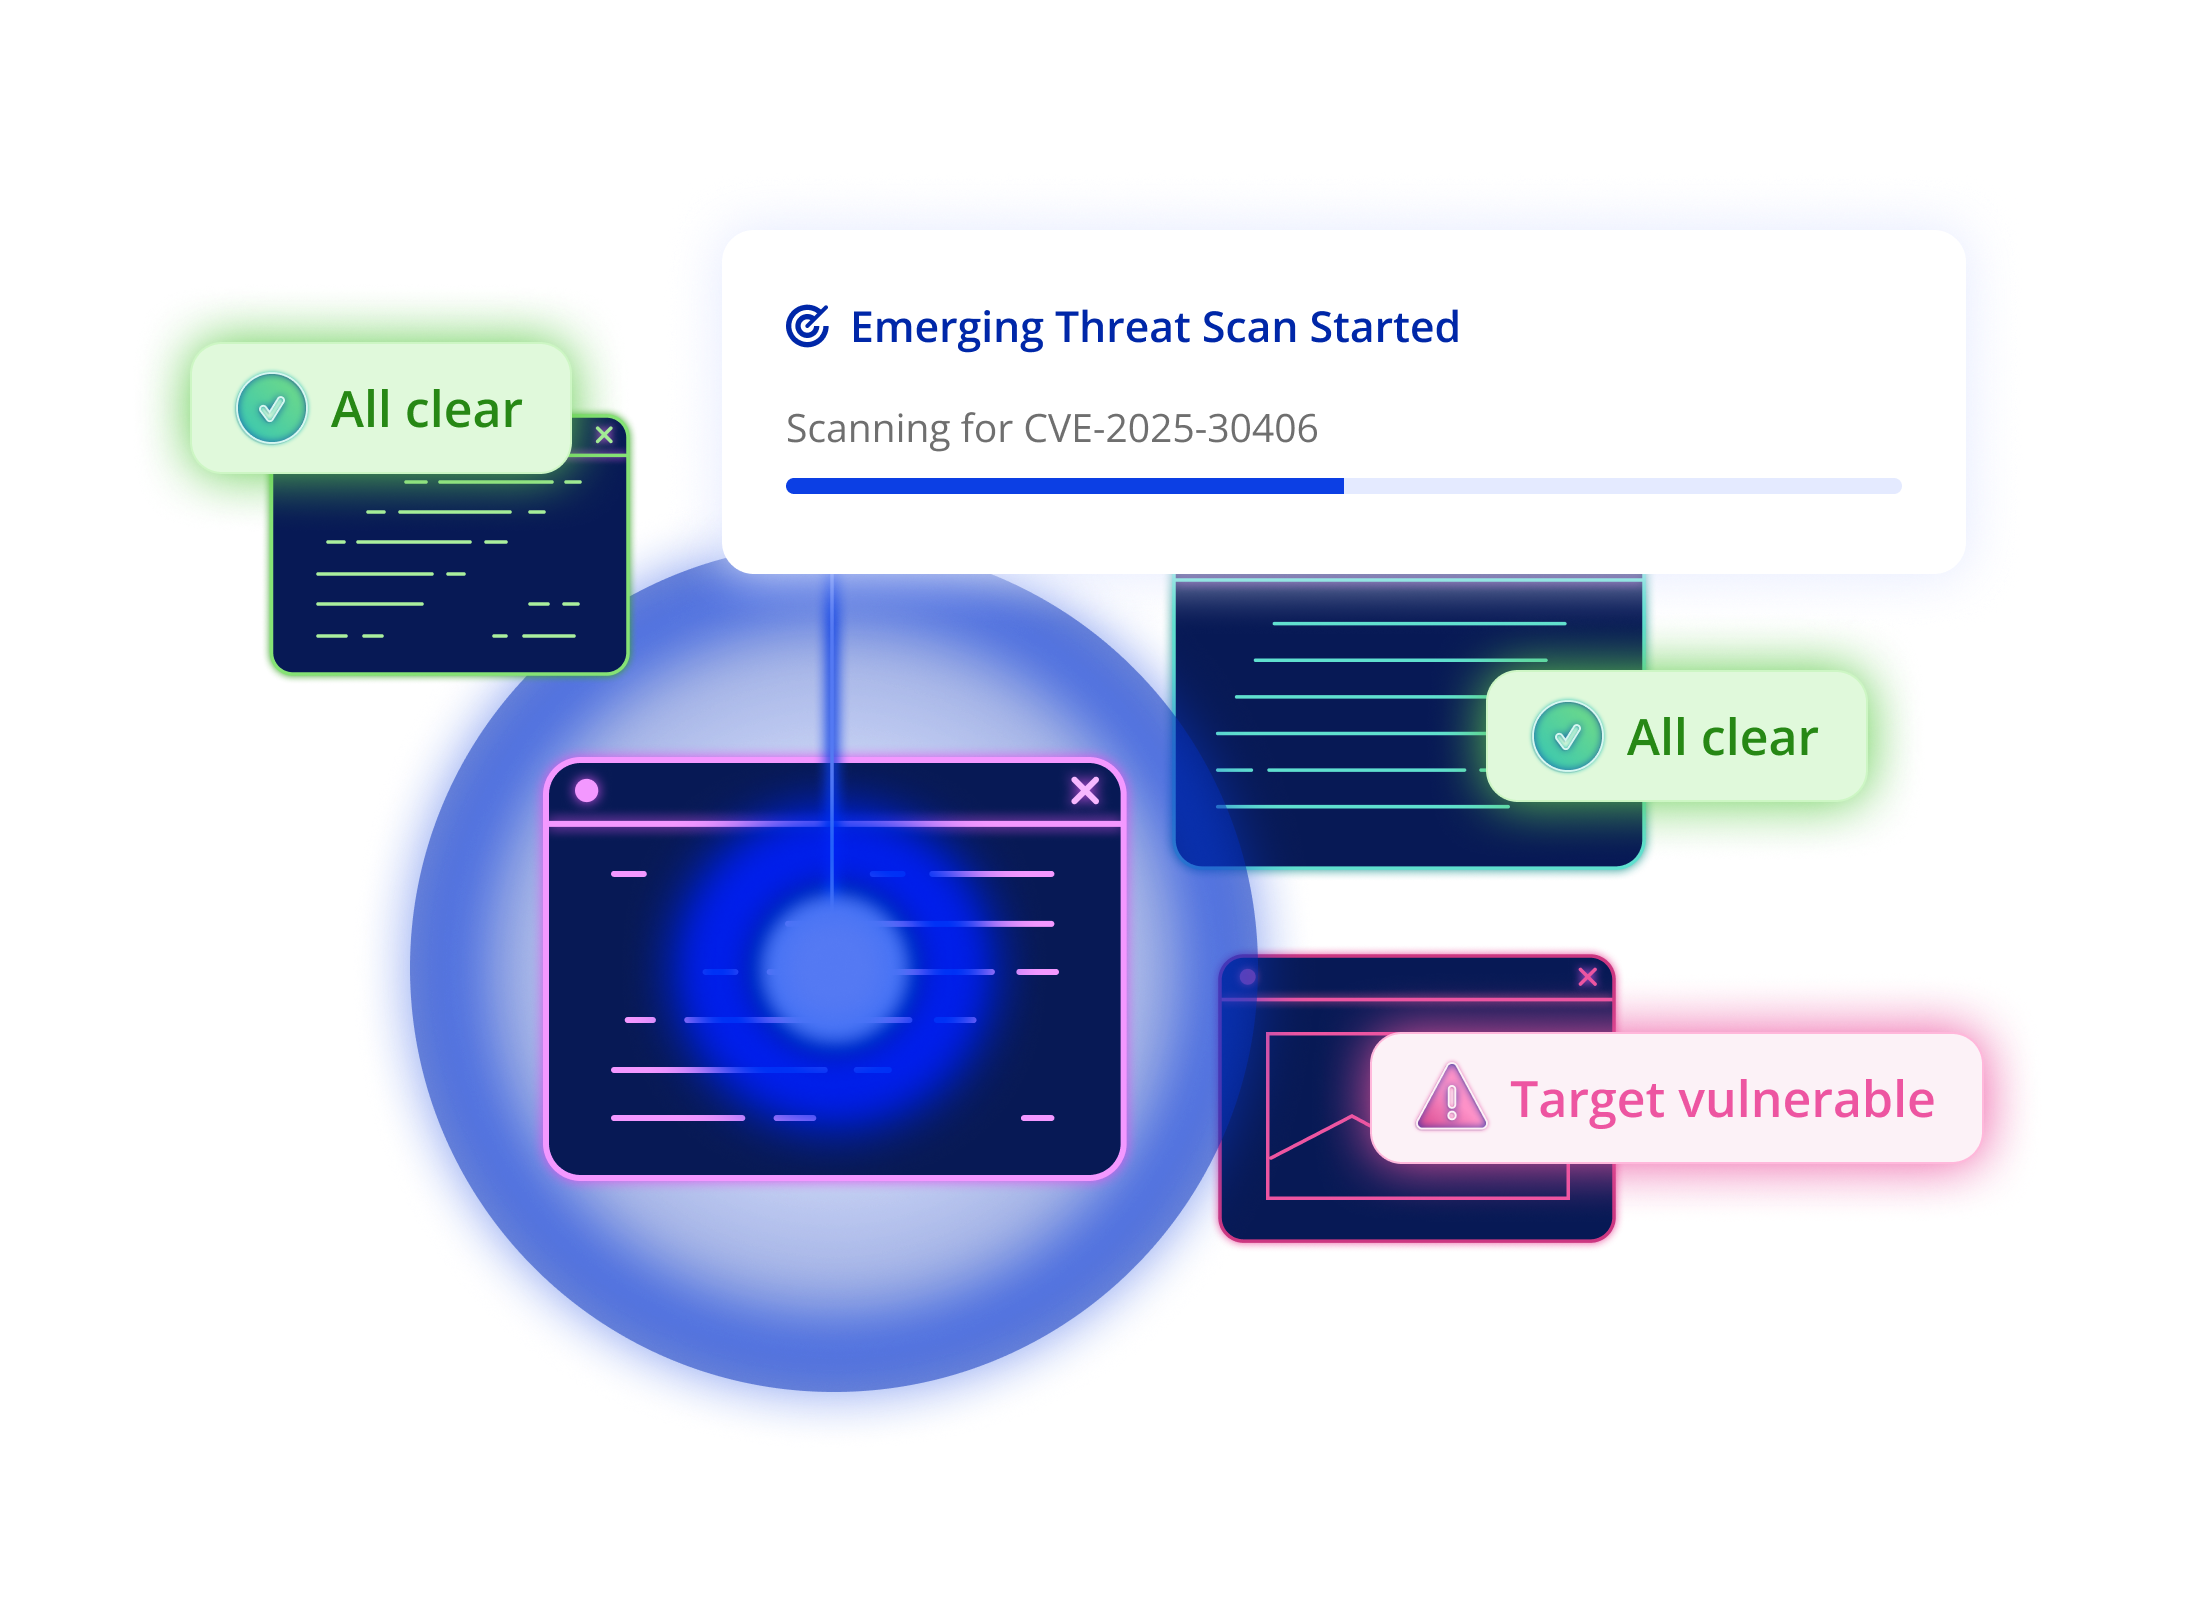
When a new vulnerability emerges, Intruder automatically checks whether you're affected and alerts you immediately.
Join 3,000+ companies securing their attack surface with Intruder






Shrink the window attackers rely on
When a new critical vulnerability drops, you need to know if you’re affected fast. Intruder automatically scans your systems - no delays, no blind spots, no manual investigating.
Reduce your exposure window
Waiting for your next scheduled scan leaves you blind when new critical vulnerabilities emerge. Intruder’s proactive threat detection keeps you protected 24/7.
We monitor for new threats so you don’t have to
Without the right tools, staying on top of new vulnerabilities can be a full time job. Intruder tracks the latest threats and acts quick to keep you secure, so you can stop doomscrolling on X.
Know if you’re vulnerable without lifting a finger
Up and running in minutes

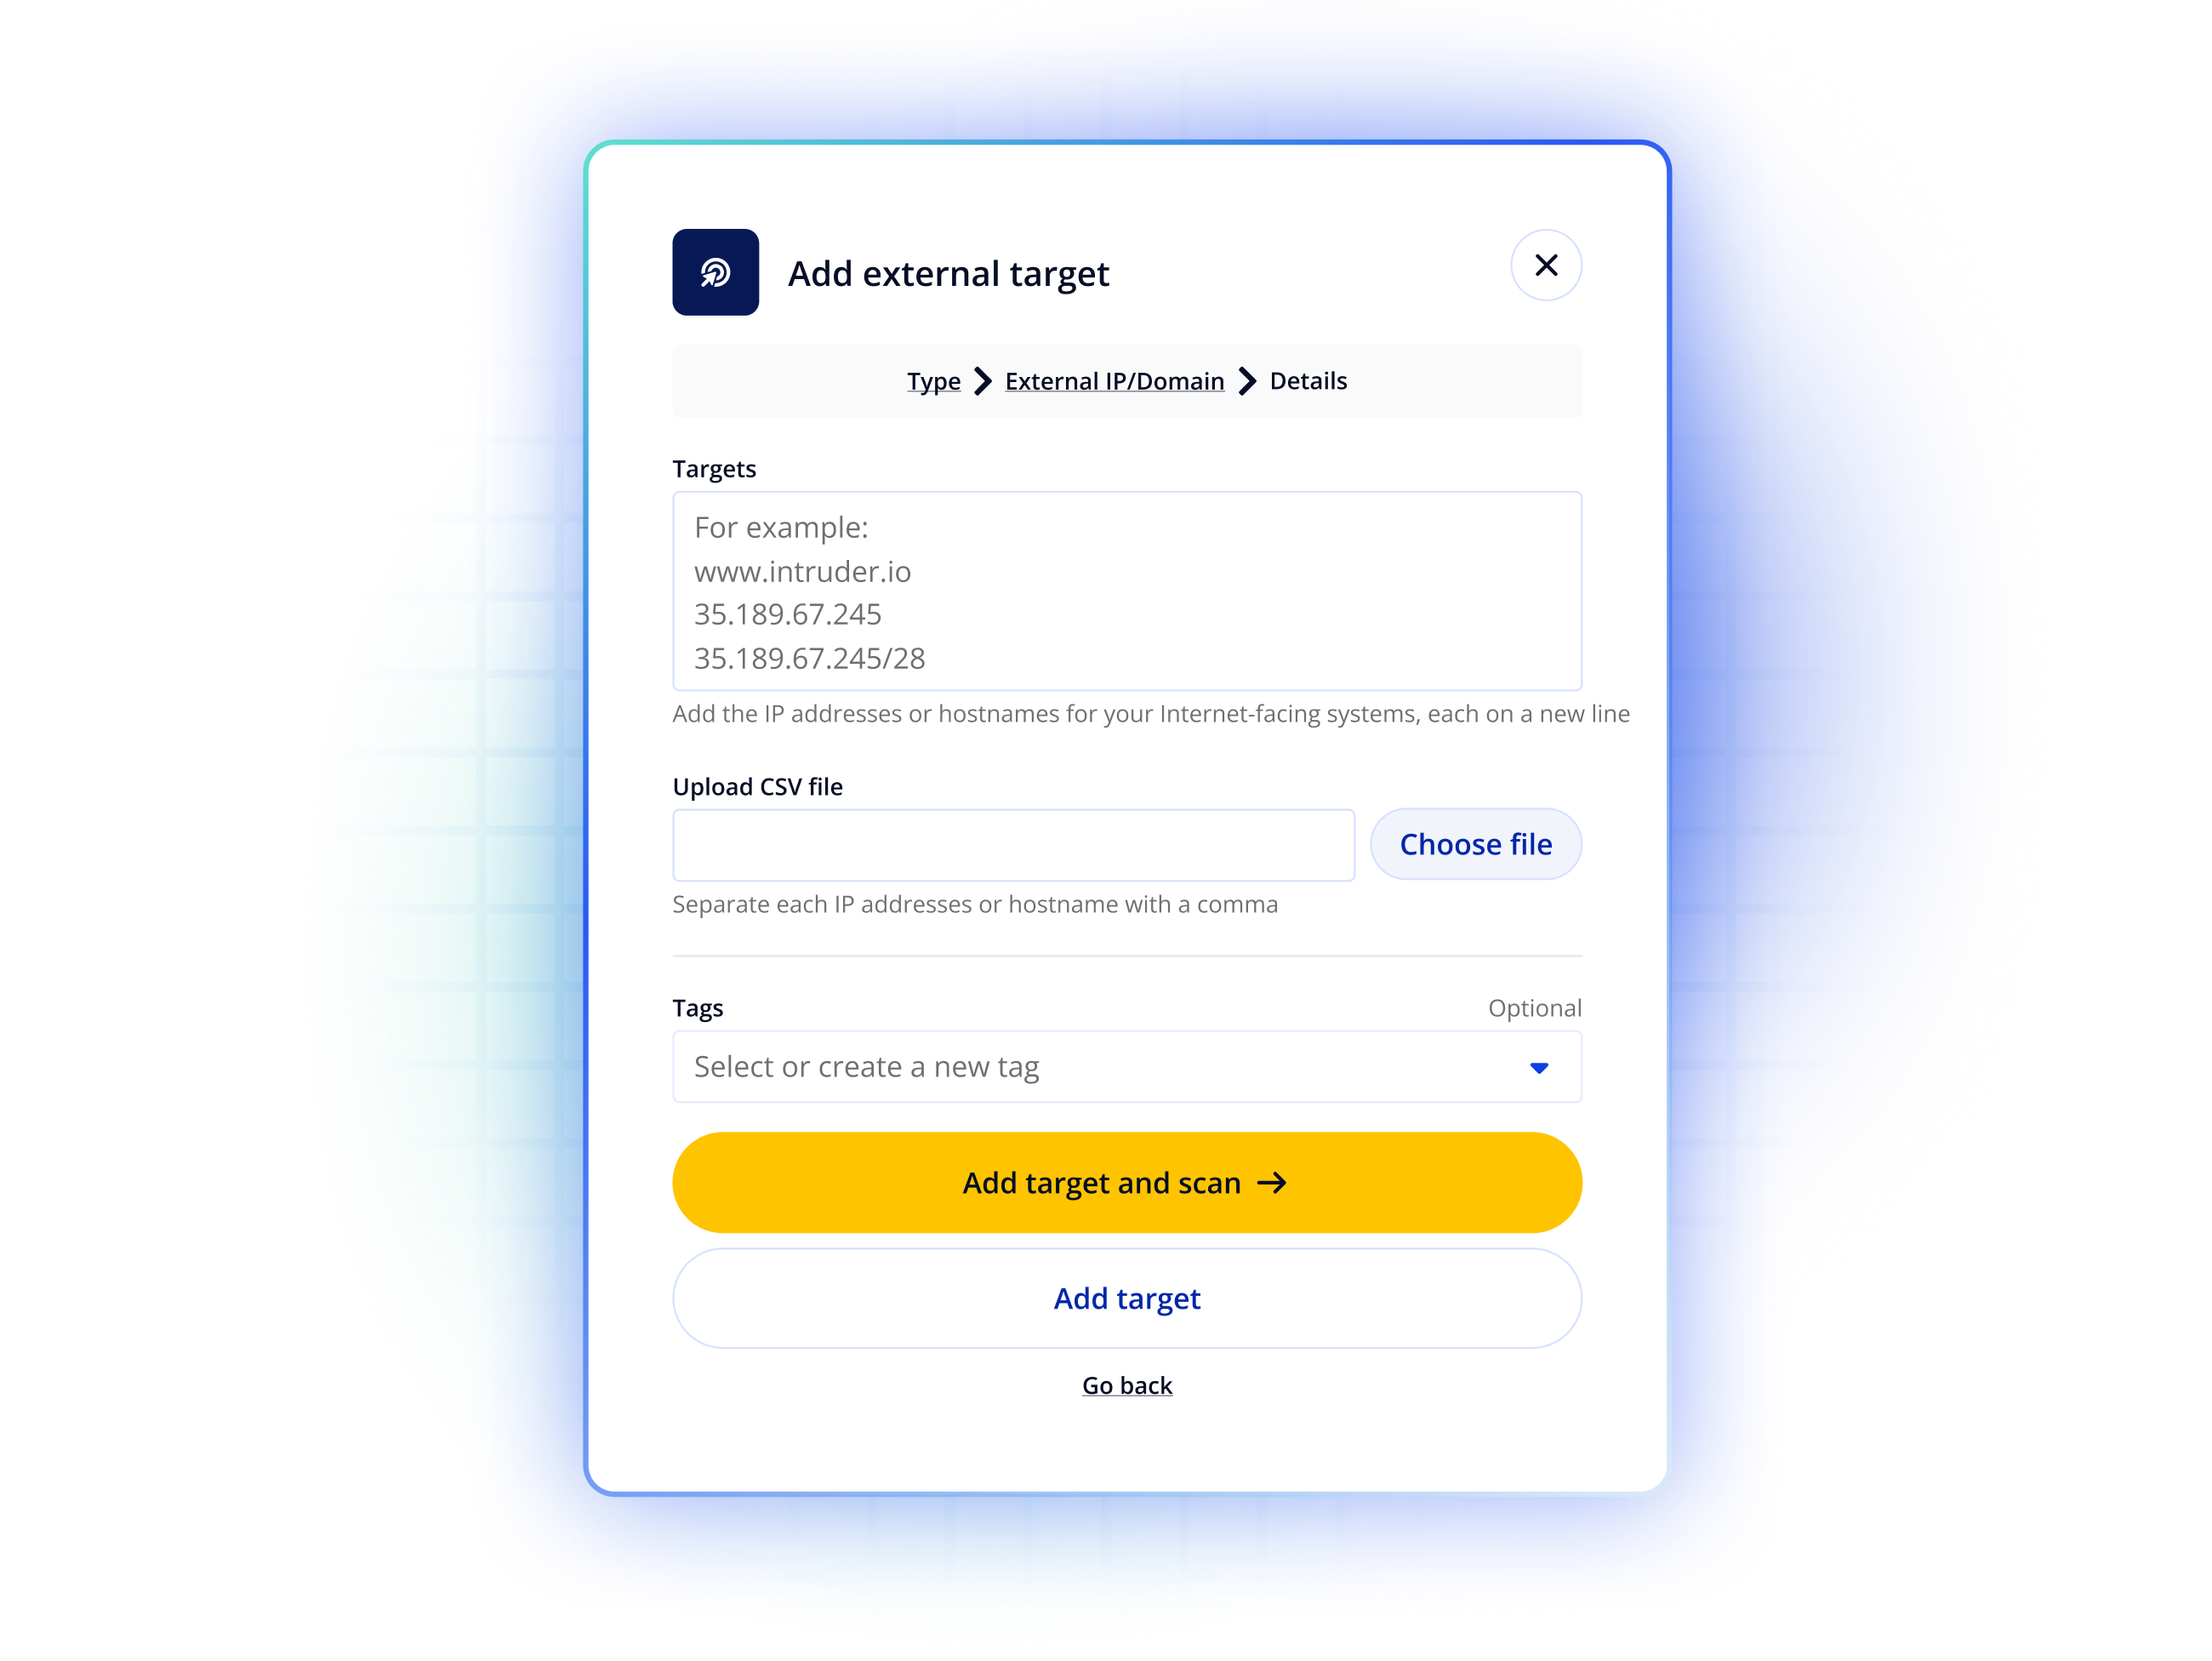
Get started with just an IP address. Once your targets are added, emerging threat scans will kick off automatically..
From finding to fix, fast
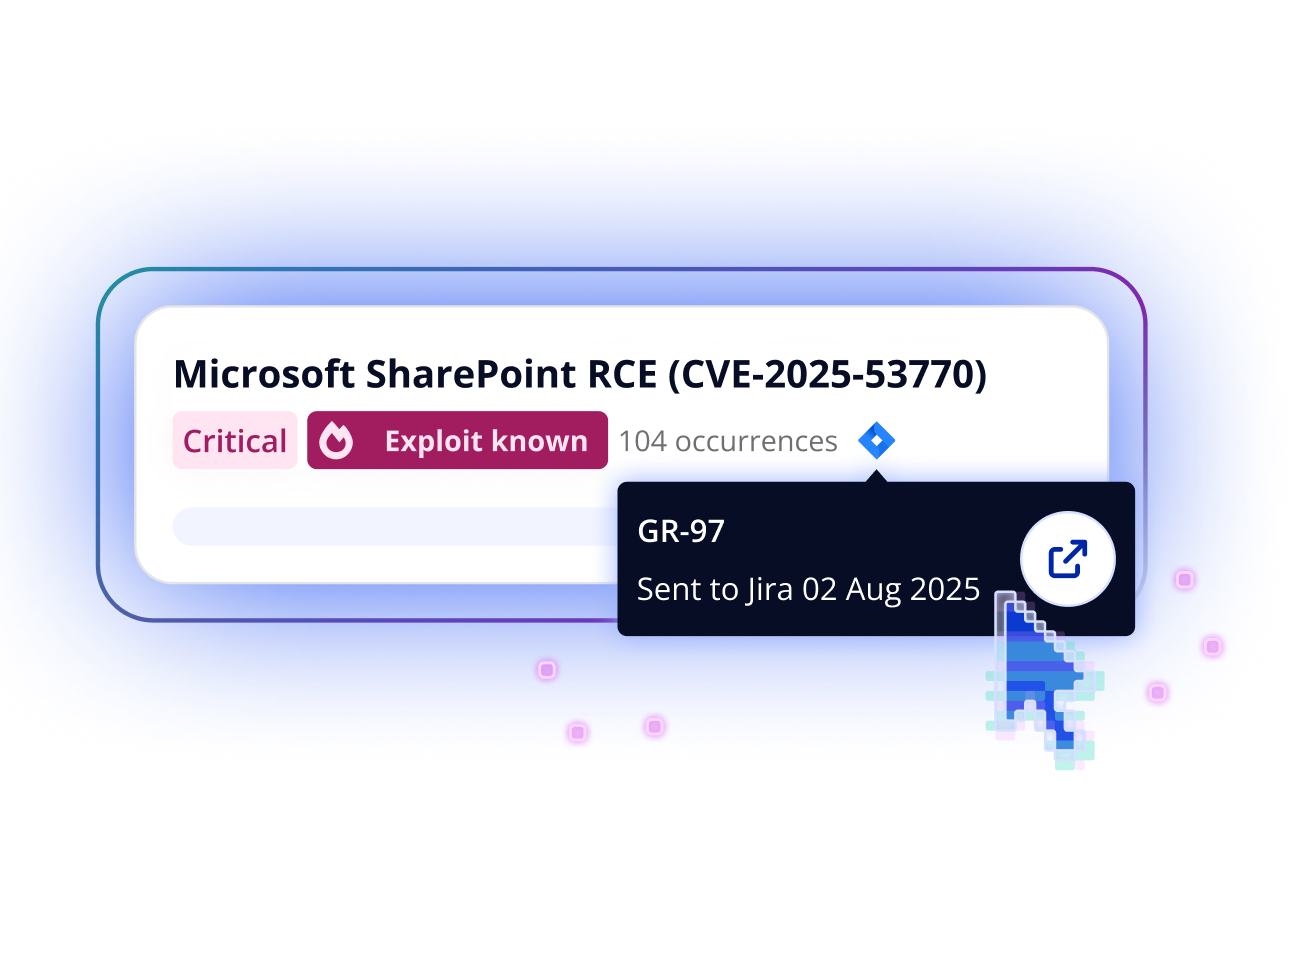
Every finding comes with step-by-step remediation advice. Push issues directly to Jira, GitHub, GitLab, Azure DevOps, or ServiceNow to get them into the right hands fast.
Stay in the loop without checking in
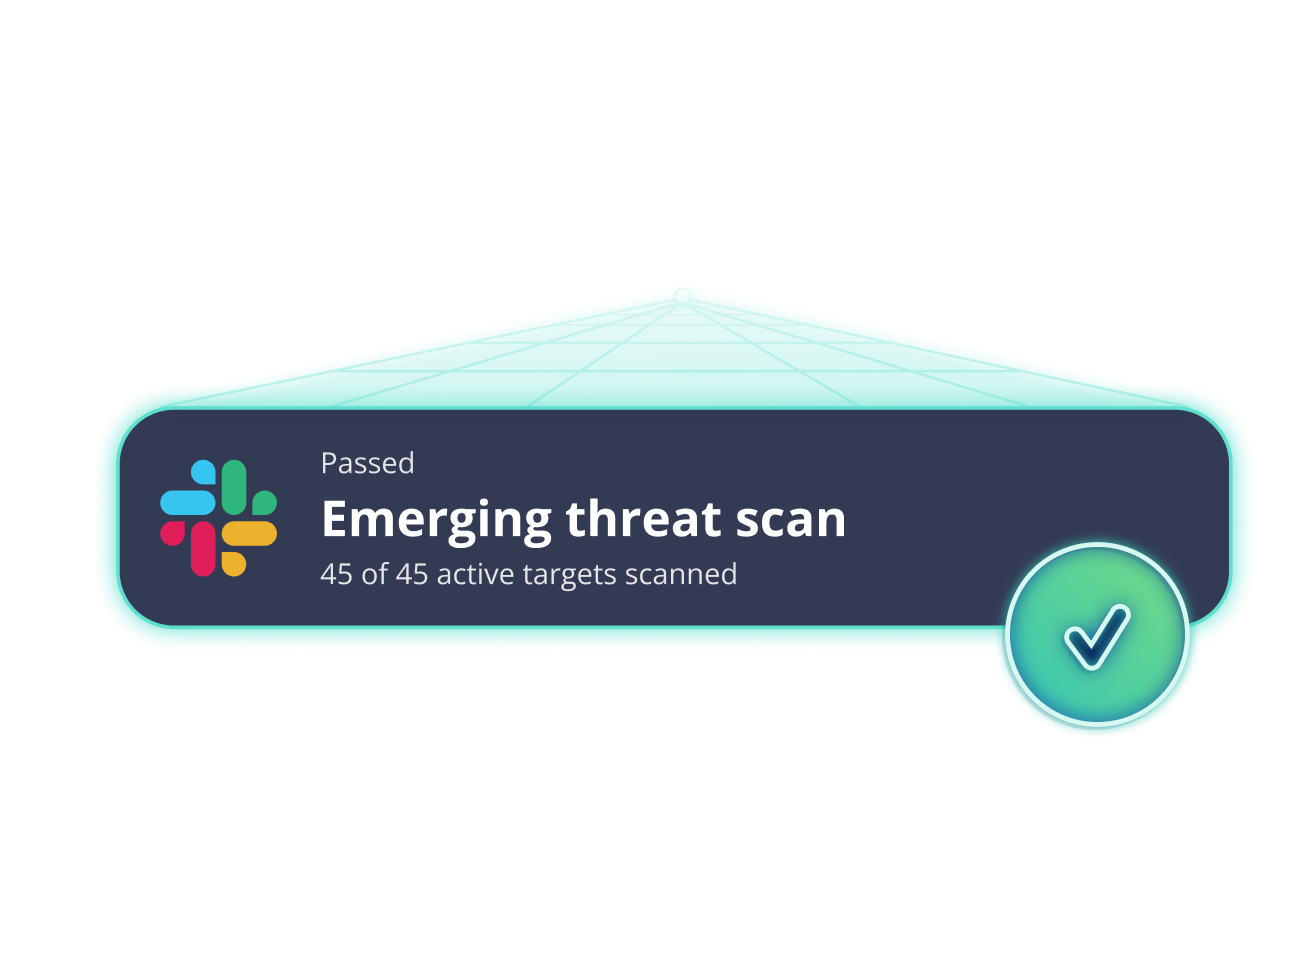
Get notified the moment a scan completes. Set up alerts via email, Slack, or Teams so nothing slips through while you're heads-down on something else.
Find what's exposed, fix what matters, and stay ahead of new threats
External Scanning
Infrastructure Security
Attack Surface Monitoring
Respond to changes

CSPM
Daily cloud config checks

Asset Discovery
Reveal unknown targets

DAST
Secure web apps

Risk Based Prioritization
No more alert fatigue

Cyber Hygiene Reporting
Demonstrate progress

Emerging Threat Detection
Check and act fast

Container Image Scanning
Automated image discovery

Secrets Detection
Prevent leaked credentials

Website Security
140k+ checks

API Security
Test your APIs

Compliance
SOC 2, ISO, HIPAA, DORA

Internal Scanning
Secure employee devices
Our customers love Intruder





One platform. Continuous security.
Emerging threat scans are automatic vulnerability checks that Intruder runs on your external targets when a new vulnerability is disclosed. You don't need to manually trigger scans every time something drops. Learn more about emerging threat scans.
Scheduled scans run on a recurring basis and check against the full database of known vulnerabilities. Emerging threat scans are reactive. They trigger automatically when a specific new vulnerability is disclosed, so you don't have to wait for your next scheduled scan to find out if you're affected.
Any new external vulnerability rated medium, high, or critical. In practice, these are the vulnerabilities that make the news, like critical RCE flaws in Ivanti EPMM (CVE-2026-1281, CVE-2026-1340) or Microsoft SharePoint (CVE-2025-53770). Learn more.
Emerging threat scans are available on Cloud, Pro, and Enterprise plans. Enterprise customers get priority scanning, meaning their targets are checked first when a new threat is identified. See all plans.