
API security testing that confirms what’s exploitable
Automated vulnerability scanning for your REST APIs. Upload your API schema and test it against 100 checks, from SQL injection to cross-site scripting. Cut time spent on false positives with AI-powered issue validation.
Join 3,000+ companies securing their attack surface with Intruder






Know which findings are worth your time
Cut the false positive triage. Intruder’s AI agents confirm whether a finding can be exploited, so you only send developers the real problems.
Catch weaknesses before they ship
Intruder’s API lets you scan your test environment from your CI/CD pipeline, so issues can get fixed during development instead of patched in a hurry after release.
Always audit-ready
Generate reports for auditors and customers, or send evidence straight to Drata or Vanta. Audit prep stops eating your week.
Scan your APIs in CI/CD and fix what’s exploitable first
Get started in minutes

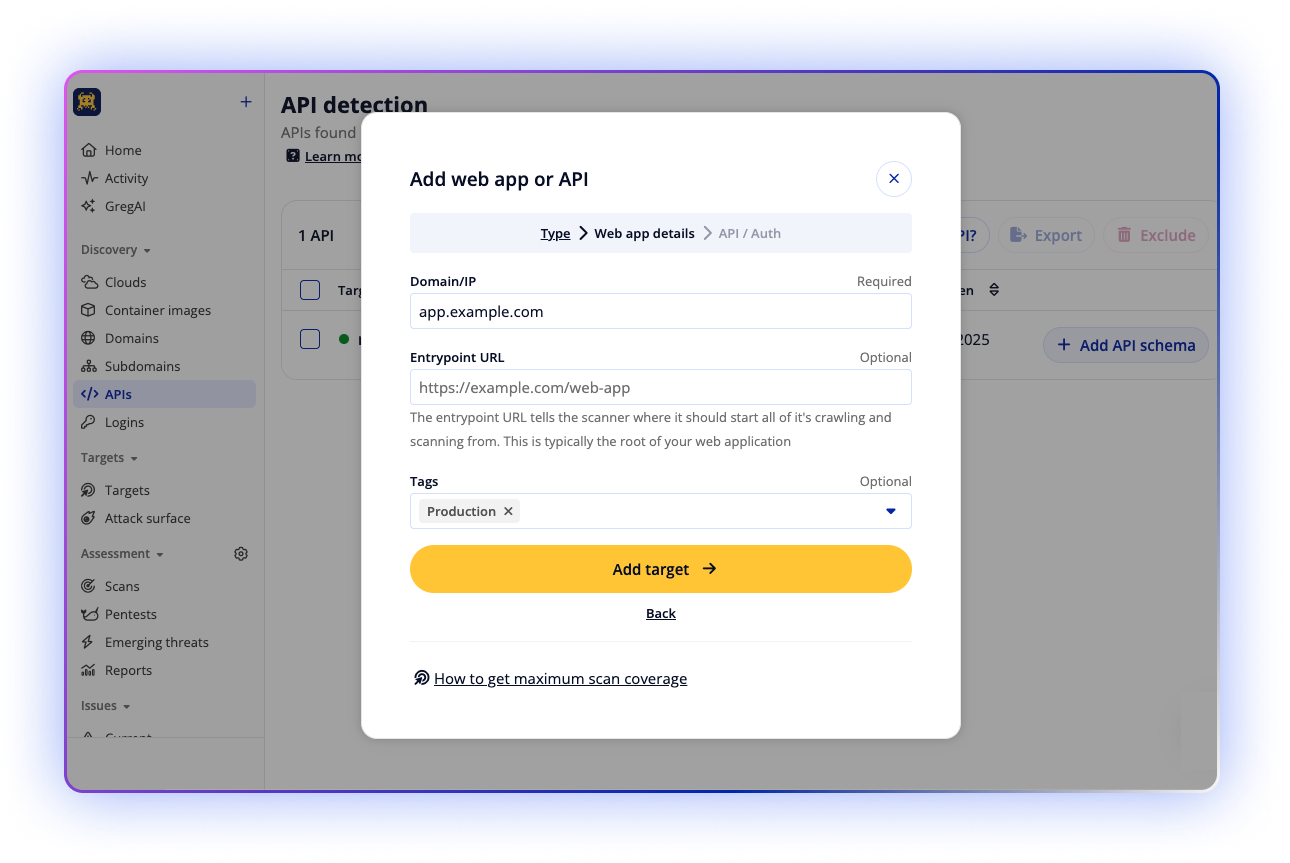
Upload your OpenAPI or Swagger schema and add authentication to scan endpoints behind logins.
Scheduled scans, server included
Run API scans on a recurring schedule or on-demand. Intruder also checks the server hosting your API for outdated software, missing patches, and encryption weaknesses.
Prioritize and fix
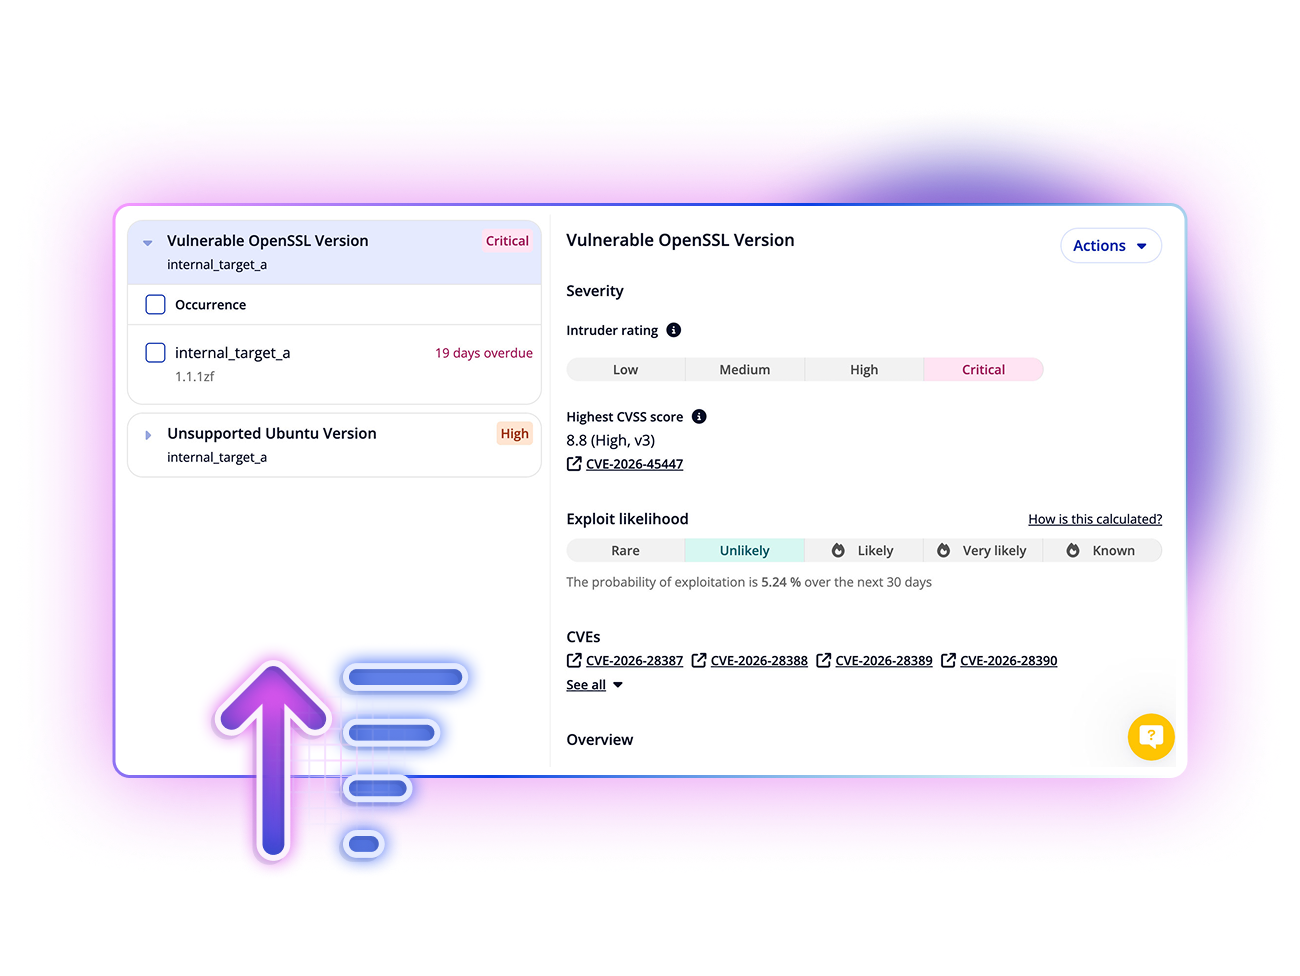
Results are prioritized by CVSS and exploit likelihood. Send them to Jira, GitHub, or Azure DevOps, and rescan individual issues to confirm your fixes worked.

Find what's exposed, fix what matters, and stay ahead of new threats
External Scanning
Infrastructure Security
Attack Surface Monitoring
Respond to changes

CSPM
Daily cloud config checks

Asset Discovery
Reveal unknown targets

DAST
Secure web apps

Risk Based Prioritization
No more alert fatigue

Cyber Hygiene Reporting
Demonstrate progress

Emerging Threat Detection
Check and act fast

Container Image Scanning
Automated image discovery

Secrets Detection
Prevent leaked credentials

Website Security
140k+ checks

API Security
Test your APIs

Compliance
SOC 2, ISO, HIPAA, DORA

Internal Scanning
Secure employee devices
Our customers love Intruder





One platform. Continuous security.
Intruder integrates with Jira, GitHub, GitLab, Azure DevOps, and ServiceNow for issue tracking, Slack and Microsoft Teams for alerts, Drata and Vanta for compliance, and Microsoft Sentinel for SIEM. See all our integrations.
Intruder runs 100 application-level checks against every endpoint defined in your schema, covering SQL injection, NoSQL injection, XSS, OS command injection, LDAP injection, server-side code injection, and more. Every scan also checks the server hosting your API for outdated software, missing patches, and encryption weaknesses. See the full list of checks.
Intruder supports OpenAPI and Swagger schemas. Upload your schema and Intruder scans every endpoint defined in it. Without a schema, Intruder still runs infrastructure-level checks against the server hosting your API. See how to upload your schema.
Yes. Intruder's API lets you trigger scans from your CI/CD pipeline, so you can catch vulnerabilities during development rather than after release. See the API documentation.
Intruder's AI agents validate whether a finding can be genuinely exploited before it's reported, so developers only see the real problems. Learn more about AI issue validation.