
DAST that respects your time
Intruder’s DAST scanner runs 100 checks across authenticated web apps and APIs, finding vulnerabilities like SQL injection, XSS, and CSRF before attackers do.
Join 3,000+ companies securing their attack surface with Intruder






Find vulnerabilities where they hide
Authenticated pages and APIs are where the most sensitive functionality lives. Intruder scans them so nothing exploitable goes undetected.
Act fast on what needs your attention
Intruder filters out noise and prioritizes by risk. No alert fatigue, just clarity on what actually matters.
Less chasing, more fixing
Issues are explained in plain English with step-by-step remediation advice to help devs fix without waiting on security.
Security that moves at the speed of your sprints
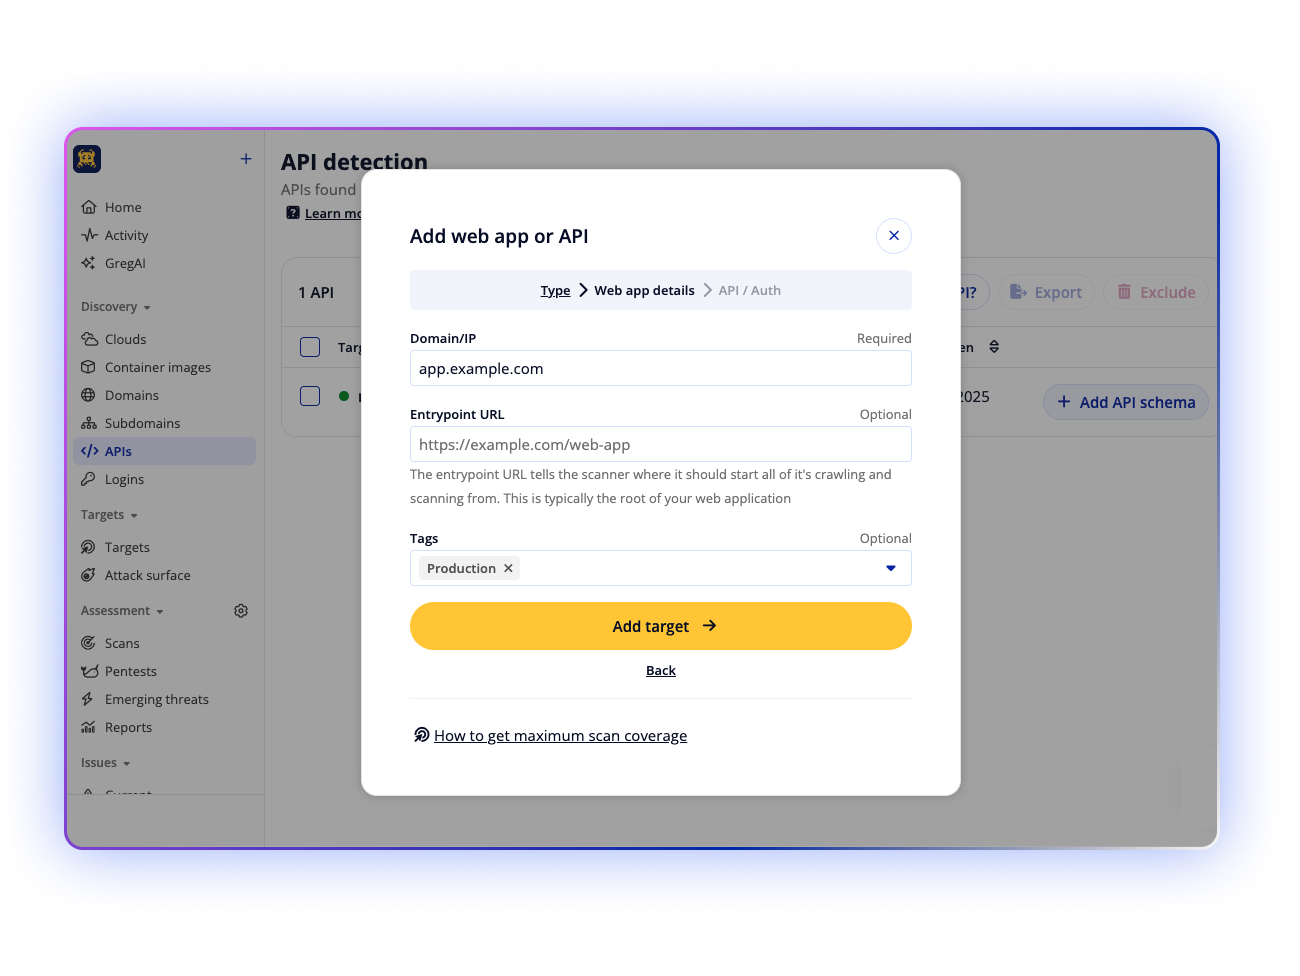
Simple to set up, however your app is built

Get started with just a domain or IP. Intruder supports custom and complex web apps (including SPAs) and a wide range of authentication methods. Scan every API endpoint by uploading your OpenAPI or Swagger schema.
From finding to fix, without the friction
Schedule scans to match your release cadence. Push issues directly to Jira, GitHub, GitLab, Azure DevOps, or ServiceNow, and integrate into your CI/CD pipeline via our API. Verify fixes quickly with targeted rescans.
Compliance evidence, ready to go
Download reports to meet SOC 2 and ISO 27001 compliance requirements. Send vulnerability scan evidence directly to Drata or Vanta.

Find what's exposed, fix what matters, and stay ahead of new threats
External Scanning
Infrastructure Security
Attack Surface Monitoring
Respond to changes

CSPM
Daily cloud config checks

Asset Discovery
Reveal unknown targets

DAST
Secure web apps

Risk Based Prioritization
No more alert fatigue

Cyber Hygiene Reporting
Demonstrate progress

Emerging Threat Detection
Check and act fast

Container Image Scanning
Automated image discovery

Secrets Detection
Prevent leaked credentials

Website Security
140k+ checks

API Security
Test your APIs

Compliance
SOC 2, ISO, HIPAA, DORA

Internal Scanning
Secure employee devices
Our customers love Intruder





One platform. Continuous security.
Dynamic Application Security Testing (DAST) scans a running web application from the outside, the same way an attacker would probe it. Unlike static analysis, which looks at code, DAST tests the live app for vulnerabilities that only appear at runtime, like SQL injection and XSS. Intruder runs 100 DAST checks across authenticated web apps and APIs.
Intruder's scanning engines are configured to be safe to use. For authenticated web app scanning, we recommend scanning test environments or those connected to a test harness. More info.
Intruder supports form-based login, HTTP authentication, header-based auth, session cookies, OAuth 2.0, and recorded login flows — so you can scan behind SSO, multi-step logins, and complex authentication setups. More info.
Yes — Intruder scans REST APIs (Swagger and OpenAPI). Upload your schema and Intruder scans every endpoint. More info.
Yes — Intruder's scanner runs SPAs in a headless browser. More info.
Yes — Intruder's DAST and infrastructure scans find OWASP issues, including web application vulnerabilities, cryptographic weaknesses, security misconfigurations, and infrastructure vulnerabilities. Find out more about external infrastructure scans.
Intruder integrates with Jira, GitHub, GitLab, Azure DevOps, and ServiceNow for issue tracking, Slack and Microsoft Teams for alerts, Drata and Vanta for compliance, and Microsoft Sentinel for SIEM. See all our integrations.