
AI pentesting that reads your code and proves what's actually exploitable
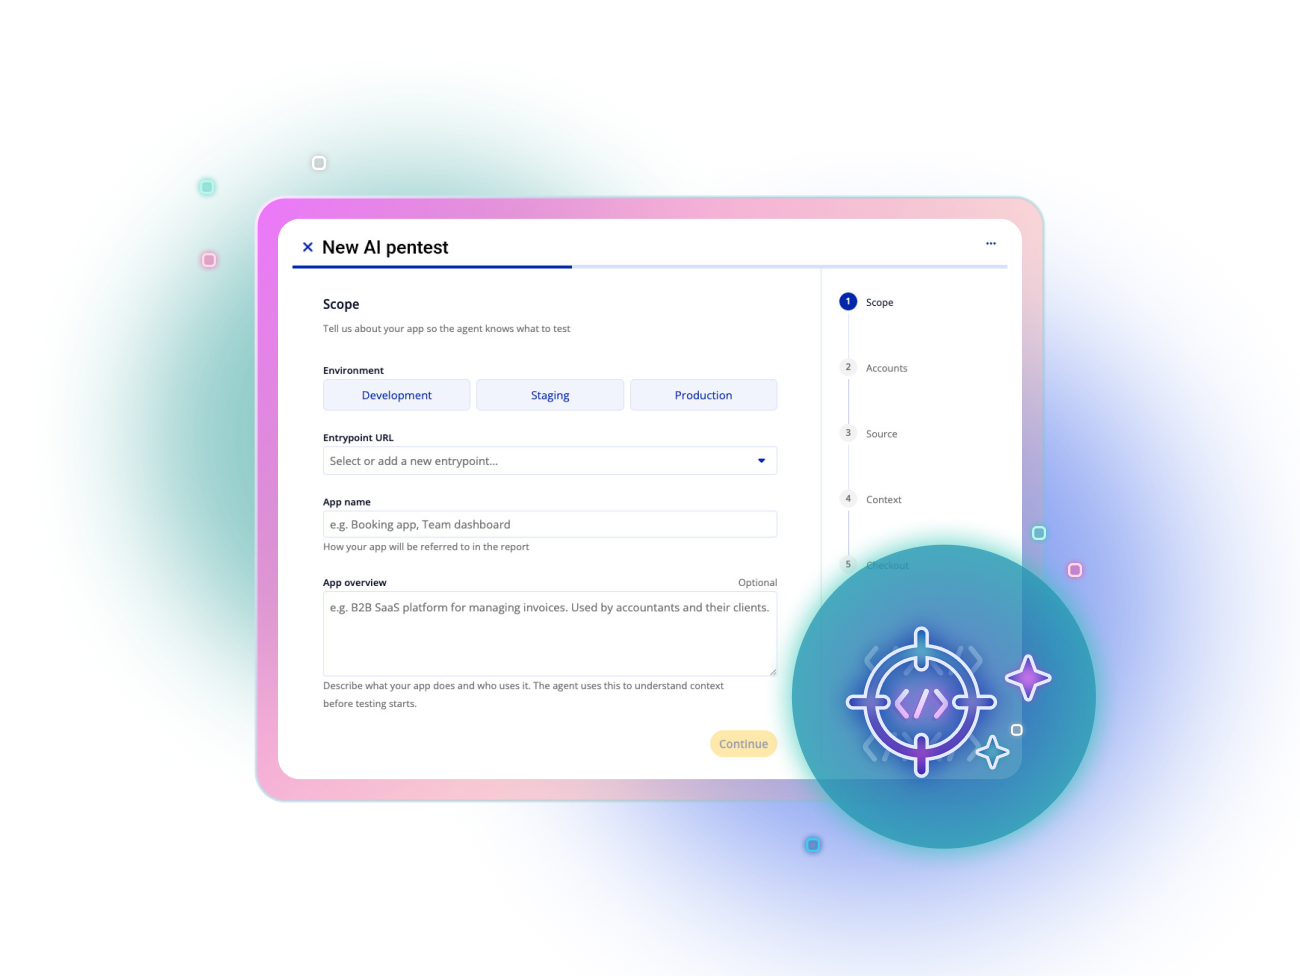
Intruder's AI agents test your web apps on-demand with white-box access to your repo. Run one on every major release, get an audit-ready report in hours.
Join 3,000+ companies securing their attack surface with Intruder






The depth a manual pentest can miss
AI SAST across your repo lets the agents use your code to go deeper than a human tester can. Our AI pentesting agents have found issues that survived multiple years of human penetration tests.
Results in hours, not weeks
Scope a test and the agents start straight away. A full report lands in hours, not the weeks a manual engagement takes to schedule and run.
A pentest budget that goes further
An AI pentest costs a fraction of a manual engagement. Instead of one assessment a year, you can run one whenever you need it.
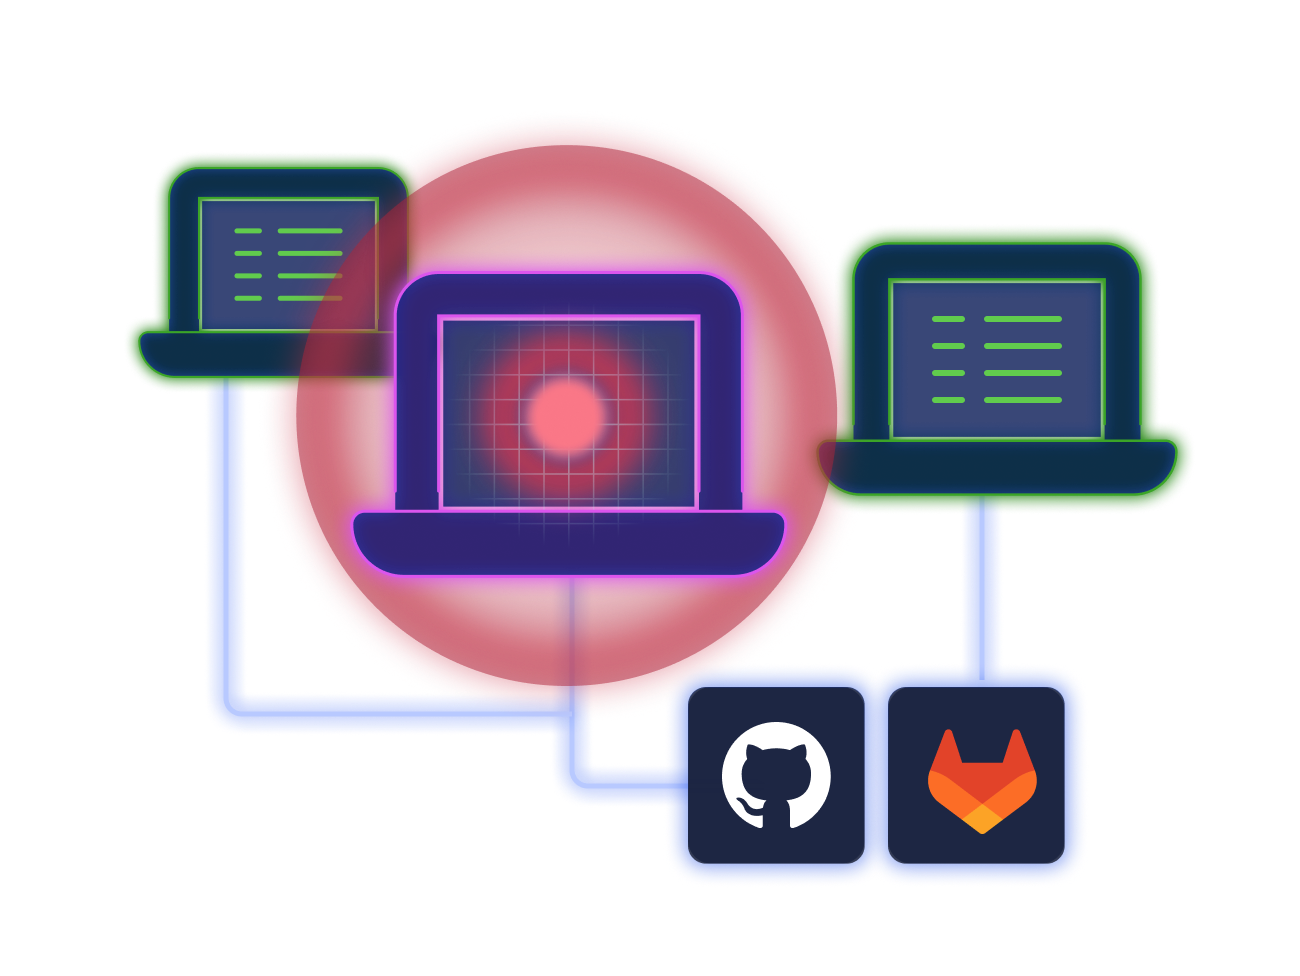
Keep security and engineering in lockstep
From repo to runtime, in one test

Connect your GitHub or GitLab repo and the agents run AI SAST across your source code, then test each finding against the app to prove what's exploitable. That white-box approach is what gives the test its depth, reaching issues an annual engagement can leave sitting for years.
Separate exploitable issues from theoretical ones
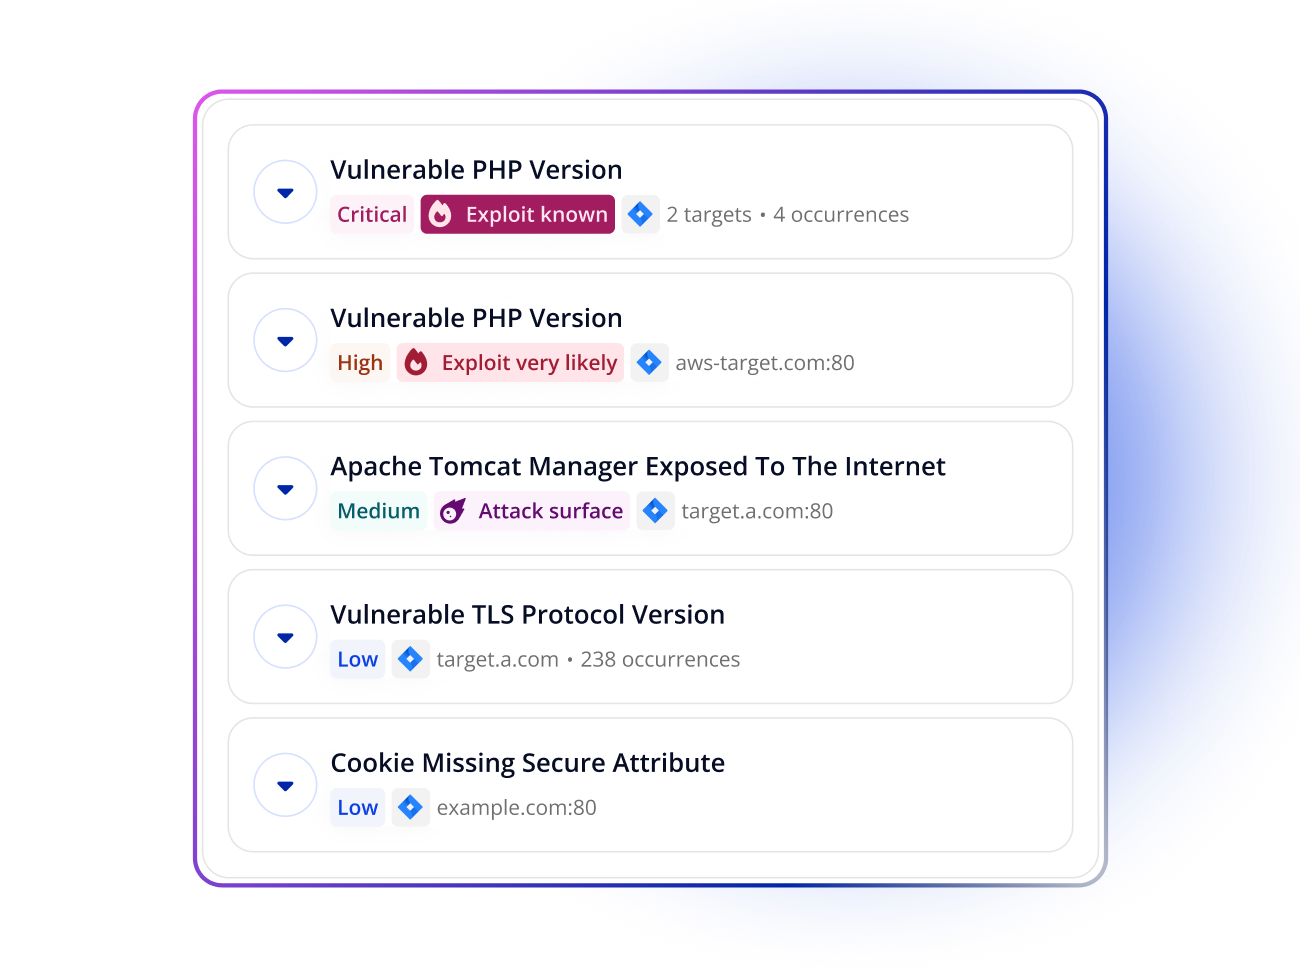
The agents investigate each finding the way an experienced pentester would, running the exploit against your app to confirm it works before it's ever reported. You get proof-of-concept code with it, so your team can reproduce the issue rather than take our word for it.
Get a report you can act on in hours
You get a summary, the detailed findings with the exact line of code behind each one, and a full transcript of every step the agent took, so you and your auditor can see exactly what was tested and what was found.
Find what's exposed, fix what matters, and stay ahead of new threats
External Scanning
Infrastructure Security
Attack Surface Monitoring
Respond to changes

CSPM
Daily cloud config checks

Asset Discovery
Reveal unknown targets

DAST
Secure web apps

Risk Based Prioritization
No more alert fatigue

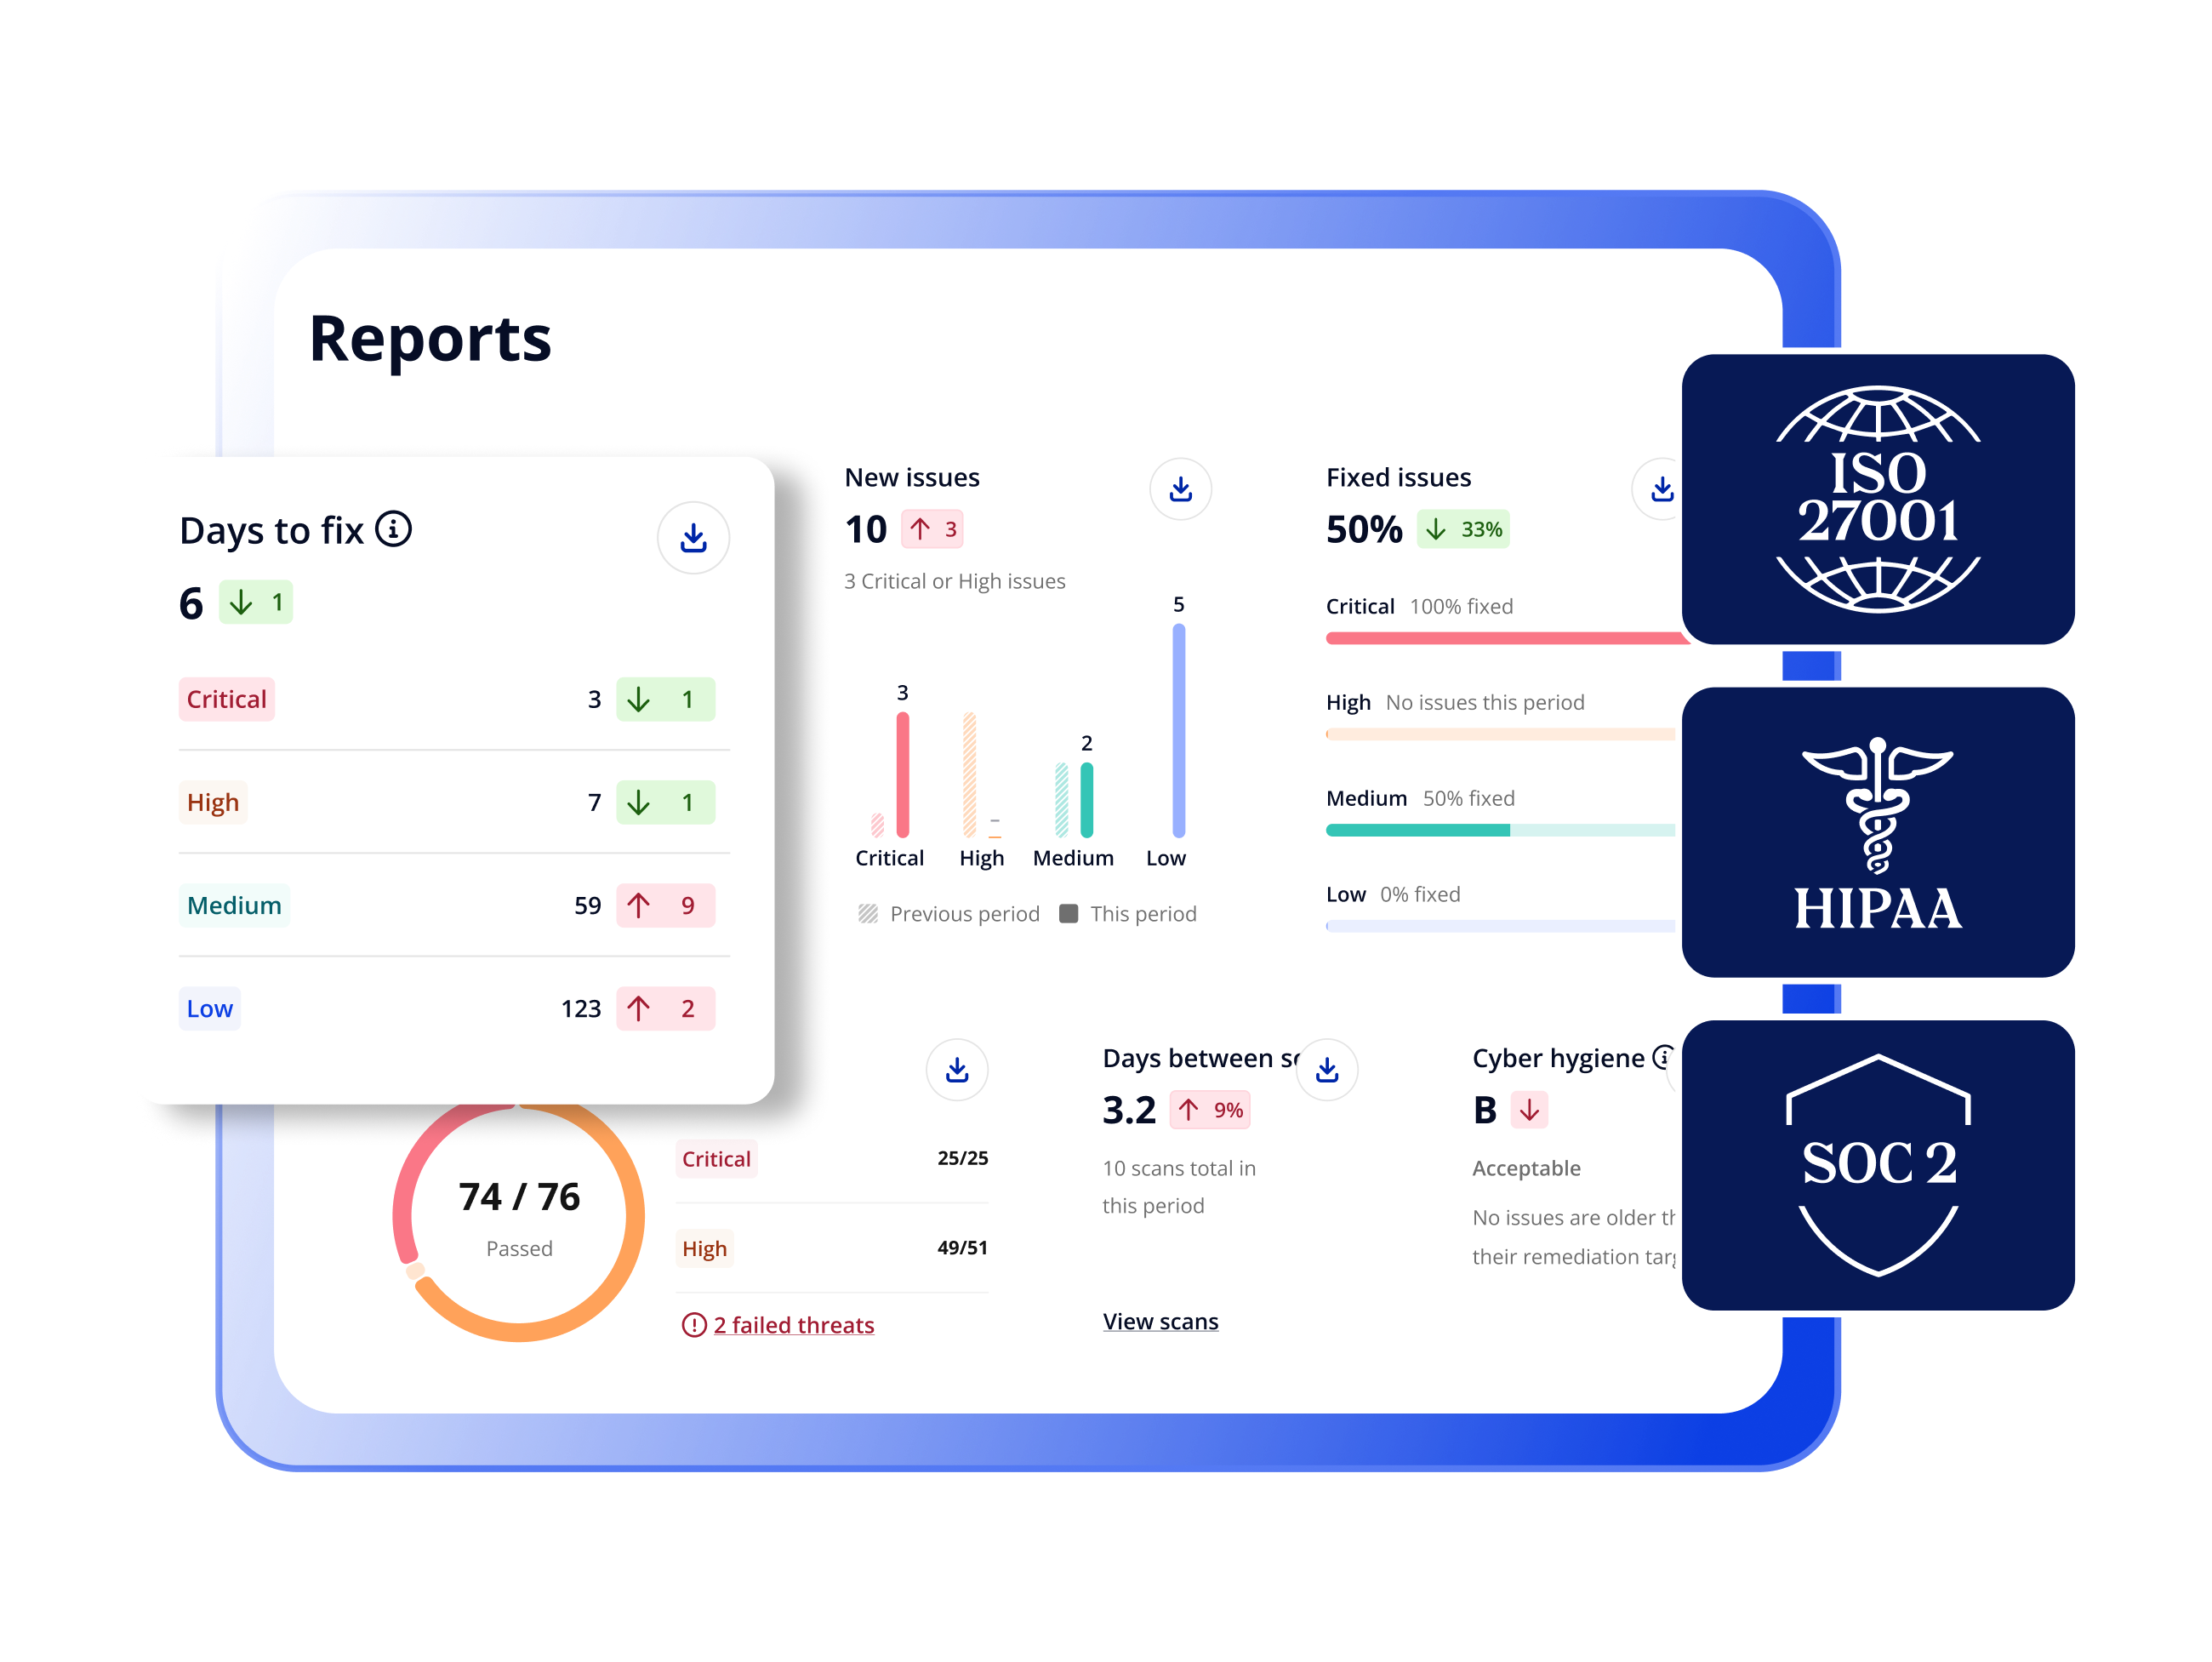
Cyber Hygiene Reporting
Demonstrate progress

Emerging Threat Detection
Check and act fast

Container Image Scanning
Automated image discovery

Secrets Detection
Prevent leaked credentials

Website Security
140k+ checks

API Security
Test your APIs

Compliance
SOC 2, ISO, HIPAA, DORA

Internal Scanning
Secure employee devices
Our customers love Intruder





One platform. Continuous security.
AI web app pentesting uses autonomous AI agents to test your application the way a skilled human pentester would, reasoning through how it behaves, finding vulnerabilities, and validating that each one is genuinely exploitable. Intruder takes a white-box approach, working from your source code for deeper coverage. Learn more about how it works.
AI pentesting is as safe to run as a human-led pentest. Neither is completely risk-free, so the same precautions apply: test in staging rather than production, keep validated backups, and make sure your disaster recovery works. Learn more.
A human in the loop isn't necessary for web app pentesting anymore. The reasoning and capability of current models are good enough to run without human interaction. The human expertise hasn't disappeared, it's built into the product. Intruder's agents are built and trained by CREST-certified pentesters and validate every finding against the application before it's reported. Learn more.
Intruder's AI web app pentesting starts from $3,500 per test for existing customers and $4,000 as a standalone purchase. Pricing is based on the size and complexity of your application. See AI pentest pricing.
AI SAST means using AI agents to analyze source code for security weaknesses instead of matching it against fixed rules. Intruder runs that analysis as part of a penetration test: the agents read your codebase, then prove what's exploitable against your running app.
White box. The agents get your source code and, when you supply them, working credentials, which is the deepest access a pentest can have. Grey box testing works from credentials and partial knowledge without the code, so it cannot trace a flaw back to the line that caused it.
Full AI web app pentests are bought per test, so you can run as many as you need rather than being capped by plan. See our AI pentest pricing for current rates. Separately, issue-level AI Pentest investigations, which validate individual scanner findings, run on monthly credits by plan: 5 on Cloud, 10 on Pro, and 50 on Enterprise.