
Detect and secure new assets and shadow IT
Find new assets that never made it onto your asset register and integrate them into your security program without lifting a finger.
Join 3,000+ companies securing their attack surface with Intruder






Complete attack surface visibility
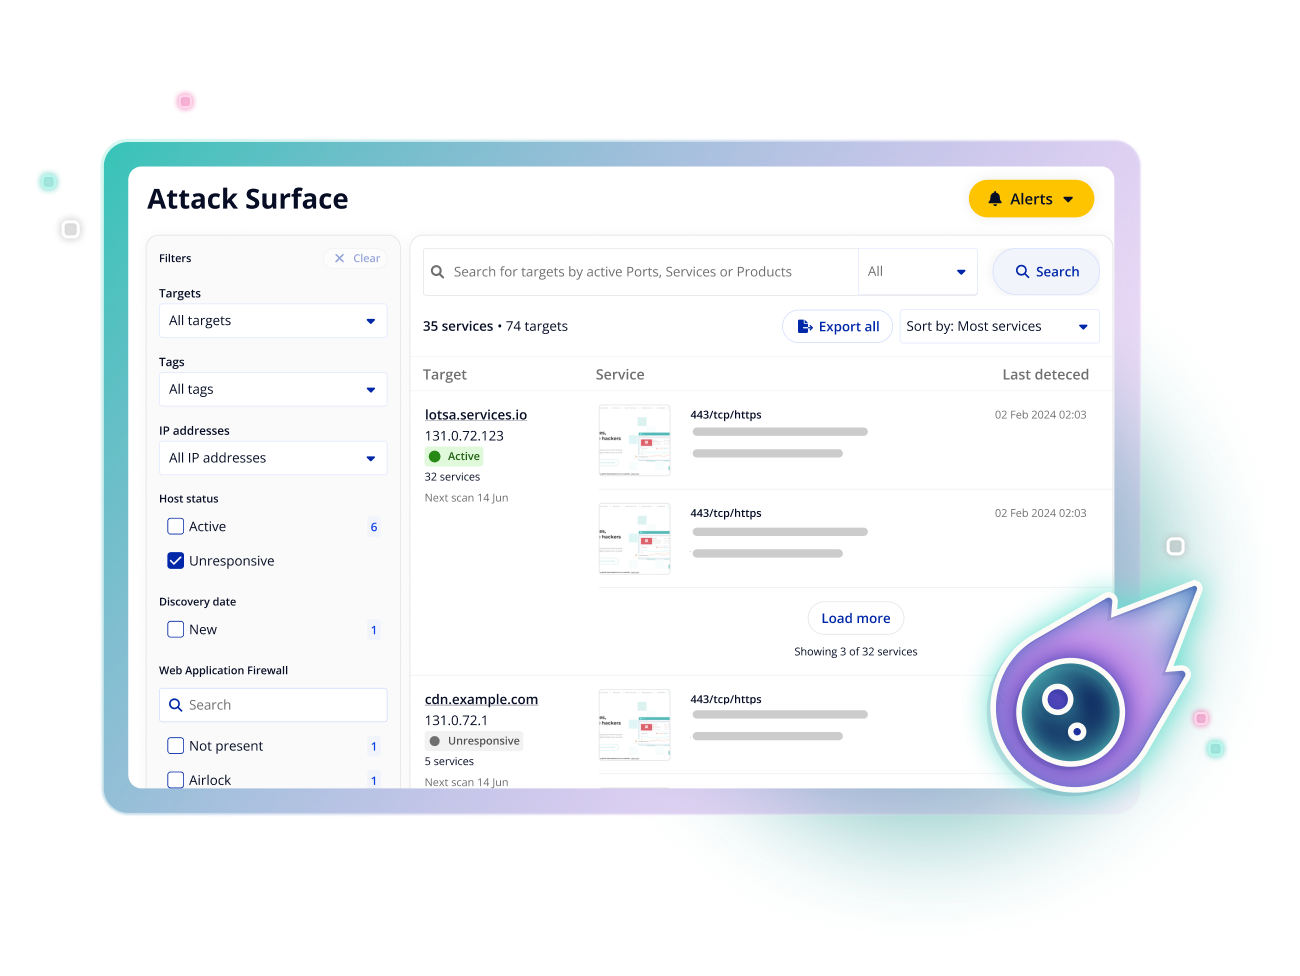
Manual asset inventories are only as reliable as the people responsible for updating them. Automated monitoring catches new assets and services as soon as they pop up.
Keep up with every deploy
Engineering teams are moving faster than ever, security needs to keep up. Intruder discovers APIs, logins, subdomains, and cloud services you don’t know exist.
Scale security with confidence
New domains, acquisitions, expanding cloud footprint - as your business grows, your attack surface grows with it. Intruder keeps your coverage from falling behind.
Secure your external perimeter
Connect your environment

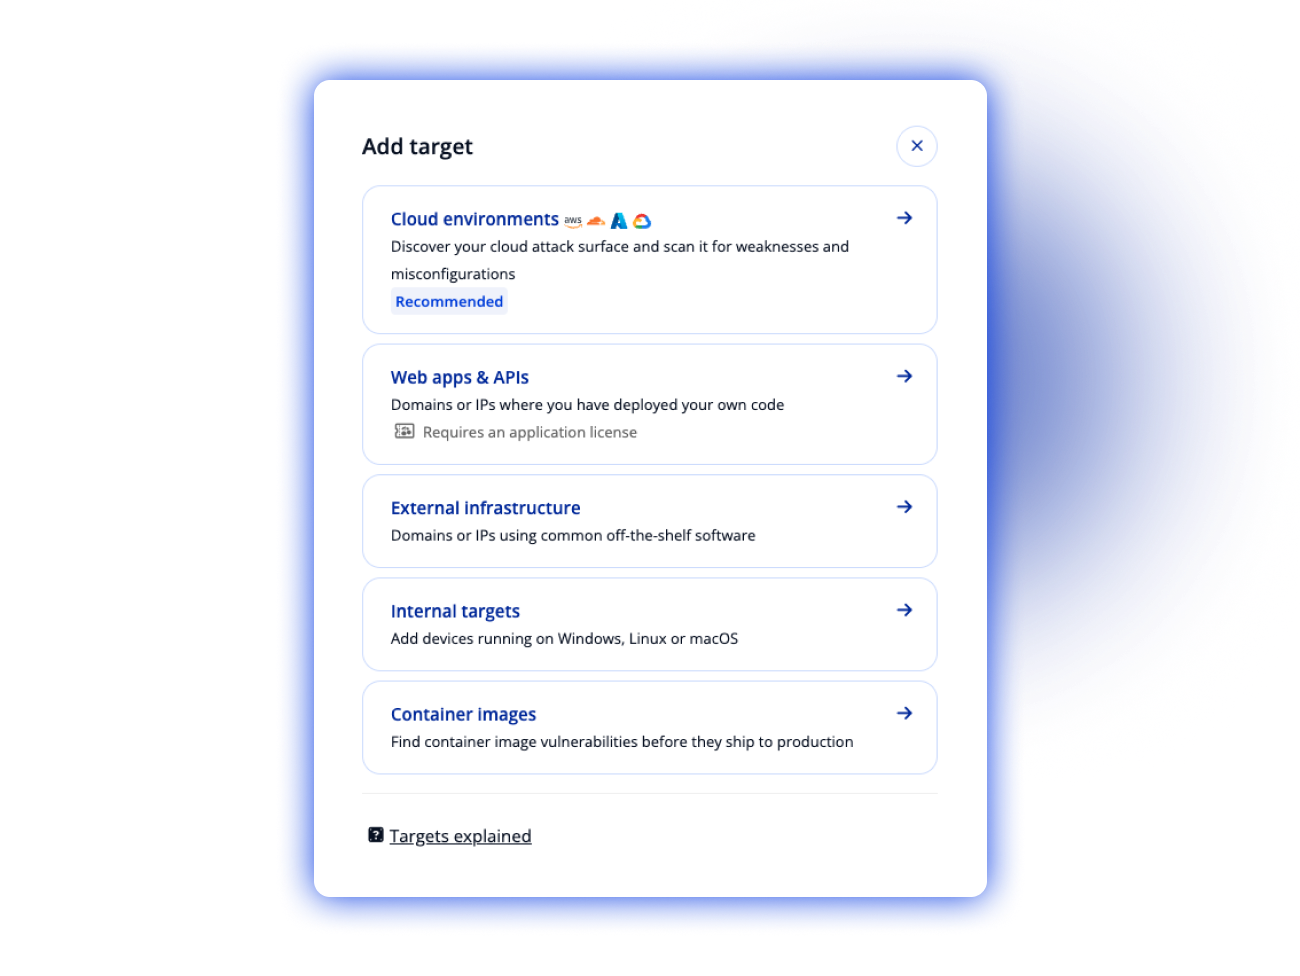
Set your initial scope by connecting your cloud accounts or adding your IP addresses and domains. Intruder takes it from here.
Auto detect unknown assets
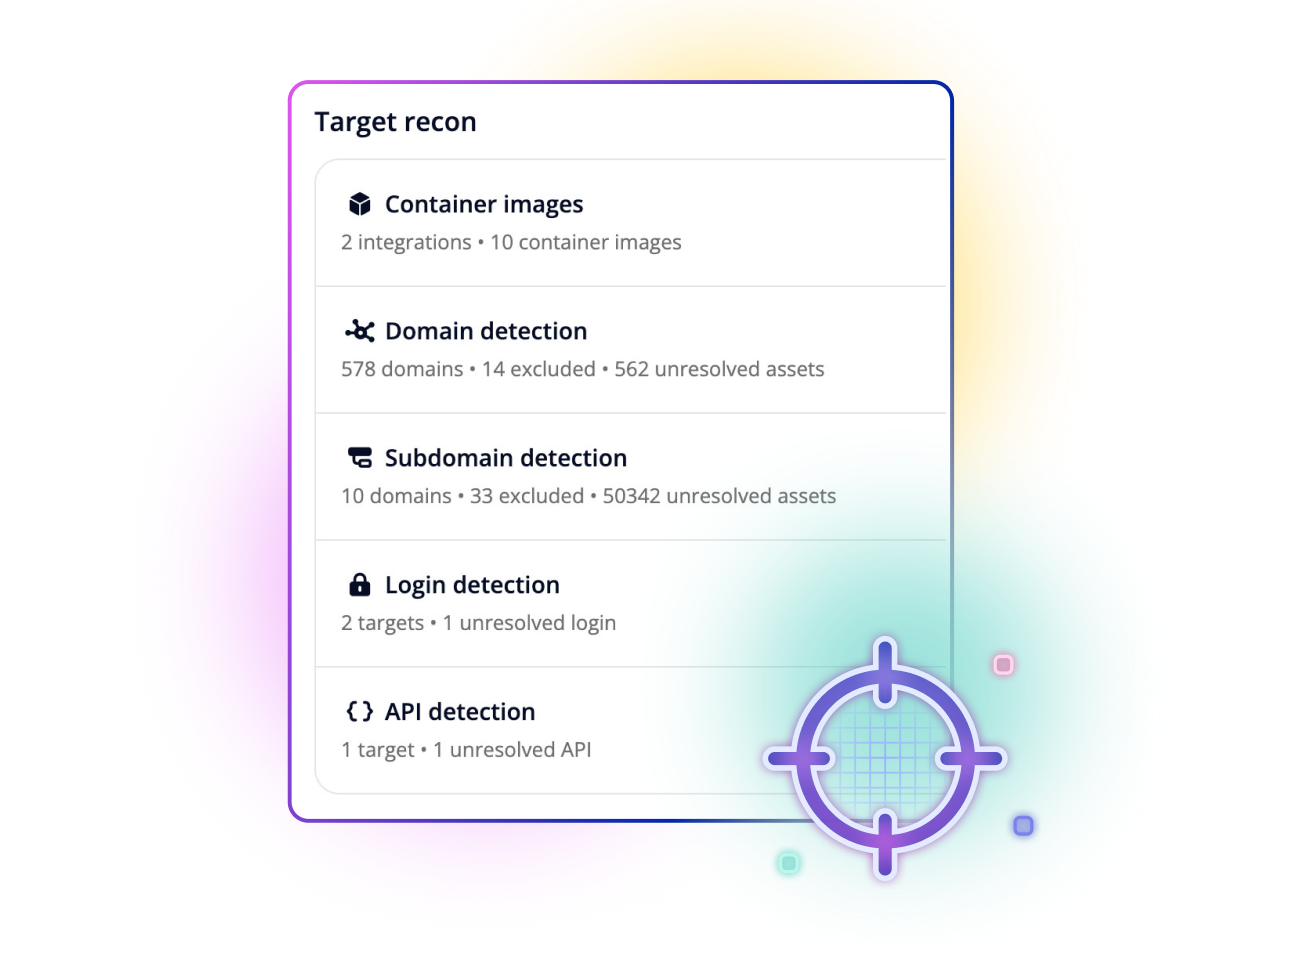
Intruder automatically discovers subdomains, related domains, login pages, and APIs across your estate. Cloud Sync continuously checks your cloud accounts and adds new services to the platform.
Continuously scan
Newly discovered assets are automatically added to your regular and proactive scans without lifting a finger. Prefer to review what's been found before scanning? You can do that too.
Find what's exposed, fix what matters, and stay ahead of new threats
External Scanning
Infrastructure Security
Attack Surface Monitoring
Respond to changes

CSPM
Daily cloud config checks

Asset Discovery
Reveal unknown targets

DAST
Secure web apps

Risk Based Prioritization
No more alert fatigue

Cyber Hygiene Reporting
Demonstrate progress

Emerging Threat Detection
Check and act fast

Container Image Scanning
Automated image discovery

Secrets Detection
Prevent leaked credentials

Website Security
140k+ checks

API Security
Test your APIs

Compliance
SOC 2, ISO, HIPAA, DORA

Internal Scanning
Secure employee devices
Our customers love Intruder





One platform. Continuous security.
Shadow IT refers to any infrastructure, services, or cloud resources running without the knowledge of your security team, like forgotten subdomains, unmanaged cloud instances, and services spun up outside standard processes. These assets go unscanned and unpatched, making them easy targets. Intruder discovers shadow IT automatically so it can be brought into your vulnerability management workflow.
Intruder discovers subdomains, related domains, login pages, APIs, and cloud services across your attack surface. Everything appears on the discovery page for you to review and add as targets for external vulnerability scanning.
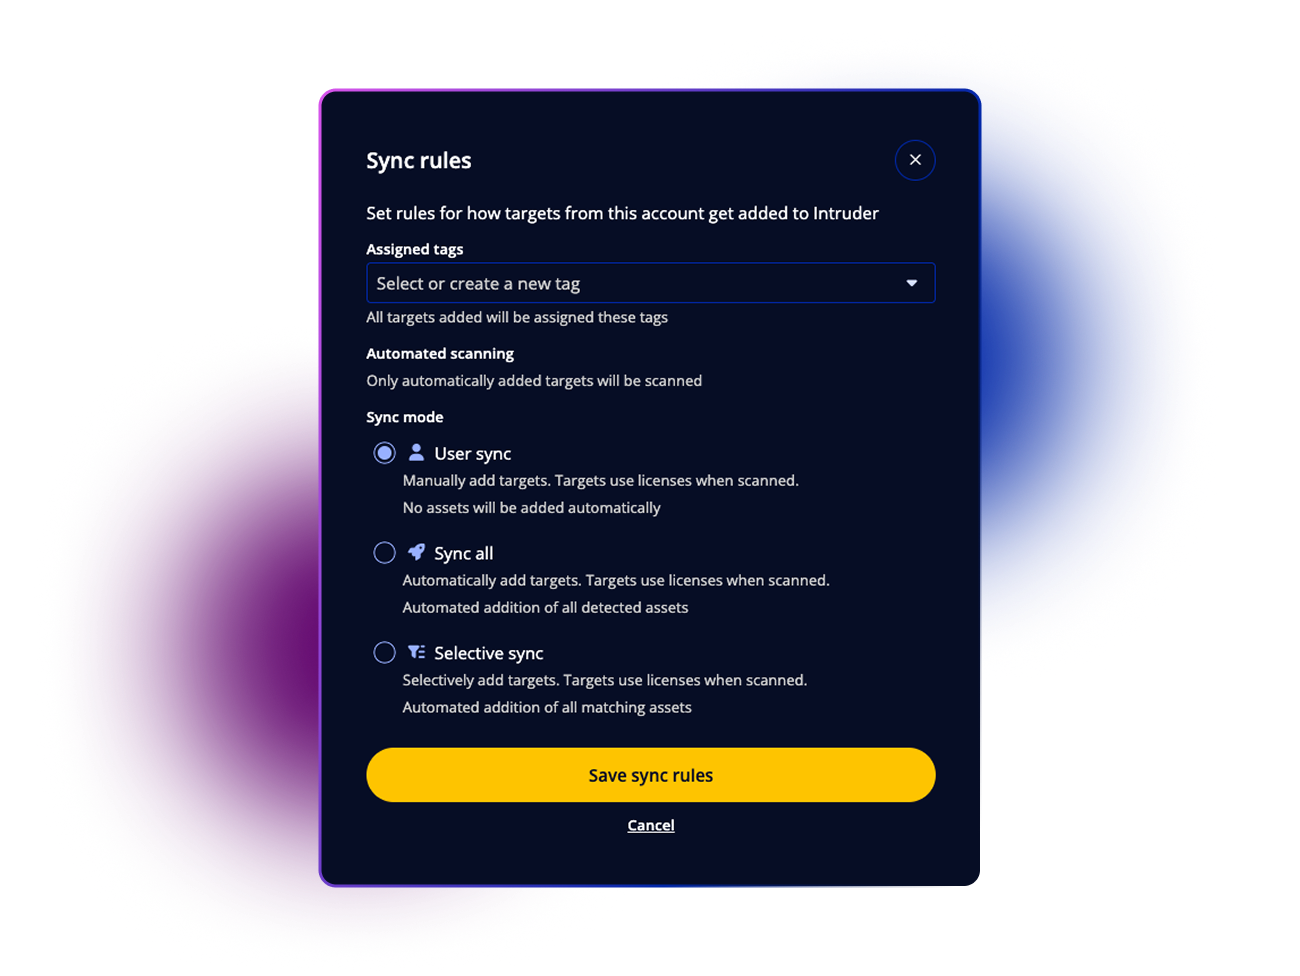
Connect your AWS, Azure, or Google Cloud account and Intruder automatically detects new services as they're exposed. You can set rules to control what's imported and enable auto-scanning so new targets are scanned as soon as they appear. See how to connect your cloud accounts.
Cloud targets sync every two hours with your connected accounts. Subdomain discovery runs weekly across all your targets. Related domain checks run whenever you add a new target. Any of these can surface assets you didn't know were exposed.