
Stop cloud misconfigurations in their tracks
Unified multi-cloud cloud security posture management (CSPM) protects against the misconfigurations that cause cloud breaches with daily checks.
Join 3,000+ companies securing their attack surface with Intruder






A single view of cloud risk
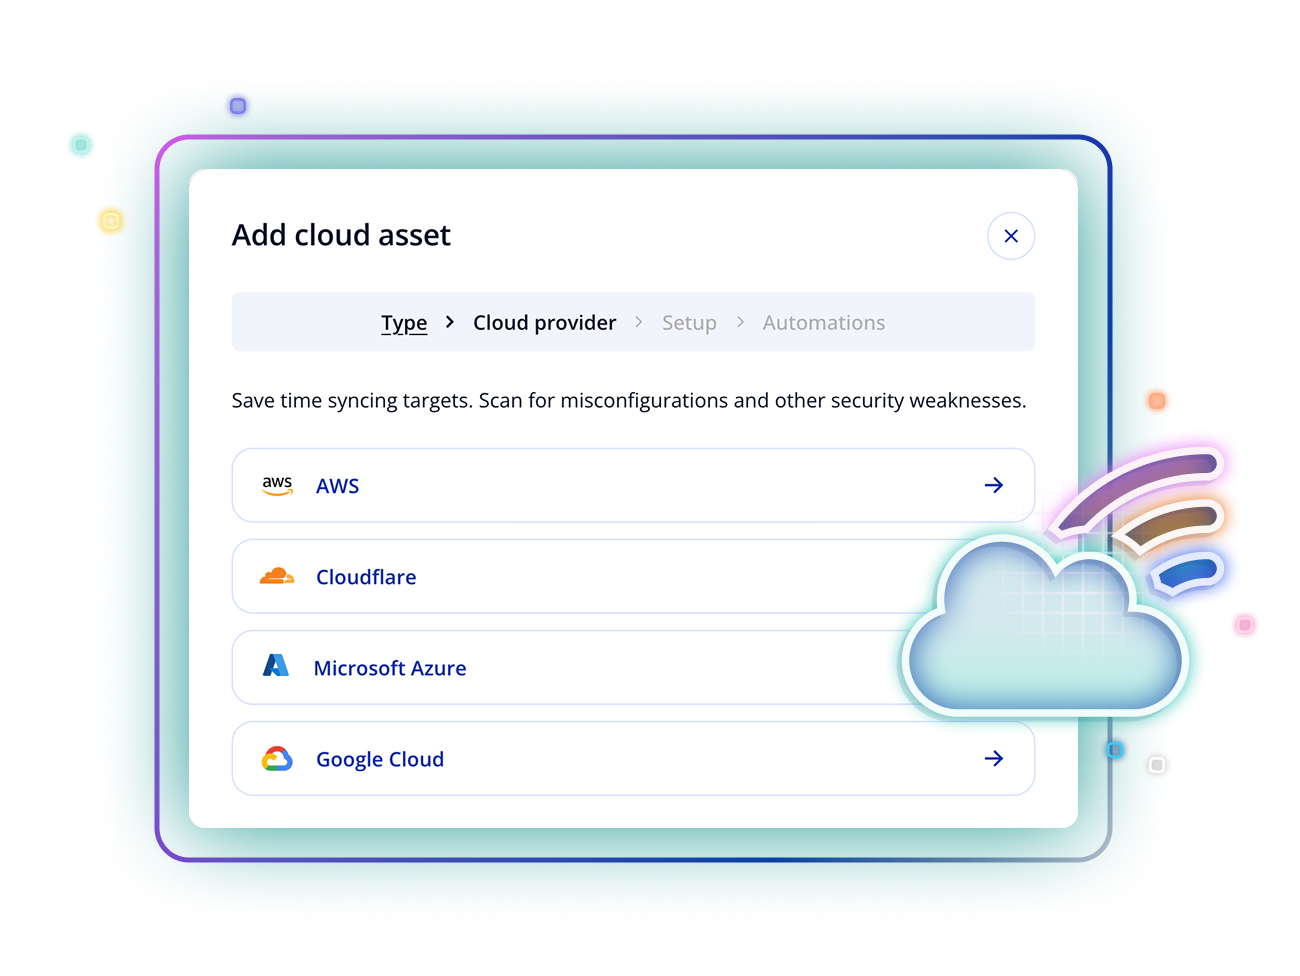
Your cloud security posture shouldn't be fragmented across separate consoles. Intruder surfaces risks across AWS, Azure, and Google Cloud in one place.
Catch misconfigurations before they’re exploited
It’s easy for misconfigured permissions, public buckets, or exposed services to creep in. Intruder’s daily CSPM checks catch them before they become a problem.
Keep up with your cloud
Someone spins up a new cloud service without telling security? Intruder detects and scans it automatically. No manual tracking, no blind spots.
See exactly what's misconfigured across your cloud. Fix what matters first.
Connect your cloud accounts

Connect your AWS, Azure, and Google Cloud accounts in minutes. No agents required, read-only access. Scans start straight away.
Daily configuration scans
Intruder runs 700+ checks daily, covering identity and access, networking, storage, logging, and permissions across every connected account. Our own custom checks run alongside industry-standard benchmarks.
Fix what matters first
Results are prioritized by severity with step-by-step remediation guidance for each issue. Track fixes in Jira, ServiceNow, GitHub, and more.
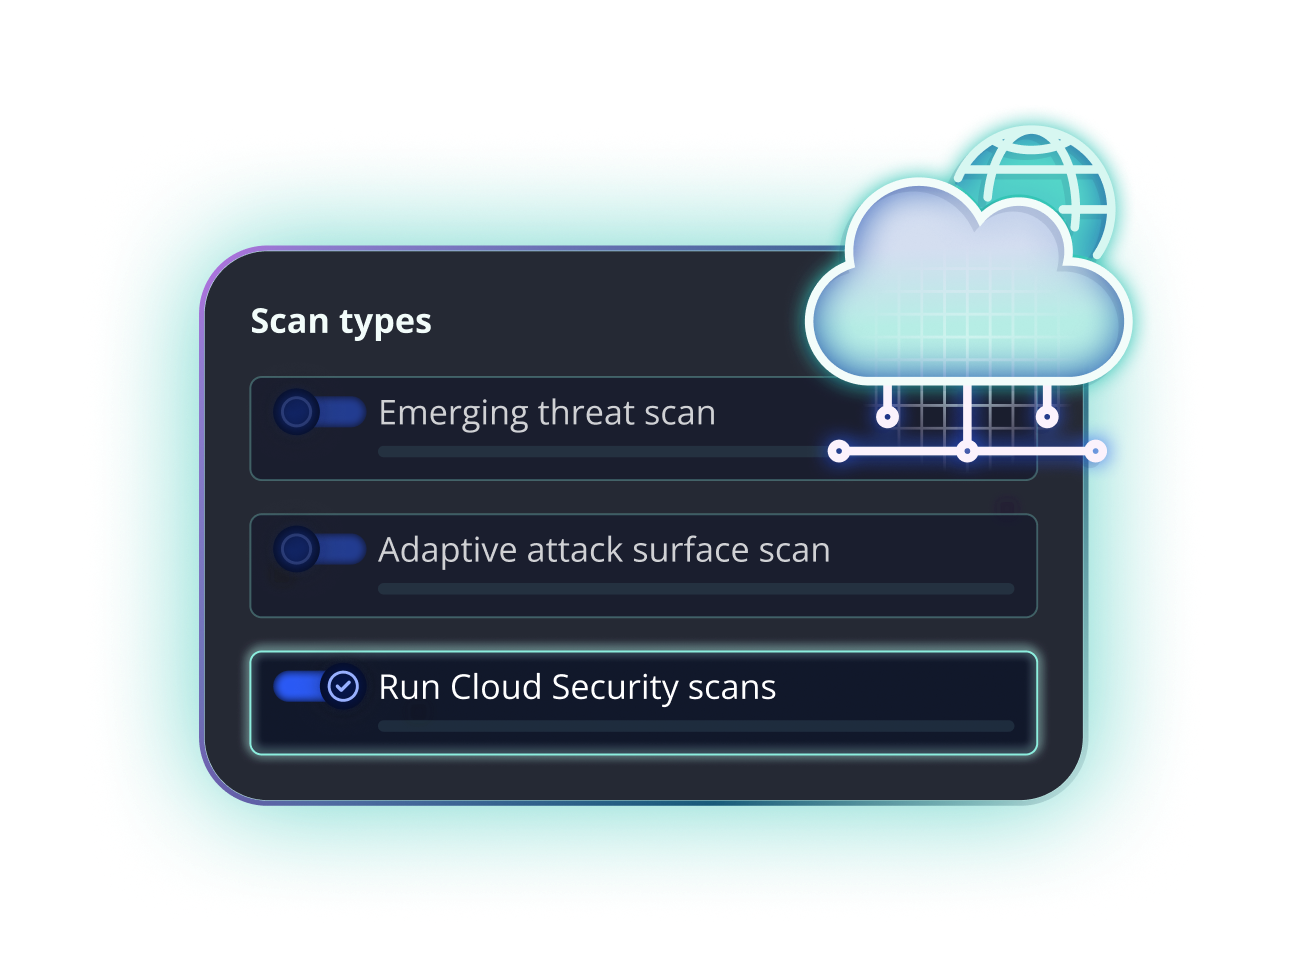
Find what's exposed, fix what matters, and stay ahead of new threats
External Scanning
Infrastructure Security
Attack Surface Monitoring
Respond to changes

CSPM
Daily cloud config checks

Asset Discovery
Reveal unknown targets

DAST
Secure web apps

Risk Based Prioritization
No more alert fatigue

Cyber Hygiene Reporting
Demonstrate progress

Emerging Threat Detection
Check and act fast

Container Image Scanning
Automated image discovery

Secrets Detection
Prevent leaked credentials

Website Security
140k+ checks

API Security
Test your APIs

Compliance
SOC 2, ISO, HIPAA, DORA

Internal Scanning
Secure employee devices
Our customers love Intruder





One platform. Continuous security.
CSPM (Cloud Security Posture Management) is the automated monitoring of cloud accounts for misconfigurations, insecure permissions, exposed secrets, and compliance gaps. Intruder runs CSPM checks daily across AWS, Azure, and Google Cloud, with results prioritized by risk and step-by-step guidance on how to fix each issue.
Intruder integrates with Jira, GitHub, GitLab, Azure DevOps, and ServiceNow for issue tracking, Slack and Microsoft Teams for alerts, Drata and Vanta for compliance, and Microsoft Sentinel for SIEM. See all our integrations.
Intruder runs over 700 configuration checks daily covering identity and access, networking, storage, logging, and permissions. Checks include misconfigured resources, overly broad public access, insecure permissions, and gaps in the shared responsibility model where default cloud settings may leave your side exposed. Custom checks built by Intruder's security team run alongside industry-standard benchmarks.
Native tools like AWS Security Hub, Azure Defender for Cloud, and GCP Security Command Center only cover their own provider. If you're running multi-cloud, that means three separate consoles and three different risk views. Intruder surfaces misconfigurations across all three in a single prioritized list alongside vulnerabilities and attack surface exposures.