
Website vulnerability scanning that keeps up with your site
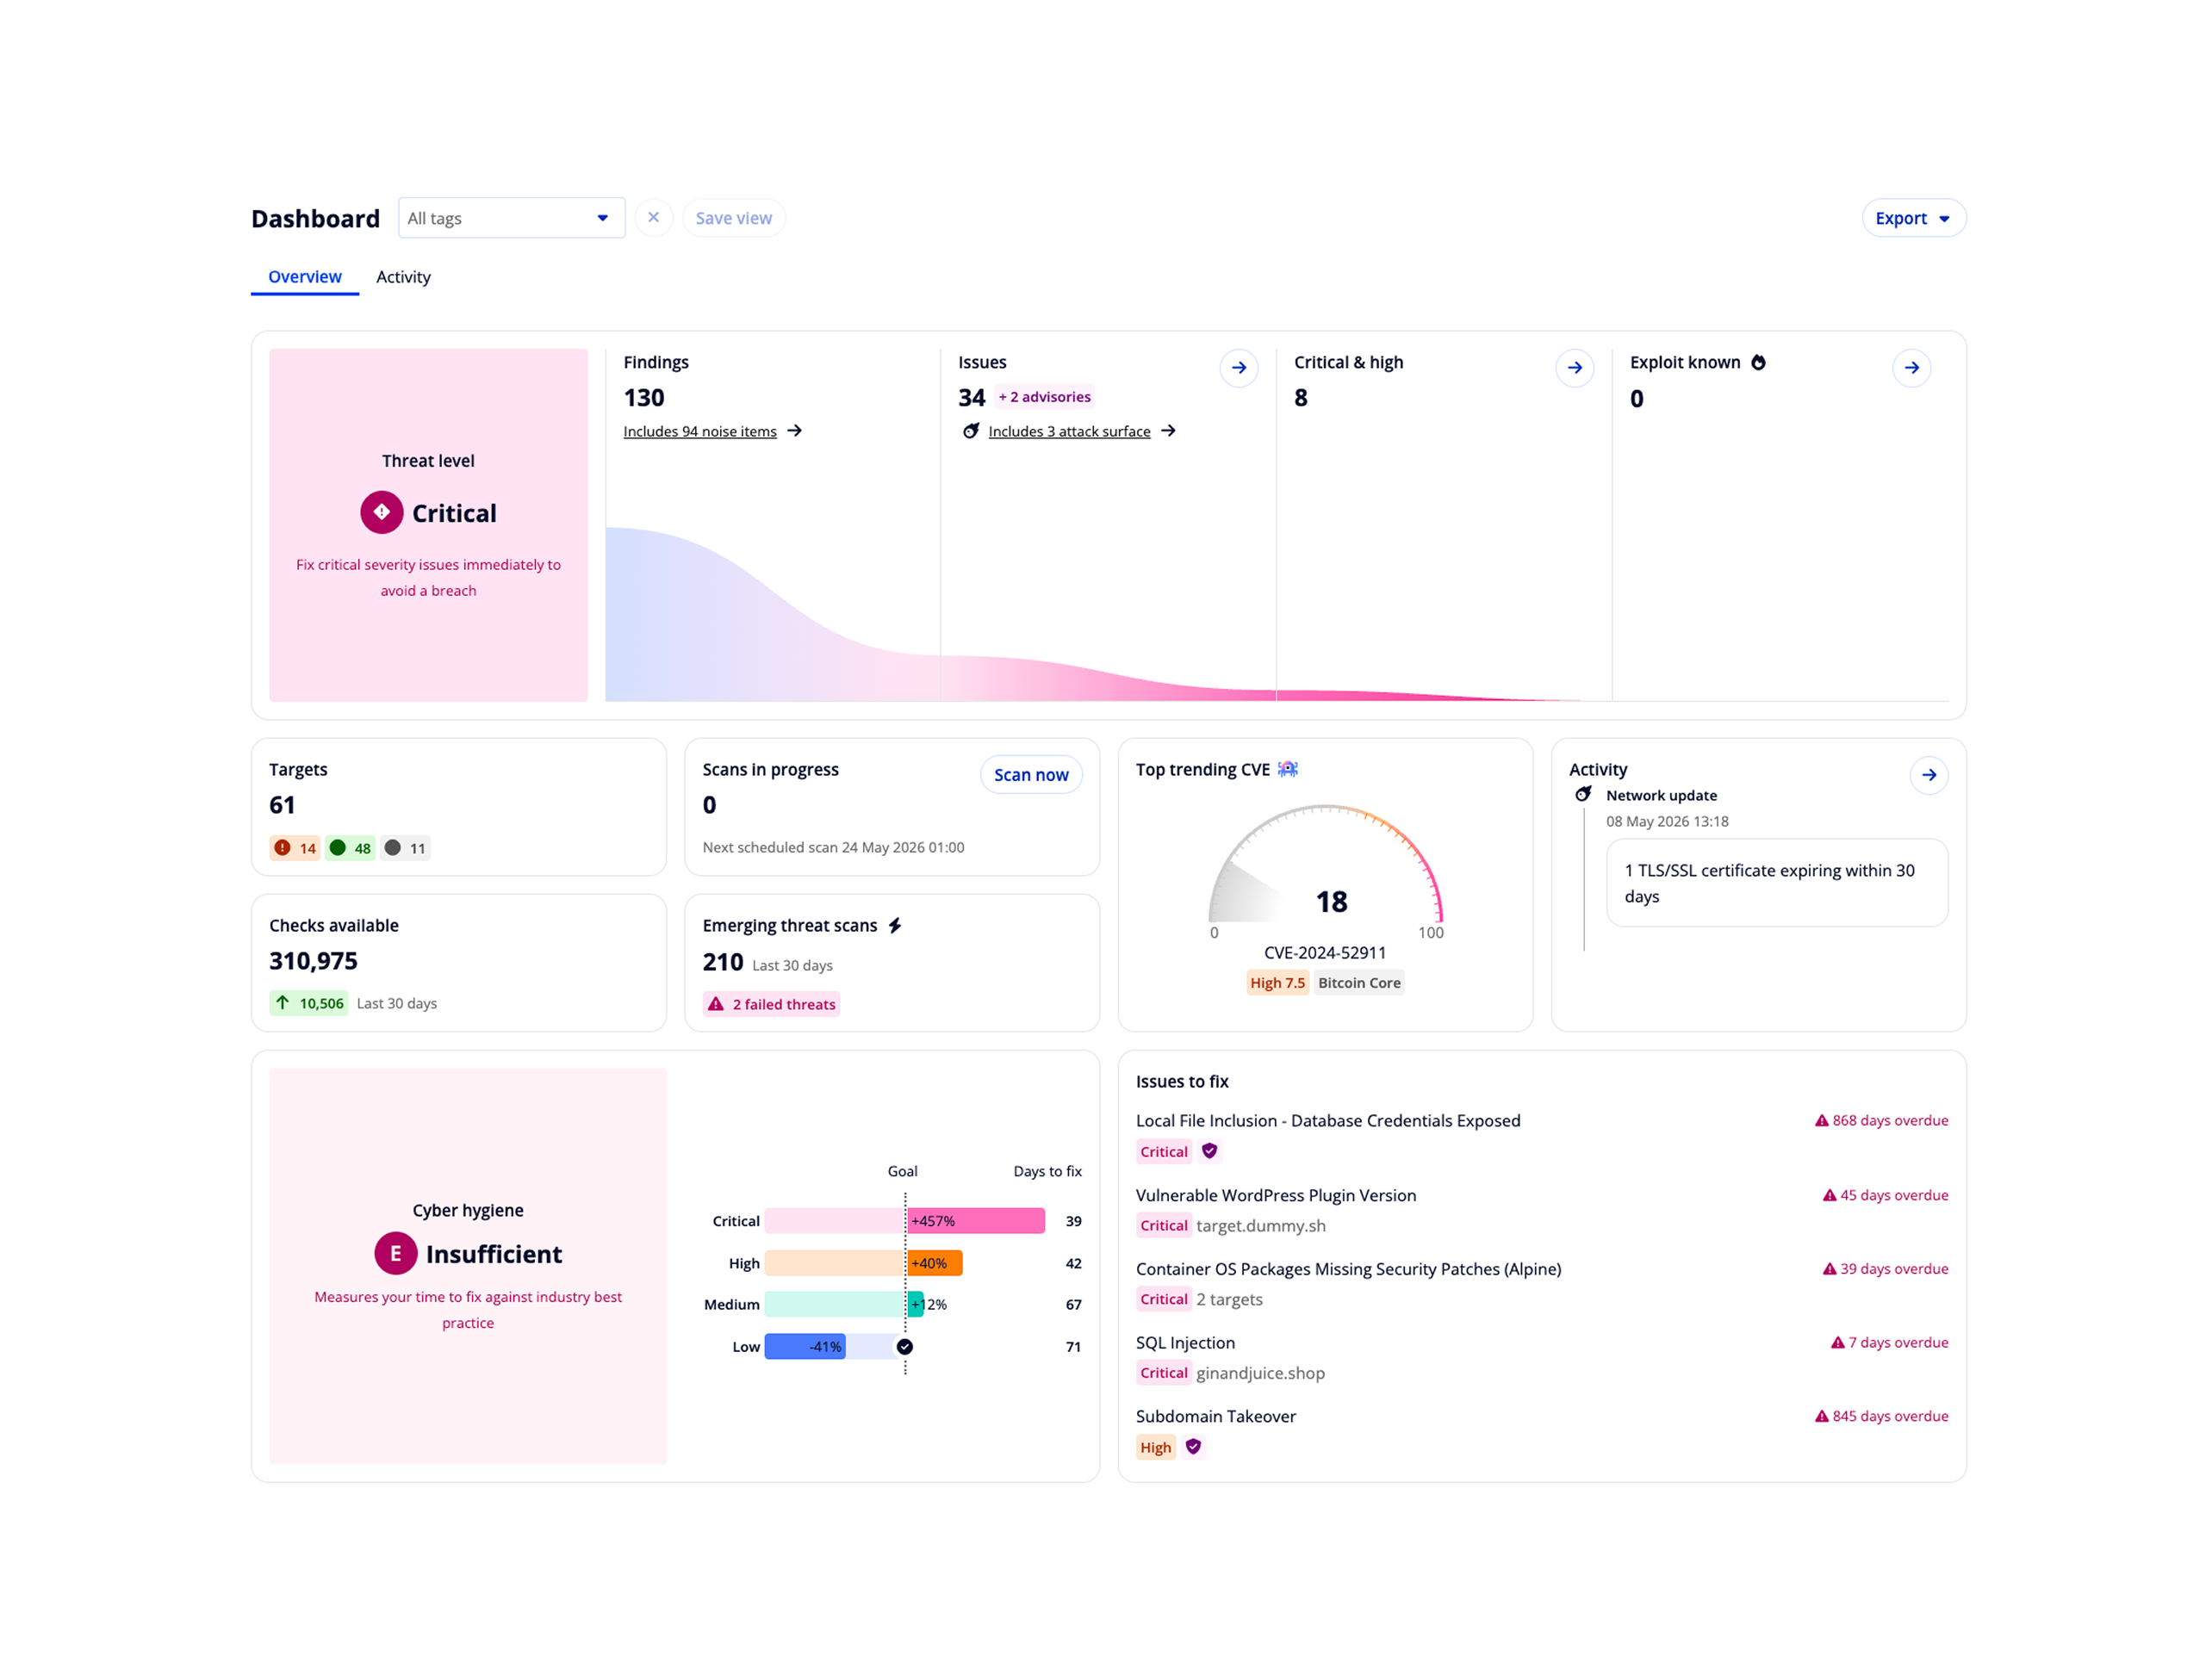
Plugins get updated, themes get swapped, and new pages go live every week. Intruder scans your website and the server it runs on, so you know when a change introduces a vulnerability and how to fix it.
Join 3,000+ companies securing their attack surface with Intruder






Catch vulnerable plugins and themes
Over 30,000 WordPress checks cover core, plugins, and themes. If an update introduces a vulnerability, Intruder flags it with remediation advice.
Scan the pages behind your login
Authenticated scanning covers account pages, dashboards, and checkout, not just the public pages of your site.
Find out if a new vulnerability affects you
When a new vulnerability is disclosed, emerging threat scans check your site automatically, without waiting for the next scheduled scan.
Continuous security for your websites
Get started in minutes

Add your website by URL or IP address, plus login details if you want to scan authenticated pages. Intruder works with WordPress, Drupal, Joomla, Squarespace, and single-page applications.
Protect your site and the server behind it
Each scan checks your site for issues like SQL injection and cross-site scripting, and checks the server hosting it for outdated software, missing patches, and misconfigurations.
Fix and confirm
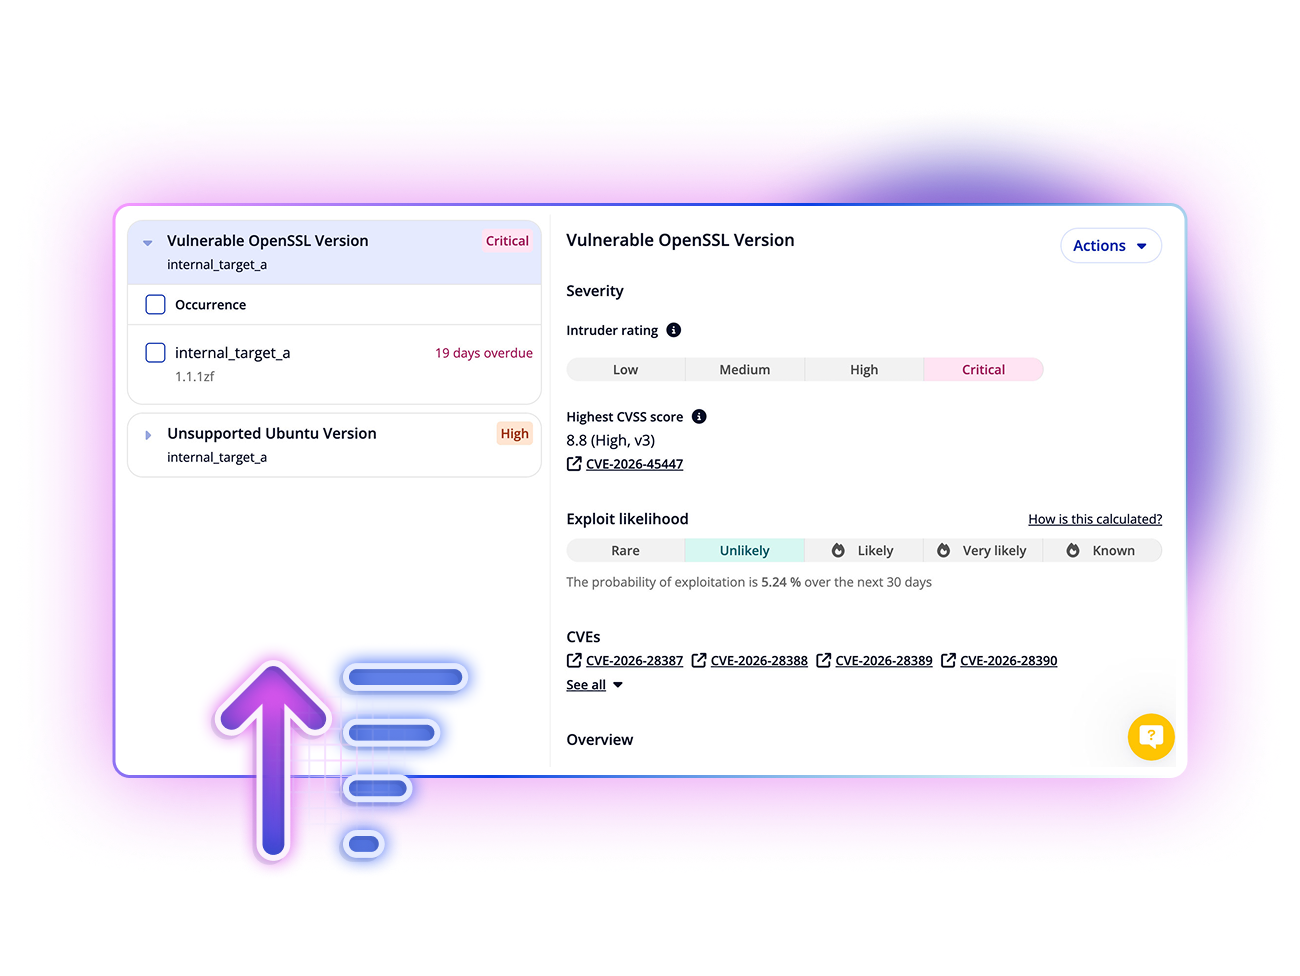
Results are prioritized by risk, with remediation advice for each issue. Send them to Jira, GitHub, or Azure DevOps, then rescan to confirm the fix worked.
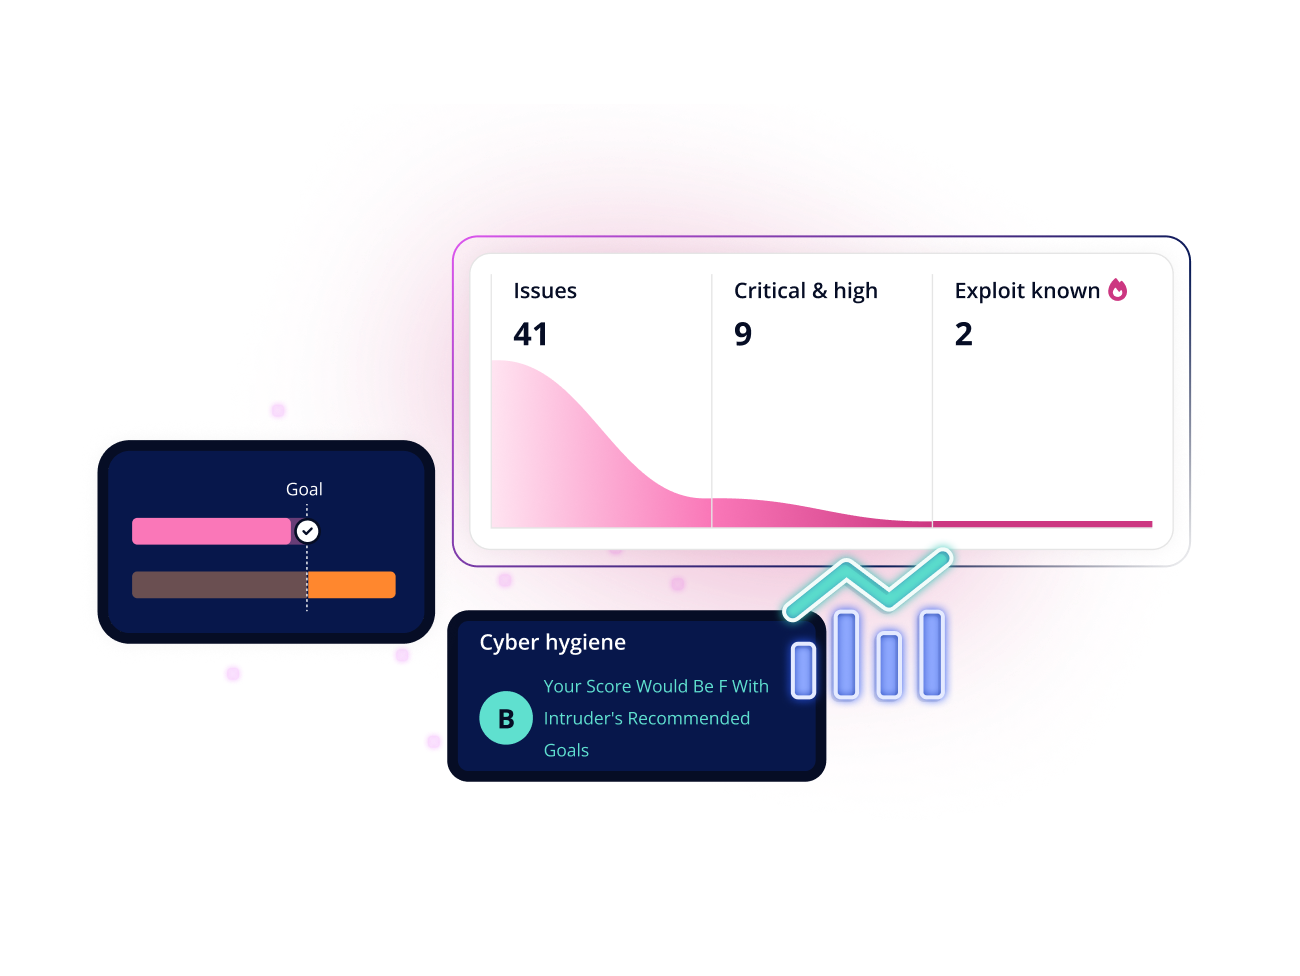
Find what's exposed, fix what matters, and stay ahead of new threats
External Scanning
Infrastructure Security
Attack Surface Monitoring
Respond to changes

CSPM
Daily cloud config checks

Asset Discovery
Reveal unknown targets

DAST
Secure web apps

Risk Based Prioritization
No more alert fatigue

Cyber Hygiene Reporting
Demonstrate progress

Emerging Threat Detection
Check and act fast

Container Image Scanning
Automated image discovery

Secrets Detection
Prevent leaked credentials

Website Security
140k+ checks

API Security
Test your APIs

Compliance
SOC 2, ISO, HIPAA, DORA

Internal Scanning
Secure employee devices
Our customers love Intruder





One platform. Continuous security.
Intruder integrates with Jira, GitHub, GitLab, Azure DevOps, and ServiceNow for issue tracking, Slack and Microsoft Teams for alerts, Drata and Vanta for compliance, and Microsoft Sentinel for SIEM. See all our integrations.
Yes. Intruder runs over 30,000 WordPress-specific checks covering core, plugins, and themes. If an update introduces a known vulnerability, Intruder flags it with remediation advice.
Each scan checks your site for application-level issues like SQL injection and cross-site scripting, and checks the server hosting it for outdated software, missing patches, and encryption weaknesses. WordPress sites also get plugin, theme, and core checks. Learn more about web app scanning.
Yes. Add your login details and Intruder scans authenticated pages like account dashboards, checkout flows, and admin panels, not just the public-facing pages of your site. See the authentication setup guides.