
Catch vulnerable containers before they reach production
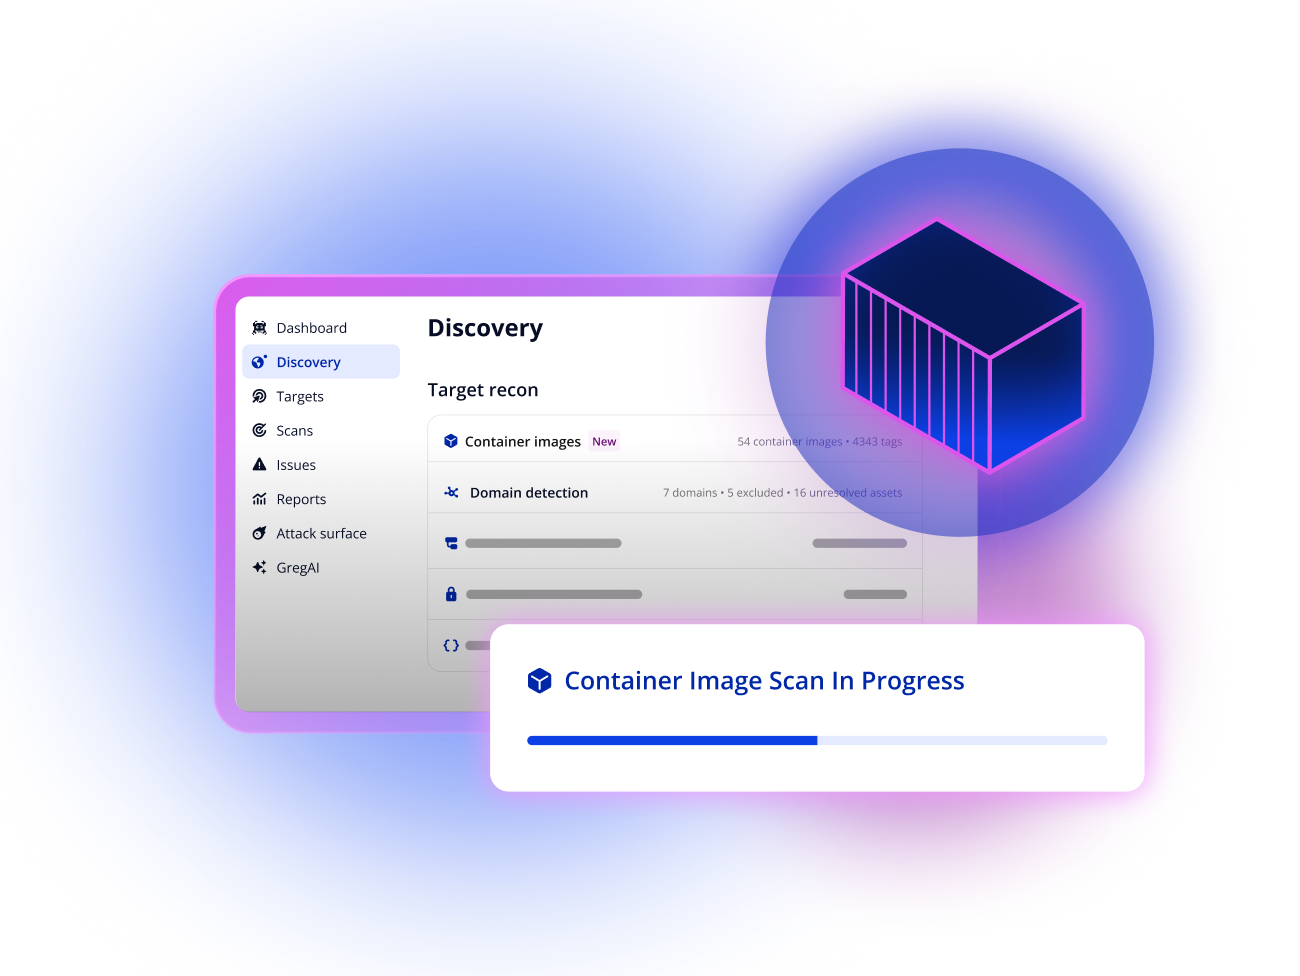
Agentless, registry level container image scanning checks for known CVEs, so you catch risks before they ship.
Join 3,000+ companies securing their attack surface with Intruder






No agents required
Intruder delivers an agentless experience by connecting to AWS, Azure, Google Cloud, and DockerHub container registries. No deploying to nodes or debugging failures.
Scan containers everywhere they run
Containers don’t just run in Kubernetes. Agent-based approaches can't reach managed services like Lambda or ECS. Intruder scans at the registry level so every image is covered.
Limit the noise
Don’t scan old versions if you don’t need to. Point Intruder at the tags that reflect what's deployed. Push a new version and the old results are retired.
Every image found, scanned, and prioritized
Connect container registries

Integrate your AWS, Azure, or Google Cloud account and your container images, including Docker images, show up in your discovery view.
Daily container image scans
Specify the tags you want to monitor to set your scan targets. First results come back in under five minutes, and the image is rescanned every 24 hours.
Prioritize and fix
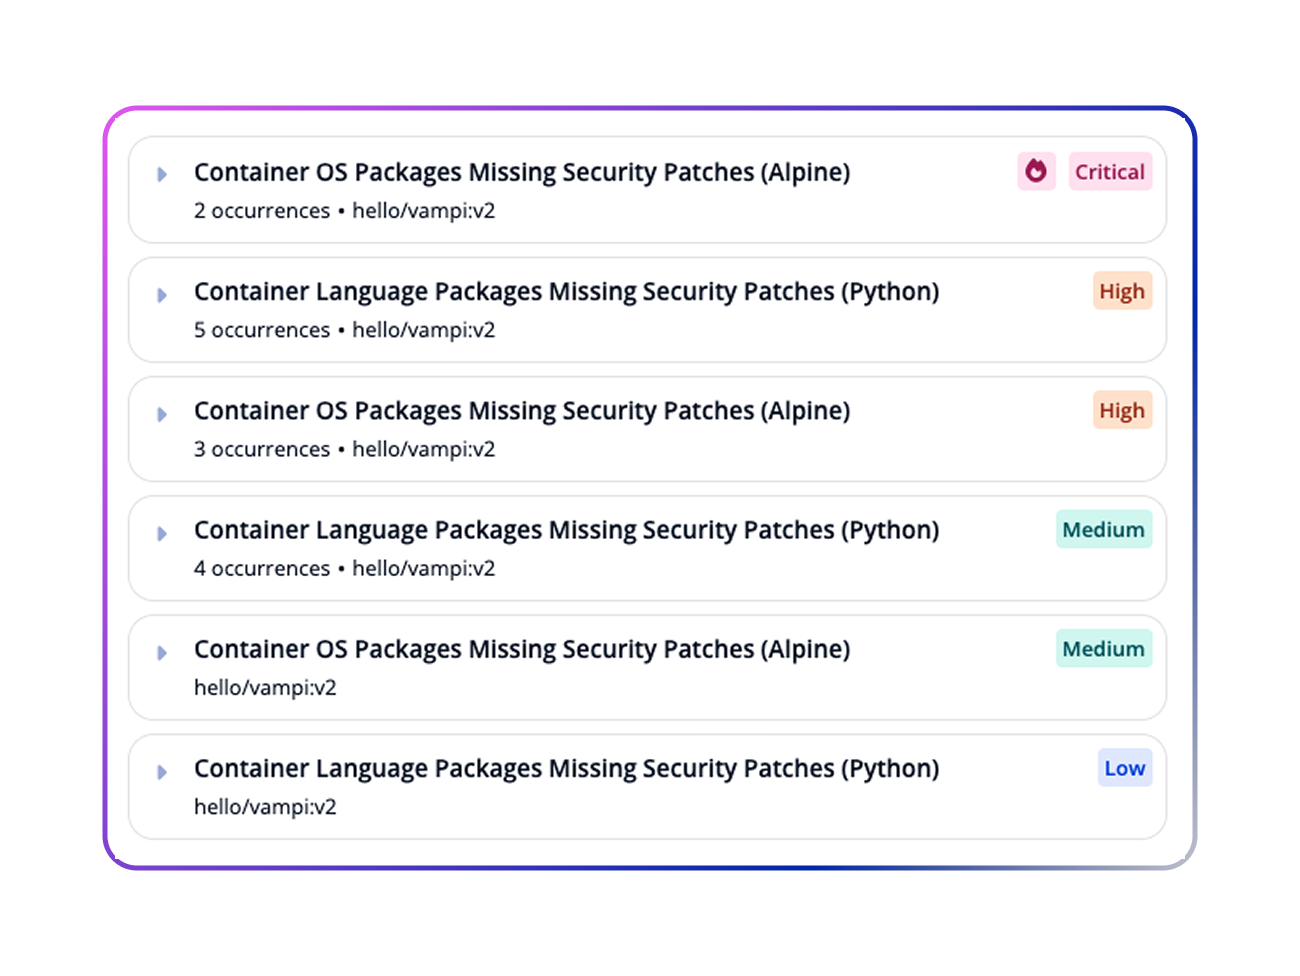
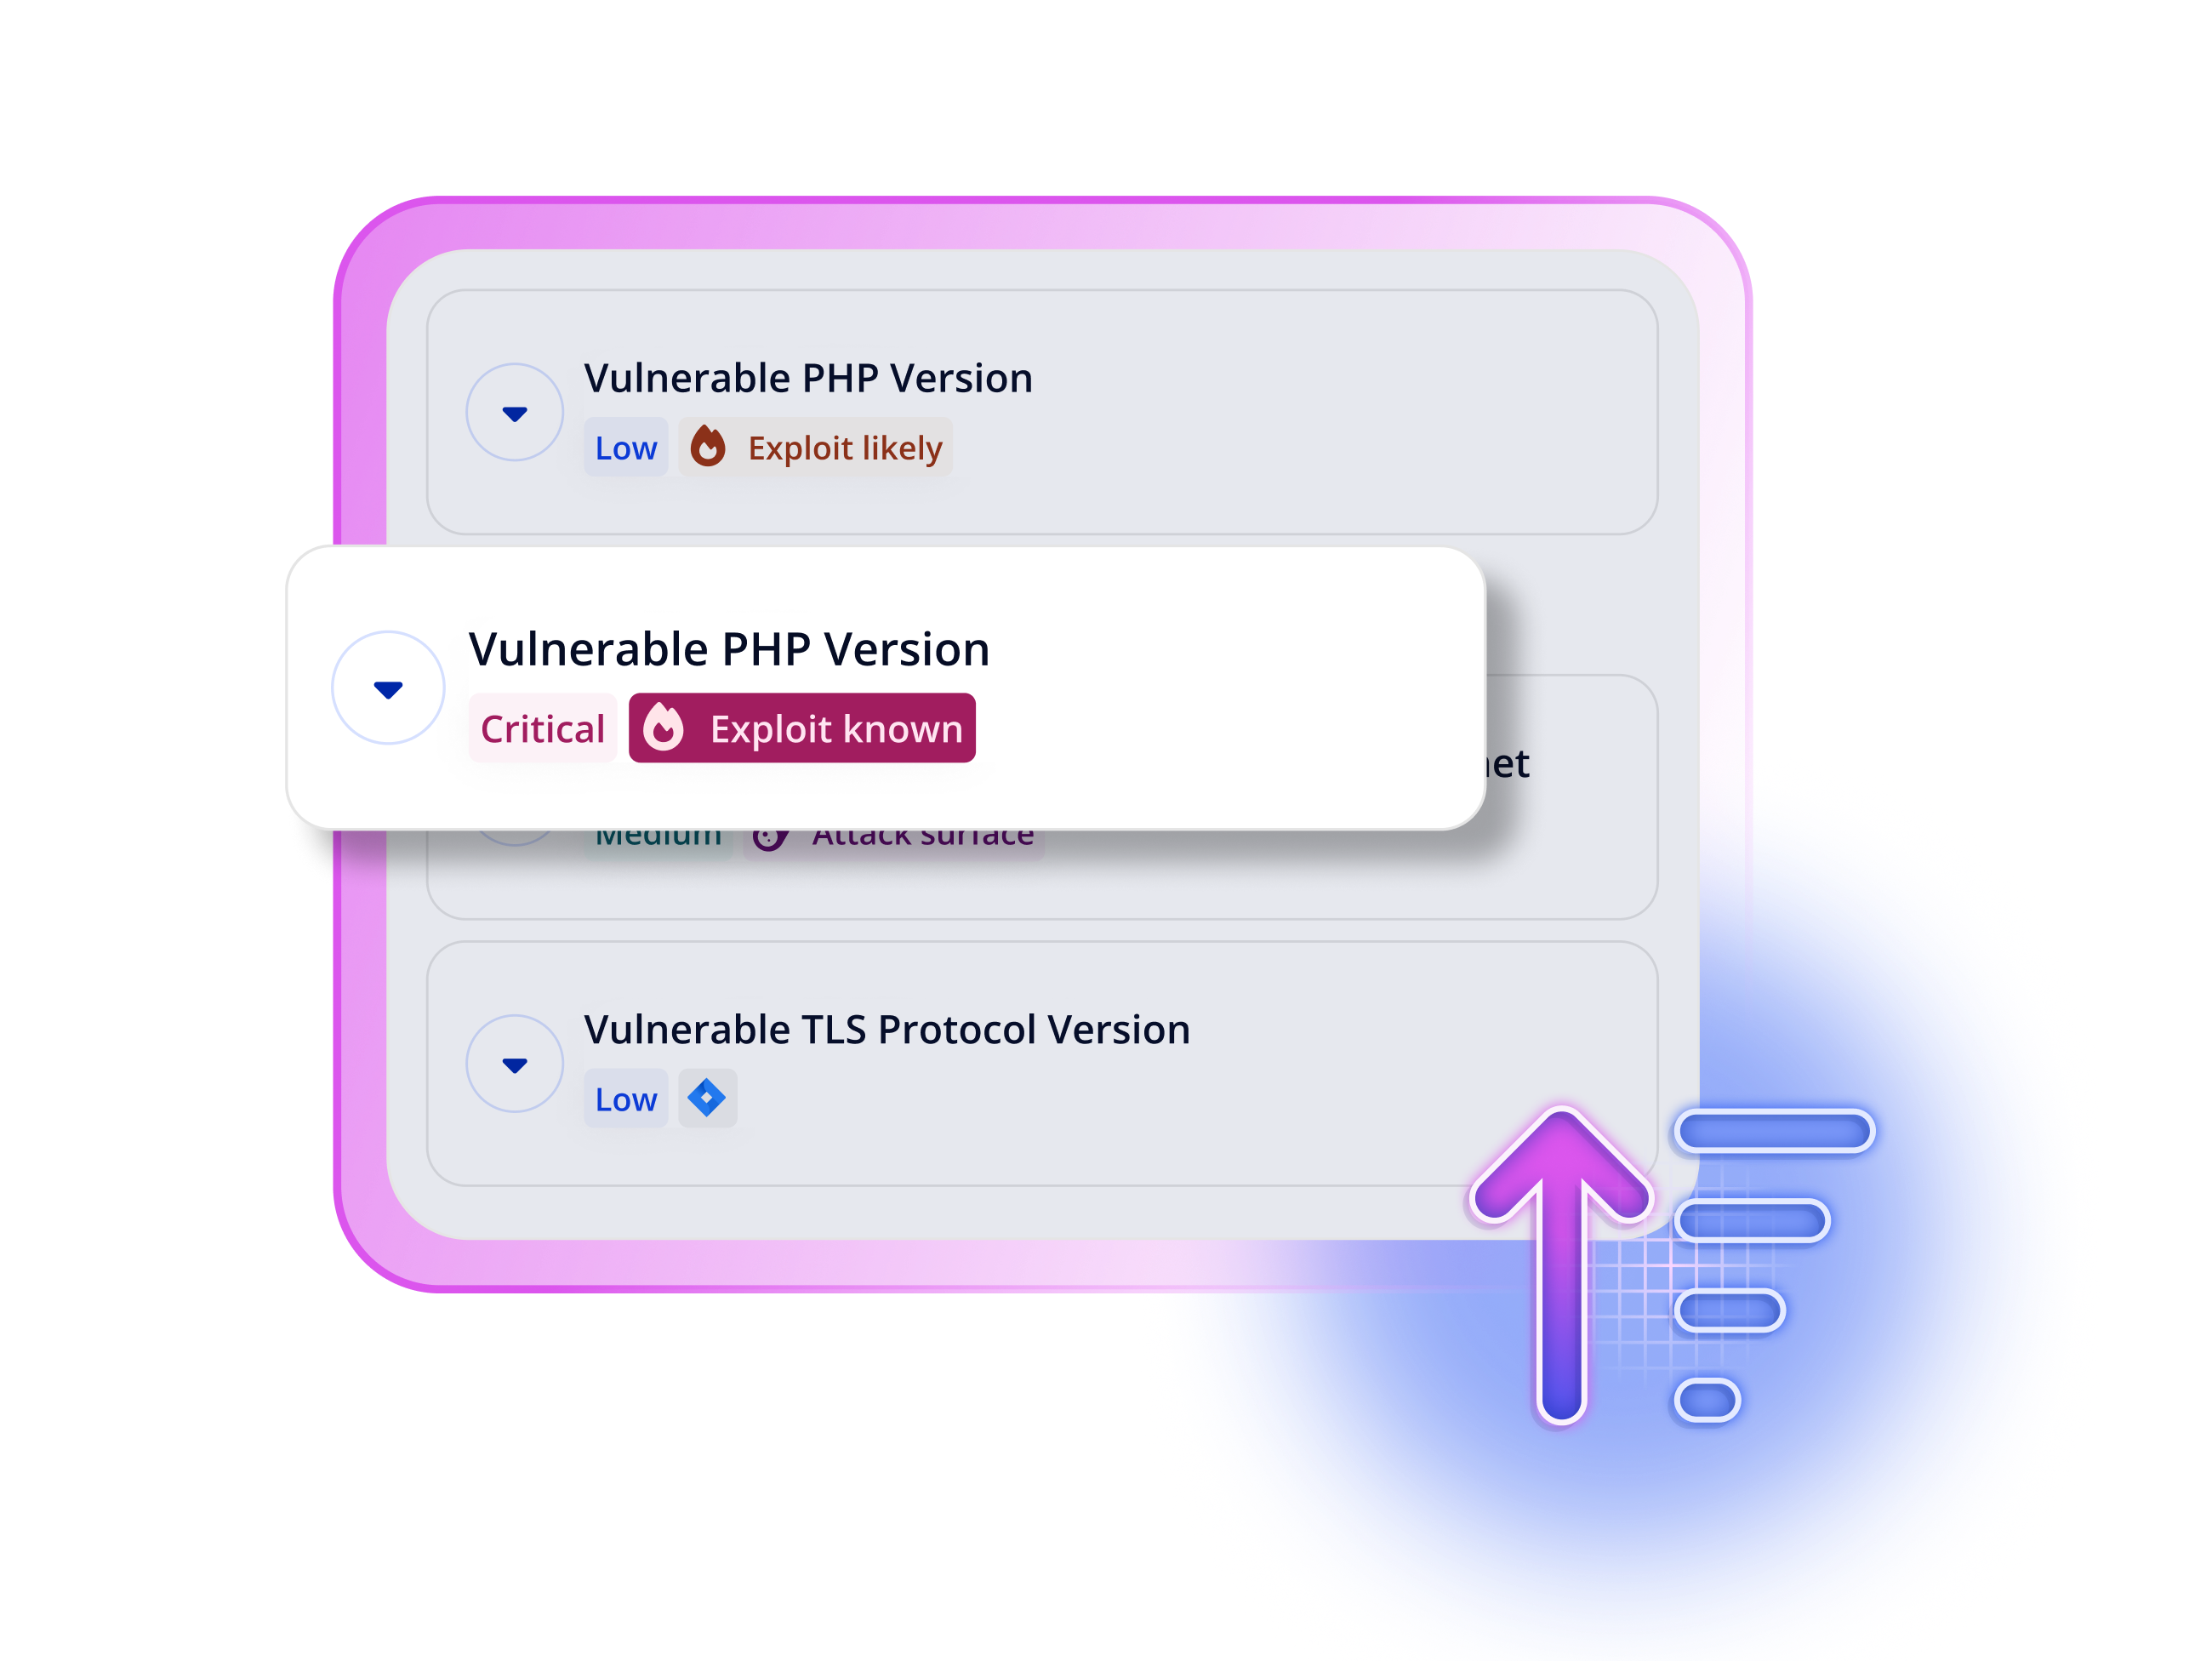
Findings appear alongside the rest of your vulnerabilities and attack surface issues, ranked by exploitability and severity, with guidance on how to fix each one.
Find what's exposed, fix what matters, and stay ahead of new threats
External Scanning
Infrastructure Security
Attack Surface Monitoring
Respond to changes

CSPM
Daily cloud config checks

Asset Discovery
Reveal unknown targets

DAST
Secure web apps

Risk Based Prioritization
No more alert fatigue

Cyber Hygiene Reporting
Demonstrate progress

Emerging Threat Detection
Check and act fast

Container Image Scanning
Automated image discovery

Secrets Detection
Prevent leaked credentials

Website Security
140k+ checks

API Security
Test your APIs

Compliance
SOC 2, ISO, HIPAA, DORA

Internal Scanning
Secure employee devices
Our customers love Intruder





One platform. Continuous security.
Intruder integrates with Jira, GitHub, GitLab, Azure DevOps, and ServiceNow for issue tracking, Slack and Microsoft Teams for alerts, Drata and Vanta for compliance, and Microsoft Sentinel for SIEM. See all our integrations.
Intruder discovers and scans container images from AWS ECR, Google Cloud Artifact Registry, Azure Container Registry, and Docker Hub. Connect your cloud account or Docker Hub and your images appear automatically in the discovery view. See the setup guide.
Every container image target is scanned at least once every 24 hours to catch newly disclosed CVEs. Intruder also checks every 5 minutes for new image versions. If you push a new tag that matches your rule, a scan kicks off automatically. More on how scanning works.
Registry-level scanning gives you broader, more consistent coverage. Runtime agents only see what's running inside a specific cluster, miss containers on managed services like ECS or Cloud Run, and need to be deployed and maintained in every environment. Scanning at the registry covers every image regardless of where it runs. Read more about registry vs. runtime scanning.
No. Intruder connects to your container registries using read-only access and scans images at the registry level - nothing is deployed into your infrastructure. See setup instructions.